30초 요약
In April 2026, Matthew Berman discusses Anthropic's Claude Mythos Preview and Project Glasswing, a limited-access initiative to help secure critical software. He emphasizes reported benchmark gains and security findings and speculates about why the model was not generally released. Anthropic's scores and vulnerability counts are company-reported, not a universal ranking or independent proof of every claim. Its stated concern is the potential misuse of powerful cyber capabilities; Berman's suggestion that hardware constraints prevented release is speculation.
- 1A restricted previewBerman reacts to Anthropic's announcement and calls Mythos Preview exceptionally capable. The model was made available to selected partners rather than generally released.
- 2Benchmark claimsAnthropic reports 93.9% versus 80.8% on SWE-bench Verified and 77.8% versus 53.4% on SWE-bench Pro, comparing Mythos Preview with Opus 4.6.
- 3Project GlasswingAnthropic formed a collaboration with technology and security organizations to identify and fix vulnerabilities in critical software.
- 4Reported vulnerability discoveriesThe company attributes discoveries in operating systems and browsers to the model, including an old OpenBSD bug and an FFmpeg vulnerability.
핵심 정리
- Anthropic announced Claude Mythos Preview and Project Glasswing on April 7, 2026, initially restricting the model to selected security partners.
- Anthropic reported improved scores over Claude Opus 4.6 on selected coding evaluations; results depend on the test configuration.
- The company says the model found thousands of previously unknown vulnerabilities, including issues in OpenBSD, FFmpeg and Linux.
- The cited Terminal-Bench 2.0 figures are 82.0% versus 65.4%, a 16.6-point difference, rather than 20 points.
- Restricted access was connected to cybersecurity risks; the video does not establish that a GPU shortage made public release impossible.
챕터별로 다듬은 전문 읽기
A new model and benchmark claims
Berman introduces Mythos Preview and cites large reported gains in coding benchmarks. These are provider-reported comparisons under specific settings.
Anthropic has announced Claude Mythos Preview, and I am struck by the coding benchmark numbers. In the company's comparison with Claude Opus 4.6, Mythos scores 93.9% versus 80.8% on SWE-bench Verified and 77.8% versus 53.4% on SWE-bench Pro. These are Anthropic-reported results under particular evaluation settings; they are not proof that the model is the best at every task ([Project Glasswing](https://www.anthropic.com/glasswing)).
I also describe a 20-point improvement on Terminal-Bench. Anthropic's displayed Terminal-Bench 2.0 results are 82.0% for Mythos Preview and 65.4% for Opus 4.6, a 16.6-percentage-point difference. Benchmark version, time limits and evaluation harness matter when comparing results.
Anthropic is not generally releasing this preview. Boris Cherny, who leads Claude Code, describes a controlled preview for cyber defenders instead of a broad release. I speculate that the model's size and a GPU crunch might also make it difficult to serve, but the video provides no evidence that this was the reason for the restriction.
Limited access and Project Glasswing
He discusses Anthropic's restricted preview and its concern about misuse. He also speculates that infrastructure constraints might have affected release.
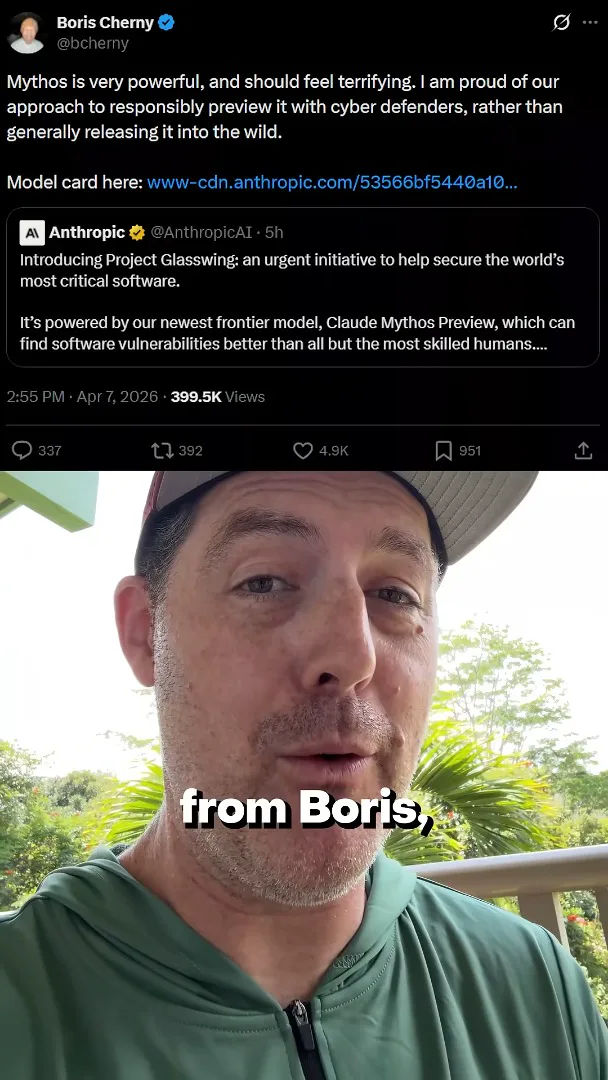
The company says it formed Project Glasswing because of the model's observed cybersecurity capabilities, bringing together selected technology and security partners to help secure critical software. Anthropic warns that models capable of discovering and exploiting vulnerabilities could be useful to attackers as well as defenders. Its statement about surpassing most human security researchers is the company's assessment, not an independently established universal ranking.
Reported security findings
Berman reviews Anthropic's claims about previously unknown vulnerabilities. The short video ends with examples involving OpenBSD, FFmpeg and Linux.
Anthropic says Mythos Preview found thousands of previously unknown vulnerabilities, including issues across major operating systems and web browsers. The company describes a 27-year-old OpenBSD vulnerability, a 16-year-old FFmpeg issue and Linux kernel findings; it says some vulnerabilities were found and exploit chains developed autonomously. These are reported findings, and the published examples include fixes and technical context ([Anthropic's security assessment](https://www.anthropic.com/research/mythos-preview)).
Anthropic cautions that similar capabilities may spread beyond organizations committed to safe deployment, with possible consequences for public safety and national security. I agree that the risk deserves attention, even though I also see Anthropic as especially cautious about releasing models. The severity and timing of future harm remain uncertain.
같은 채널의 다른 글
 34:21EN
 Matthew Berman· 2026년 10월 27일Matthew Berman Examines Anthropic’s IPO Filing, AI Growth and GovernanceMatthew Berman, Sam Altman · Forward FutureThe presenter reviews the S-1’s financial metrics, compute strategy and voting structure while questioning the tension between rapid AI development and safety.
 0:36ENMatthew Berman· 2026년 10월 25일Kimi K3.1 and a Rubik’s Cube Solver DemonstrationMatthew Berman · Forward FutureMatthew Berman shows a scrambled virtual cube being solved and gives the Kimi K3.1 test a favorable assessment.
 0:21ENMatthew Berman· 2026년 10월 24일An AI-Generated Kimi Benchmark Chart Used Invented ScoresMatthew Berman · Forward FutureMatthew Berman asks for a graph of Kimi K3.1 Pro benchmarks, then discovers that the displayed figures are illustrative placeholders.
 25:50ENMatthew Berman· 2026년 10월 24일Kimi K3.1 Pro Tested: Strong 3D Demos, Uneven Results and Competitive PricingMatthew Berman · Forward FutureMatthew Berman tests the open-weight model on coding, 3D rendering and visual explanations, then compares benchmark results and prices.
 32:20ENMatthew Berman· 2026년 10월 23일Who Is Local AI For? The Costs, Trade-offs and a Hybrid FutureMatthew Berman · Forward FutureMatthew Berman weighs data control and independence against hardware cost, setup complexity and inference speed.
 1:03:37ENMatthew Berman· 2026년 10월 23일Matthew Berman’s Team Tests Kimi K3.1 on Animation, Games, and ChartsMatthew Berman, Alex, Brian · Forward FutureA live team AMA turns into an informal test of Kimi K3.1, from personal-agent workflows to motion graphics, a browser game, and a benchmark chart.