En 30 secondes
OpenAI’s internal security sprint produced enough findings that deduplication and ownership became major bottlenecks. Engineers Ian and Kyle say 36% of findings were duplicates, so they built a workflow that supplies scanners with context, validates and groups reports, assigns owners, generates patches and checks fixes. They describe how the open-source CLI and hosted Codex Security Cloud expose parts of that workflow for other teams.
- 1A security sprint became a continuous find-and-fix loopIan describes scanning, validation, ownership and fix verification, with reported false-positive and rollback rates.
- 2Scanners need architecture and protection contextKyle says narrow scan instructions and shared knowledge help agents interpret code.
- 3Duplicate findings created a substantial triage burdenKyle says 36% of findings in the internal sprint were duplicates.
- 4An independent step checks whether a generated patch worksThe verify-fix workflow challenges the patch before it goes through normal review.
- 5Teams can assemble the workflow or use the hosted serviceThe CLI and SDK support custom integration; the cloud product runs a continuous loop connected to GitHub.
À retenir
- Supply scanners with both task-specific scope and shared system context.
- Deduplicate reports before assigning work; OpenAI says 36% of its sprint findings were duplicates.
- Verify generated fixes and keep normal code review in the release process.
- Run recurring scans as code changes to prevent the backlog from rebuilding.
Lire le texte remanié, chapitre par chapitre
The internal security sprint and its results
The speakers describe the defender’s window and a company-wide push. They report results from validating findings and generated patches.
Ian and Kyle of OpenAI’s cyber product engineering team introduce Codex Security: a CLI workflow for discovering and validating findings, generating patches and verifying fixes, alongside a hosted cloud service.
Ian argues that stronger models give defenders a window to find weaknesses before comparable capabilities become broadly available to attackers. He says OpenAI made security a company-wide priority.
During an internal security sprint, he says, a quarter of product engineers focused on strengthening systems. The team built a continuous loop to scan, validate, assign ownership and verify fixes.
Ian reports a 0.81% false-positive rate after deduplication and validation, and a rollback rate below 1% for Codex-generated fixes. The tools developed from this work are offered as a plugin, CLI, SDK and cloud product.
Give scans enough context
The CLI combines scoped instructions with reusable information about architecture and protections.
Kyle frames the workflow in five parts: provide context, scan, enrich findings, produce patches and integrate the result into the development lifecycle. He says the open-source CLI supplied core building blocks for the internal effort.
A vague instruction to find every vulnerability was insufficient for OpenAI’s large codebase. The team split scans into narrow areas and supplied context about each component, its exposure and existing protections.
A scan-specific instruction defines scope and the vulnerability types to investigate. Repeated background can instead live in a shared knowledge base available to both scanners and validators, including architecture and firewall information outside the source code.
OpenAI also committed SECURITY.md files across components so product owners could record threat models and security guidelines. Kyle demonstrates passing both a prompt and knowledge base into a deep scan.
The deep scan runs multiple agents in parallel, combines findings and repeats passes until it finds nothing new or reaches its configured limit. A large repository can take considerable time.
Group and prioritize findings
Duplicate reports and unclear ownership made triage difficult. The team added deduplication, a security rubric and ownership rules.
Hundreds of agents scanning different areas produced tens of thousands of findings. Kyle says deduplication was an early bottleneck: multiple reports could describe one underlying vulnerability, leading to redundant tickets.
In the internal sprint, 36% of findings were duplicates. The CLI’s deduplication workflow uses agents to group those reports before developers are asked to investigate.
The team next classified findings against a security rubric. Kyle says the rubric was revised as the team learned which vulnerabilities mattered most, including cases where an external actor could gain unauthorized access.
Assigning ownership was unexpectedly difficult in a fast-growing company. Once the team codified which groups owned which components, it could assign findings with fewer tickets passed between teams.
Generate and verify patches
OpenAI gradually moved toward generating fixes in advance. An independent check and ordinary review remain part of the process.
Initially, developers received tickets, asked Codex to propose fixes, and took the changes through pull requests and production. As confidence and context improved, the team began generating patches in advance.
Kyle describes automation as a dial rather than a switch: teams can increase its role as they gain confidence. The CLI patch workflow can be given instructions for starting a development environment and testing the change.
An additional verify-fix step checks whether a patch actually resolves the finding; Kyle compares it to an adversarial agent challenging the proposed fix. The resulting change still goes through the organization’s normal review process.
The speakers say CLI primitives can fit different workflows, whether they require code review, QA or product review. Teams can connect them to repositories and continuous integration rather than replacing their existing process.
Keep scanning as the code changes
The speakers describe model improvements and continuous scanning. They demonstrate the hosted cloud workflow and GitHub integration.
Ian shows a third-party PatchBench comparison and says a newer model delivered better results at lower cost in the displayed test. He expects improvements in models to improve the same security workflow.
He describes a large initial backlog followed by fewer findings and faster detection after the backlog was addressed. To maintain that state, he says, scans must keep running as the codebase changes.
The CLI and SDK can be assembled into CI or GitHub workflows. Codex Security Cloud offers a hosted continuous loop connected to GitHub repositories and uses security-focused Daybreak models, Ian says.
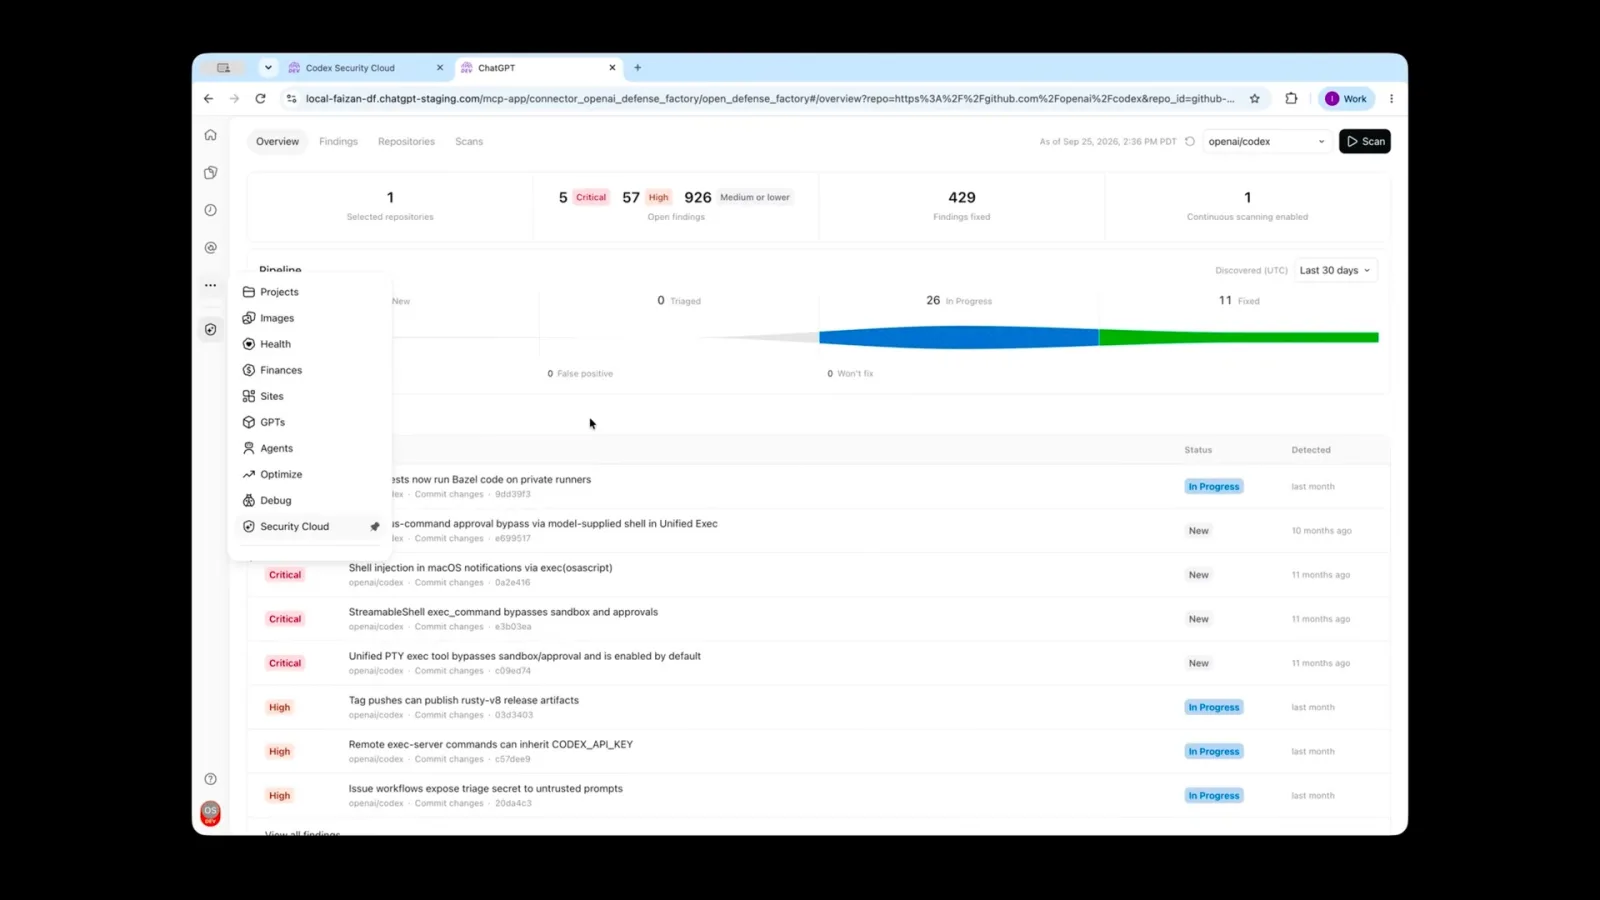
In the cloud demo, he installs the plugin, connects GitHub and configures scanning on each new commit. The results show findings and allow a patch to be generated as a pull request for review.
Sur la même chaîne
 27:44EN
 OpenAI· 11 nov. 2026Plugin extensions bring interactive tools into ChatGPTCorey, Max Neuber · OpenAIOpenAI describes discovery, sidebar and file entry points, event-driven automation and revised submissions.
 24:01ENOpenAI· 11 nov. 2026When agent work needs loops, subagents and a shared logRaj, Eric · OpenAIOpenAI’s Raj and Eric explain persistence, when to delegate and how they coordinate longer work.
 22:37ENOpenAI· 11 nov. 2026How GPT Live keeps speaking while an agent worksAlex, Erika · OpenAIOpenAI demonstrates simultaneous voice, background delegation and three ways to return updates.
 19:44ENOpenAI· 11 nov. 2026What a managed agent harness has to do to keep workingCharlie, Steve · OpenAIOpenAI engineers explain remote sandboxes, long-running state and a human-approved flight rebooking demo.
 27:09ENOpenAI· 11 nov. 2026A six-week coding agent run and what it took to superviseOpenAI engineers describe a CI maintenance agent, long-running context and the cost of keeping it working.
 20:48ENOpenAI· 11 nov. 2026Sites adds personalized connectors and agent-friendly web appsKatia, John · OpenAIOpenAI demonstrates scheduled updates, per-user plugins and WebMCP in two Sites applications.