30초 요약
Nori Agentic co-founders Amol Kapoor and Clifford Ressel explain the role of an asset manager’s security master and why private investments, whose terms live across documents, are hard to standardize. Kapoor describes a customer workflow in which an agent investigates each changed field, cites evidence and asks a human owner to review its recommendation. The speakers present the claimed reduction from roughly an hour to five minutes of human work as an example of their deployment, and argue for shared agent infrastructure, domain-specific instructions and human oversight.
- 1The security masterRessel describes the central investment database as a quality boundary between data producers and downstream consumers.
- 2Private assets lack common identifiersDeal terms and amendments live in bespoke documents rather than a single standardized API.
- 3Reviewing individual cellsKapoor says the customer’s team previously spent about an hour investigating each changed field, on average.
- 4Agent gathers a cited caseA locally deployed model investigates selected sources, produces a recommendation and alerts the owner for review.
- 5Keep a person involvedKapoor argues that substantial automation plus a short human review can be more practical than insisting on full autonomy.
핵심 정리
- A security master connects inconsistent data sources to risk, accounting and compliance workflows.
- Private assets often lack shared identifiers and require information to be extracted from deal-specific documents.
- An agent can gather evidence for a changed field and recommend an action while leaving the decision to a person.
- Instructions, source access and the runtime environment supply much of the agent’s domain context.
- Shared infrastructure and a human review step can make specialized workflows easier to deploy.
챕터별로 다듬은 전문 읽기
Why private-asset data is difficult
Kapoor describes the growth of private investing and the documents that contain its details. He introduces Nori Agentic and the security-master problem.
Amol Kapoor opens with a change in finance: more capital is flowing into private assets, including land, energy infrastructure, data centers and shares in private AI companies. He cites secondary-market volume and forecasts for alternative assets as illustrations of a broader shift, not as guarantees about future growth.
Kapoor attributes that shift to several forces. Alongside demand for infrastructure that supports AI, he points to companies staying private longer, regulatory considerations and investors seeking opportunities outside heavily contested public markets.
If more of the economy is held privately, Kapoor argues, buying an index of public stocks no longer gives an investor exposure to the whole market. That encourages more investors to seek private assets, which in turn makes the practical problem of managing their data more important.
The details of a private investment may be scattered across PDFs, Box folders, emails and call transcripts. Even basic questions such as the number of shares owned, a strike price, the purchase price of land or the rights attached to a deal can require searching several documents.
Kapoor introduces Nori Agentic, which builds cloud agents, and explains that the talk focuses on using them to manage and audit a firm's investments. His co-founder and CTO Clifford Ressel, who has experience in back-office finance, takes over to explain the security master.
What a security master does
Ressel explains how the database connects identifiers and data sources to business-critical analysis. He uses public shares to illustrate mapping complexity.
Ressel describes a security master, or sec master, as the master database of the securities and instruments in an asset manager's investment universe. It serves as a starting point for risk management, profit-and-loss accounting, regulatory compliance and other business-critical analysis.
When sources disagree about a value, the ideal process catches the conflict before it enters the master data. Teams can return to the sources or examine the mapping logic and correct upstream problems before those errors spread to downstream analysis.
Ressel calls this an organizational primitive: a layer between data producers and consumers where standards, visibility and quality checks can be enforced. The implementation could be a complex lakehouse with many tables or a single denormalized source of truth.
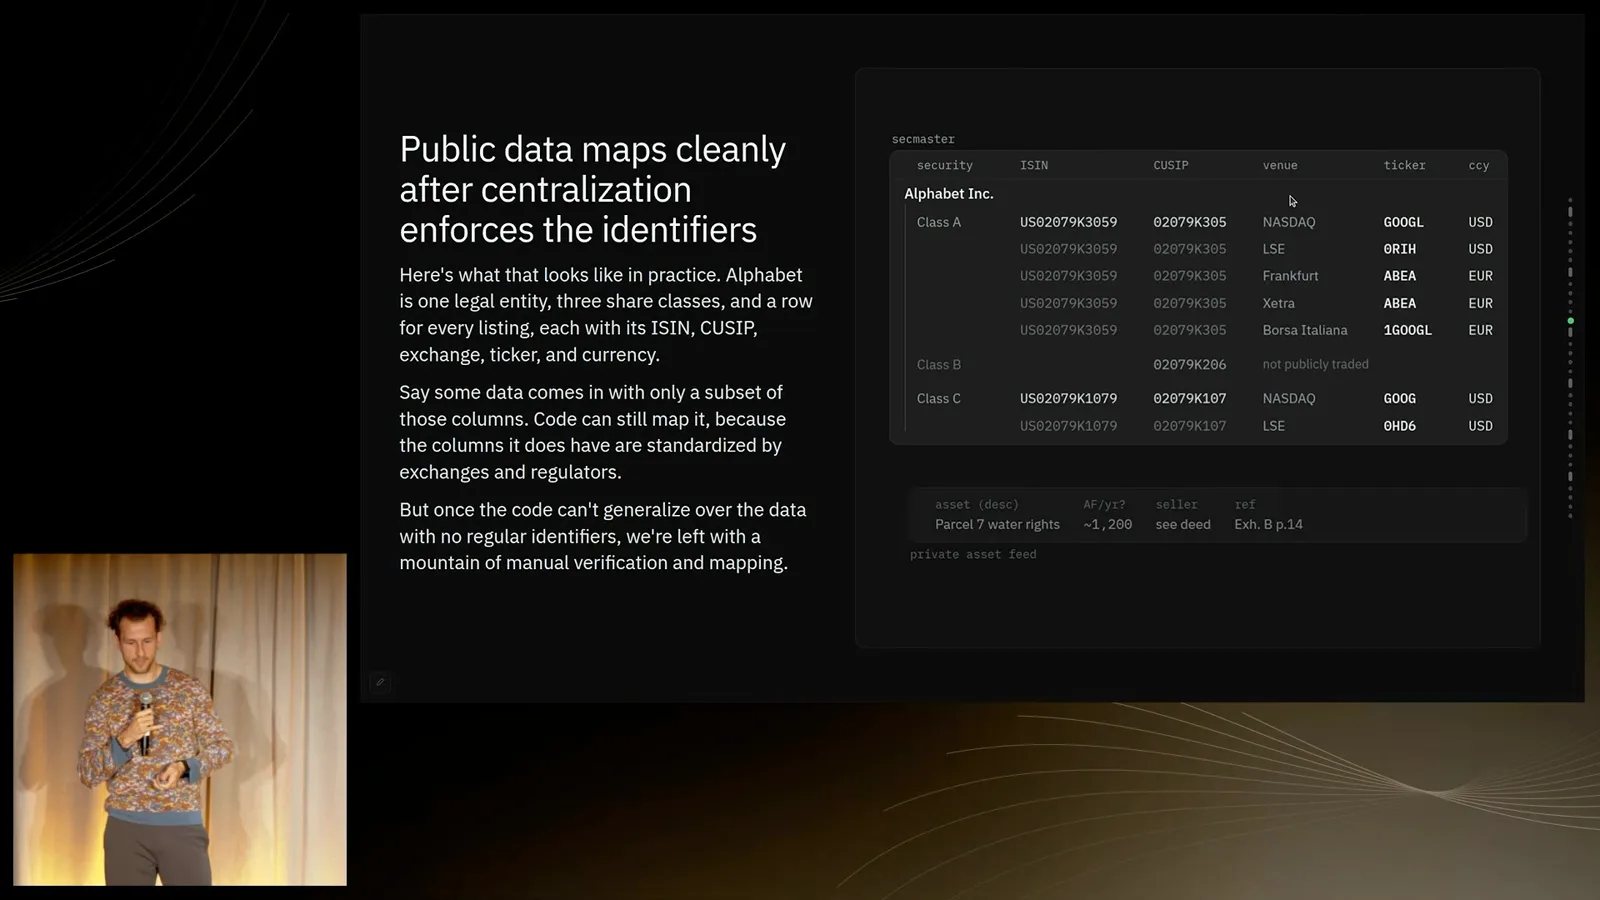
Public markets have several coordinating institutions. Vendors provide identifiers such as FIGIs and RICs, while numbering agencies supply ISINs and CUSIPs for regulatory and other purposes. Mapping these identifiers to an internal view lets firms join outside data, report holdings and model risk.
Even a familiar public stock illustrates the complexity. Google has GOOG and GOOGL share classes; information might be reported at the legal-entity level, the security level or across different exchanges. A firm must map those different granularities correctly before it can combine the data.
Ressel compares the problem to a date-time library: it looks straightforward when someone has solved it well, but the implementation contains many edge cases and complex conventions. A denormalized table can give incoming data enough identifier mappings to reach the right internal record even if only some identifiers are present.
Where private assets break the model
Private deals may have no common identifiers or centralized data source. Their terms and amendments need to be reconciled from individual documents.
Structured data and a well-defined internal ontology can help coding agents build new analyses, Ressel says. The harder case is a source with no standard identifier: someone must determine manually which entity it describes and whether the mapping is correct.
Consider lending to a company building a power plant or buying nearby land. There may be no shared identifier, central regulator of the information structure or vendor API with a ready-made ontology. Repayment schedules, collateral and amendments live in individual agreements, so each asset brings its own documents and data work.
Kapoor returns to the operational consequence. Private assets still need standardization, cleaning and auditability even when their documentation is inconsistent. Risk analysts should not have to search every document themselves to establish whether the data they receive is correct.
A change-review workflow
Kapoor describes an asset manager’s cell-by-cell review process. The team’s agent investigates changes, cites evidence and asks the owner for a decision.
He describes a Fortune 200 asset manager whose data engineering team checked day-over-day changes to a security master. In his example, a table of 50,000 assets and around 200 columns produces a continuing stream of individual cell changes for people to investigate.
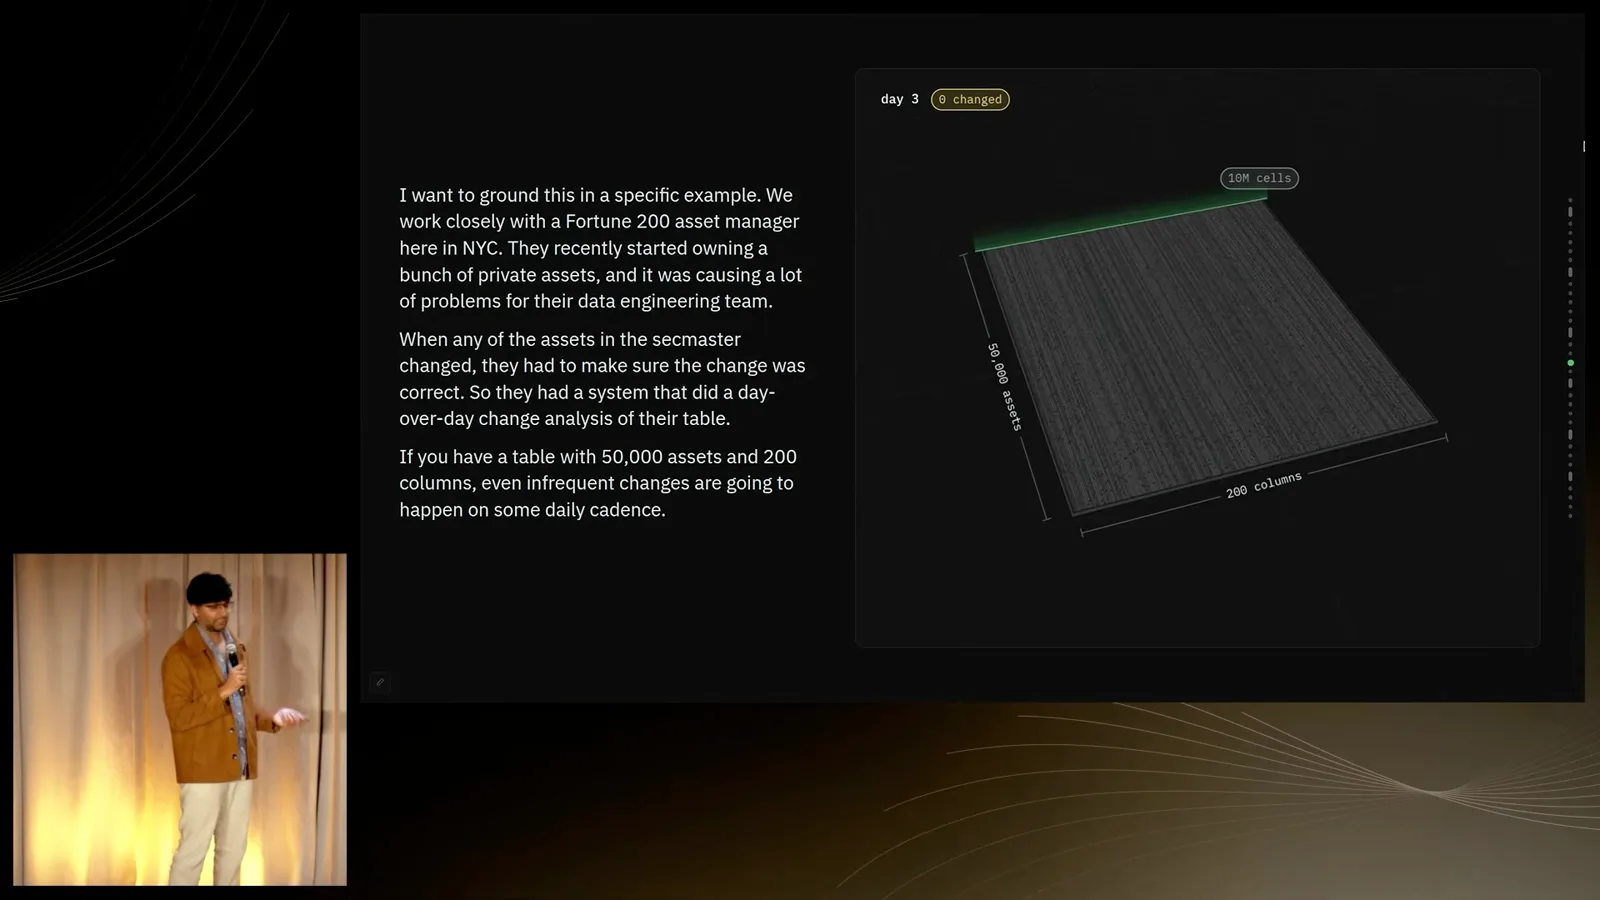
Investigators compared each changed cell with documents and other sources to decide whether it was valid. A price, name, bankruptcy, ownership change or renegotiated contract could each trigger a review. Kapoor says the work averaged about an hour per change; he corrects an initial statement of hundreds of thousands of monthly hours to hundreds or thousands.
Kapoor defines a cloud agent as a coding agent operating in a remote environment rather than on a user's laptop. He says that environment can support scheduled work, observability, transparency and audit requirements, so the agent can start when new security-master data arrives.
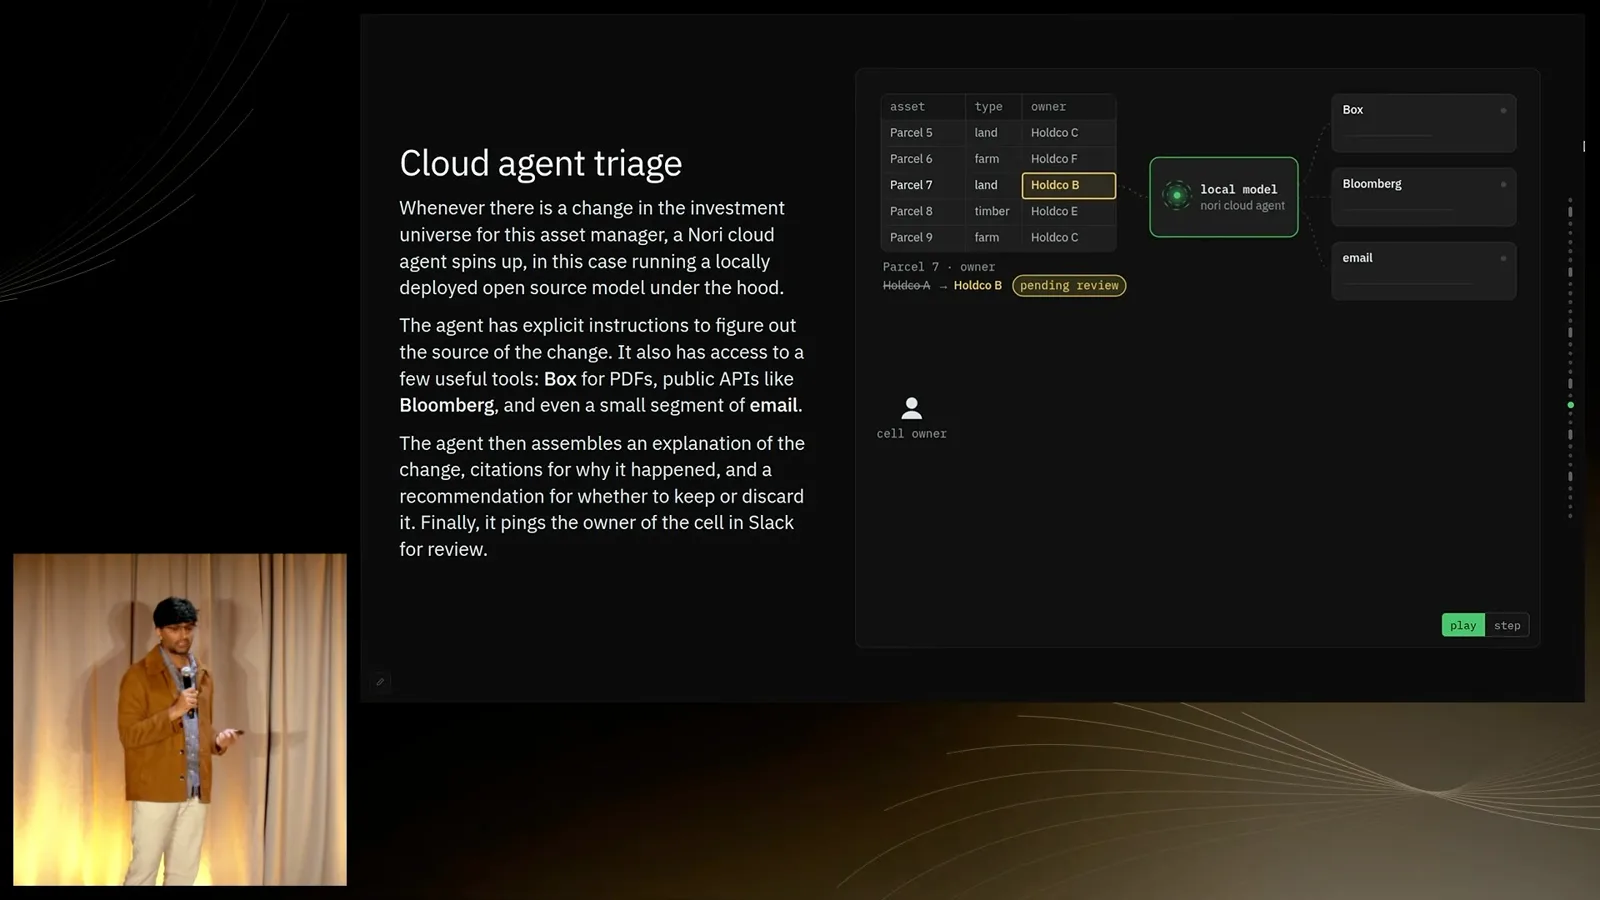
In the described deployment, a change triggers a Nori agent using a locally deployed open-source model within the customer's environment. The agent has instructions and access to selected sources, including PDFs in Box, public data APIs and a limited portion of email, to investigate the origin of the change.
The agent assembles an explanation, cites supporting sources and recommends retaining or discarding the change. It then alerts the owner of the changed cell in Slack. A person reviews the recommendation and can perform further research; the agent is not the final authority.
Kapoor says the agent reduces the human portion of a typical check from around an hour to about five minutes because it performs the document search and assembles the supporting case. This is the team's account of its particular workflow, not a general benchmark for all asset managers.
Instructions and shared infrastructure
The speakers use written domain guidance and configured tools to adapt a general agent. Kapoor proposes reusing orchestration and security across different workflows.
How does the agent gain domain expertise? Kapoor compares it with onboarding an analyst: provide written guidance on where documents live, which sources to trust and how to assess changes. Teams can update natural-language Markdown instructions rather than building a separate bespoke agent for every task.
He suggests pairing a general agent with configurations such as skills or AGENTS.md files. Much of the specialization comes from the environment, credentials, available tools and instructions supplied to it, rather than a unique underlying orchestration system for each workflow.
Kapoor likens the resulting security master to a database surrounded by small automated cleaners that watch for issues and surface them. He argues that the same pattern can move enterprise work from a reactive model, where a person asks an agent for help, to one where agents proactively bring people analysis and recommendations.
For that approach to scale, he recommends common infrastructure for orchestration, security and integrations across security-master, audit and code-review agents. Each task can retain its own triggers, tools, context and company-owned instructions while sharing the underlying platform.
Lessons from building for finance
Kapoor emphasizes collaboration with domain experts and human review. He argues agents can reduce the effort caused by inconsistent, organically evolved systems.
His first lesson is that AI adoption is a collaboration problem: customers want solutions while engineers often offer building blocks. Nori found progress when domain experts could connect the capabilities of cloud agents to a concrete problem they already had.
Second, Kapoor recommends aiming for substantial automation while keeping a human involved. Rather than insisting that an agent complete every case end to end, a five-minute human review can make many valuable workflows practical and preserve accountability, especially in finance.
His final lesson concerns accidental complexity: work caused by the way systems evolved, such as the same data appearing in different formats, rather than by the intrinsic difficulty of the underlying problem. He sees agents as useful for this repetitive, high-effort work, freeing people to spend more time on genuinely difficult decisions.
같은 채널의 다른 글
 31:22EN
 AI Engineer· 2026년 11월 7일Nouha Dziri on Making Coding-Agent Teams More Cost-EfficientNouha Dziri · CohereExperiments on ProgramBench and Commit0 show why the task bottleneck, lead model and coordination design matter more than simply adding agents.
 18:28ENAI Engineer· 2026년 11월 7일Vinoo Ganesh on Building AI Answers from Verifiable FactsVinoo Ganesh · KeplerKepler’s co-founder describes pointer-based retrieval, deterministic calculations and access controls for financial AI.
 1:04:02ENAI Engineer· 2026년 11월 6일Lance Martin: Audit Prompts, Build Better Evals and Optimize Agent CostLance Martin · AnthropicAn Anthropic engineer explains prompt caching, evaluation design, hill climbing and the architecture of reliable long-running agents.
 23:05ZHAI Engineer· 2026년 11월 6일Ryo Lu:当我们什么都能做,还知道自己想做什么吗?Ryo Lu从 AI 生成的日记工具到爵士乐团,Ryo Lu 讨论如何在更强大的工具旁保有判断、生活和与他人合作的空间。
 19:19ENAI Engineer· 2026년 11월 6일Ben Holmes: Use Agent Traces to Improve Agent SkillsBen Holmes · WarpThe Warp engineer explains how scoring conversations can uncover hidden friction and produce reviewable configuration improvements.
 19:43ENAI Engineer· 2026년 11월 6일How a Knowledge Graph Helped Map a 35-Million-Line MainframeStephen Chin, Neeraj Deshmukh · Neo4jStephen Chin and Neeraj Deshmukh explain context, agent orchestration and behavior-parity tests for legacy-system modernization.