30초 요약
Theo Browne reads proposed Codeberg terms concerning projects consisting mostly of generative-AI-written code. He disputes the implied security comparison and cites a viewer poll and his own experience; neither establishes the security of AI-generated code in general.
- 1The proposed restrictionTheo reads wording concerning projects mostly composed of code written by generative AI.
- 2A viewer pollHe asks whether a randomly selected AI-generated package or one by a below-average developer is more likely to be secure.
- 3Theo’s experienceHe believes recent AI models often write better code than average people, based on his own reading of code.
핵심 정리
- The proposal concerns projects mostly consisting of AI-written code, not every use of AI.
- Codeberg cites copyright uncertainty and concerns about safeguards against harmful code.
- Theo’s viewer poll reflects a self-selected audience and does not measure actual security.
- His comparison of human and AI-written code is a personal assessment, not a controlled study.
챕터별로 다듬은 전문 읽기
Codeberg’s proposal and a security comparison
Theo reads proposed language and polls his audience. He shares his view of recent AI-generated code while the poll remains an informal measure of audience opinion.
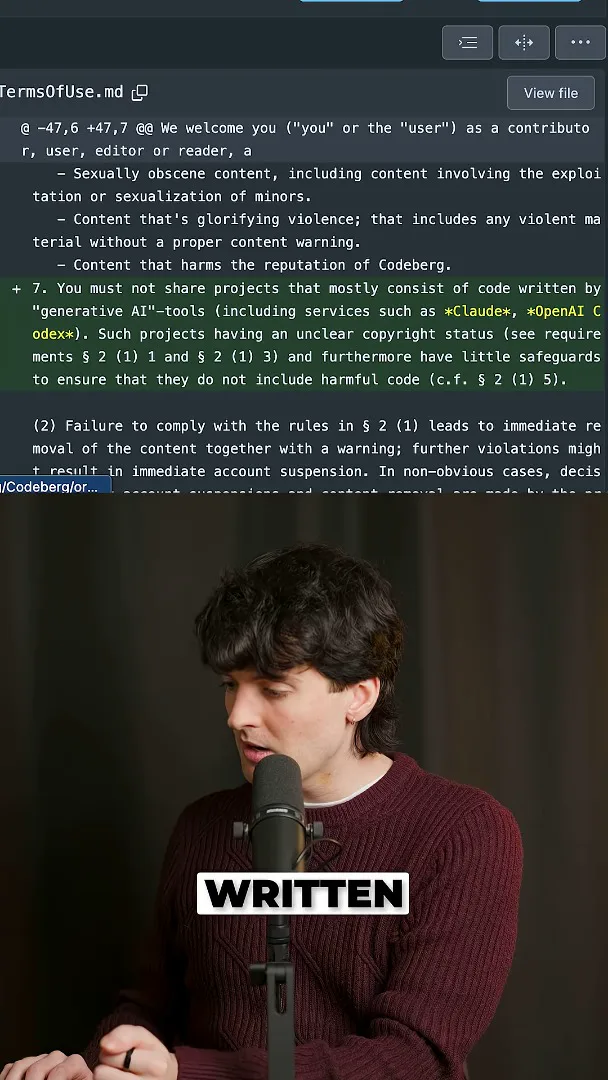
Codeberg’s proposed terms say users must not share projects consisting mostly of code written by generative AI tools. The language raises concerns about unclear copyright status and safeguards against harmful code. This concerns projects mostly made of AI-written code, not every use of AI; the organization’s [announcement](https://blog.codeberg.org/protecting-our-floss-commons-from-llms.html) also describes preliminary enforcement guidance.
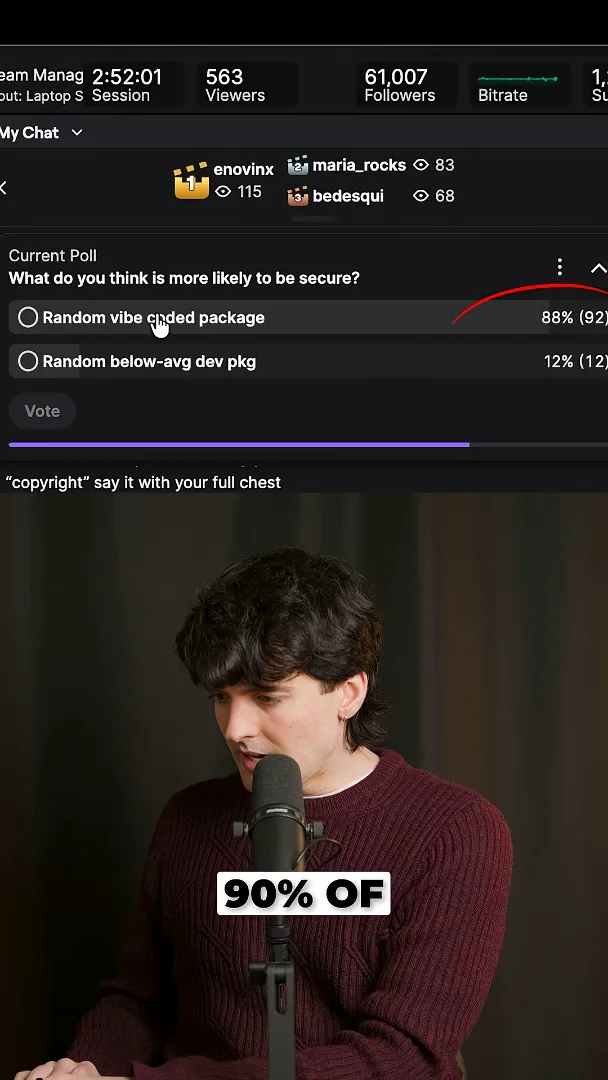
I ask my audience which they think is more likely to be secure: a randomly selected vibe-coded package using modern models such as Fable and GPT-5.6, or a random package by a below-average developer. I report that about 90% of my chat chooses the AI-generated package. This is a self-selected audience poll, not a security test or a representative survey.
Some viewers say they would have voted differently a year earlier, and I would have too. Since Opus 4.5, I have read a lot of code from both AI and people; my impression is that the average person writes worse code than the average output using Opus 4.5 or newer. That is my personal experience, not evidence that a particular generated package is secure.
같은 채널의 다른 글
 38:47EN
 Theo - t3․gg· 2026년 10월 28일Theo’s Long-Running Agent Experiments: Verification, Compute and CostTheo Browne · Ping LabsA skateboard game and two compiler projects show how repeated checks and flexible compute can sustain agent work—and how expensive those loops can become.
 36:07ENTheo - t3․gg· 2026년 10월 27일Theo on Token Costs, Coding Agents, and the Price of AI CapabilityTheo Browne · Ping LabsA viral estimate of Lauren's AI spending prompts a closer look at cache pricing, benchmarks, and the changing work of coding agents.
 30:37ENTheo - t3․gg· 2026년 10월 26일Theo’s Three Skills for Reviewing and Shipping with Coding AgentsTheo Browne · Ping LabsHow sol-loop, full-send and full-stop encode review, verification and different levels of merge authority.
 0:43ENTheo - t3․gg· 2026년 10월 23일Theo Distinguishes Security Vulnerabilities from Active AttacksTheo Browne · Ping LabsA short explanation of why disclosed software flaws and reported attacks are different kinds of security news.
 29:22ENTheo - t3․gg· 2026년 10월 22일Theo on Security Vulnerabilities, Stolen API Keys and AITheo Browne · Ping LabsA look at the gap between vulnerability disclosure and patching, and a speculative account of why stolen inference keys may be valuable.
 31:13ENTheo - t3․gg· 2026년 10월 20일Theo on Why Smarter Models Help More Than DevelopersTheo Browne · Ping LabsFrom game modifications to compiler experiments, Theo revisits his assumptions about who benefits from more capable AI.