30 秒でわかる
Patrick Smyth of Chainguard argues that AI-enabled attackers and supply-chain malware are changing the risk calculus for open-source dependencies. He discusses the shrinking time between exploitation and patches, malicious packages, known vulnerabilities, zero-days and attacks on CI/CD, developer machines and agent tooling. Smyth recommends faster remediation, package cooling periods, signed artifacts and provenance. He also explains Chainguard’s containers, source-built libraries, consortium and hardened workflow offerings as the company’s proposed responses.
- 1Exploitation and patch timingSmyth cites Mandiant data on the gap between exploitation and vendor patches; the displayed slide shows an average of minus seven days for 2025.
- 2Malware can propagate through dependenciesHe discusses Shai-Hulud and incidents involving Trivy, LiteLLM and Axios as examples of supply-chain attacks.
- 3A chain of trustOrganizations depend on upstream software while bearing responsibility to their own users, making dependency security a shared concern.
- 4Distinct risk surfacesHe separates malware, known CVEs and zero-days from entry points such as CI/CD and agent tooling.
- 5Remediation targetsSmyth describes Chainguard’s stated targets of one day for known-exploited vulnerabilities, seven for critical issues and fourteen for the remainder.
- 6Sign artifacts and check provenanceHe recommends signing artifacts and verifying their provenance across internal pipelines using tools such as Sigstore and SLSA.
ポイント
- Software users depend on upstream components that can affect their own customers if compromised.
- Smyth argues that conventional patch windows are increasingly strained by rapid exploitation.
- Package cooling periods, faster remediation and signed artifacts address different parts of the supply-chain problem.
- CI/CD pipelines, developer workstations and agent tooling are additional attack surfaces.
- Minimal images and source-built dependencies are among the approaches Smyth describes; they do not eliminate the need for continuing security work.
チャプターごとに整えた全文を読む
Faster attacks and shorter patch windows
Smyth introduces examples of AI-assisted attacks and cites Mandiant figures on exploitation relative to patches.
Patrick Smyth of Chainguard introduces a talk about how frontier AI changes risk tolerance for open-source software. He begins with examples that he says show attackers using AI to scale their work, and argues that capabilities that once required a team may become accessible to a smaller group.
Smyth describes reported incidents involving AI-assisted scripts, ransomware and attacks across multiple organizations. His broader point is that attackers can use the same accelerating tools as defenders, increasing the importance of software supply-chain security.
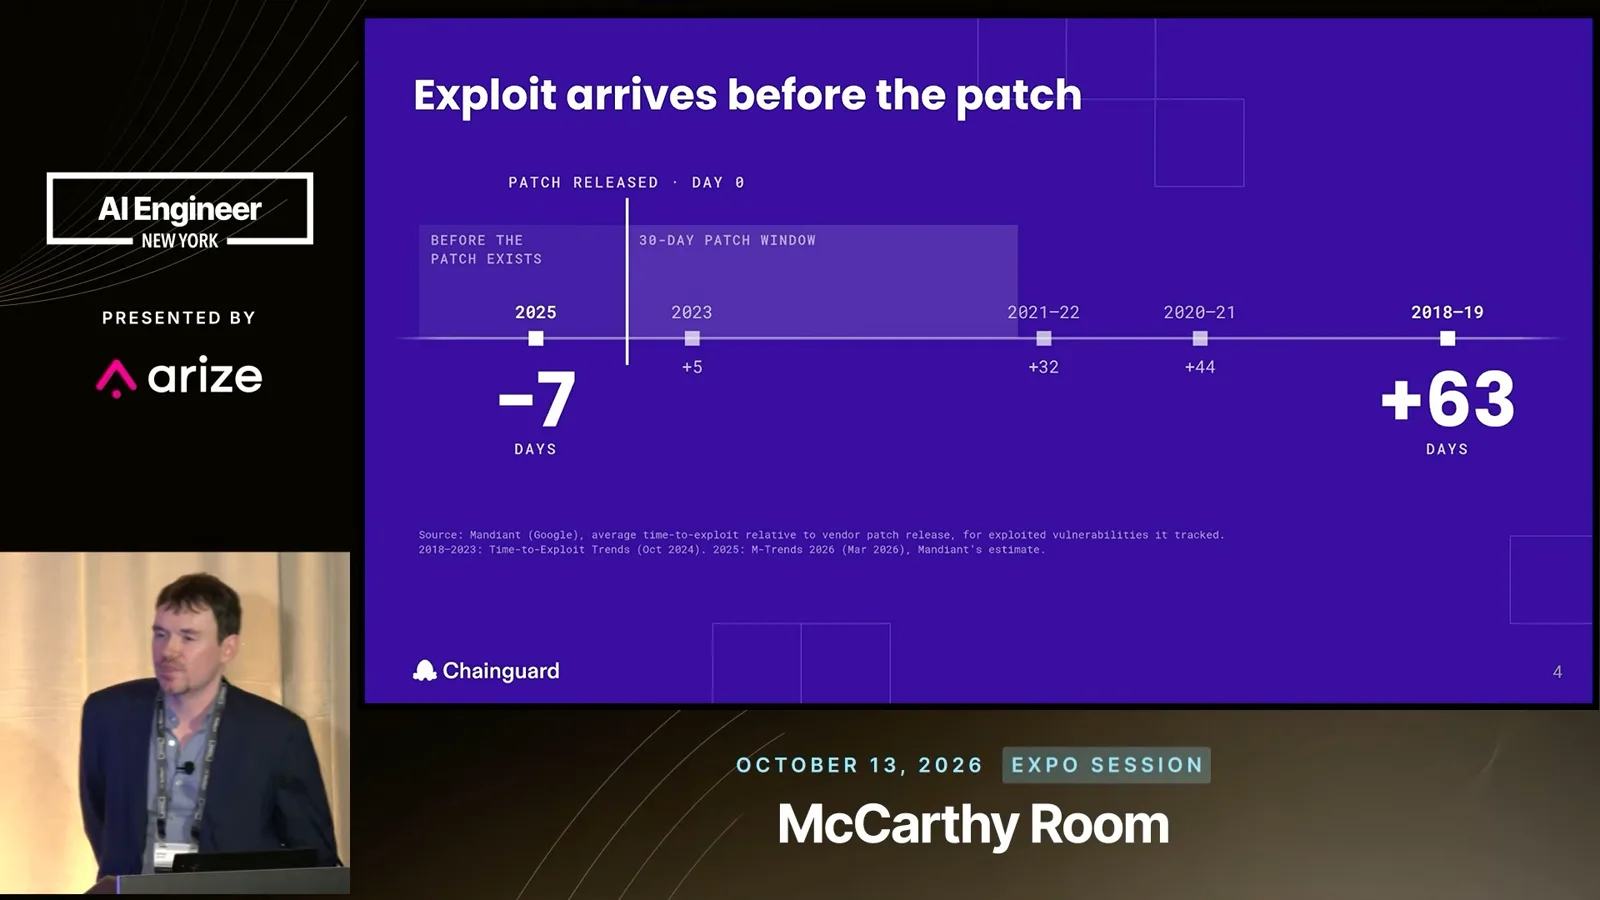
He cites Mandiant’s M-Trends data on the average time of exploitation relative to vendor patch release. His slide shows about 63 days after a patch in 2018–19 and seven days before the patch in 2025 for tracked vulnerabilities. He cautions that averages are noisy but says the trend challenges conventional remediation windows.
A typical workflow scans a software stack with tools such as Grype or Trivy, ranks known CVEs by severity and assigns remediation to a team. Smyth argues that a 30-day schedule can be too slow when attackers exploit known vulnerabilities quickly or discover unknown ones before a patch exists.
Malware and the supply-chain trust problem
He discusses recent malware incidents, dependency propagation and how organizations depend on upstream software while serving their own users.
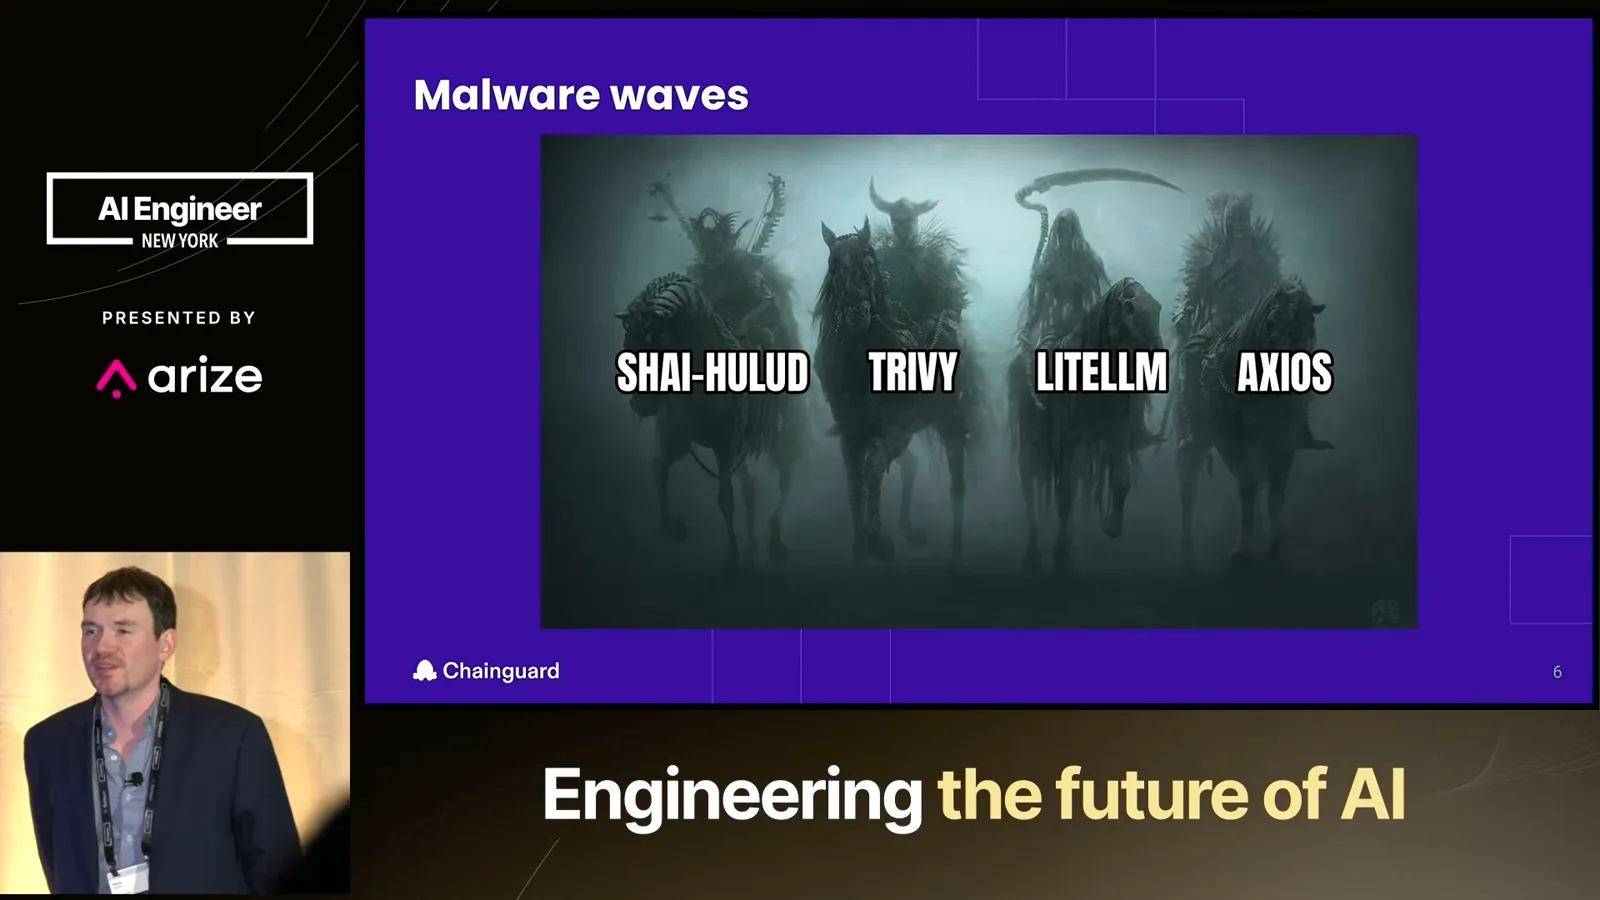
He turns to malware in the software supply chain, citing Shai-Hulud, Trivy, LiteLLM and Axios as examples. He describes Shai-Hulud as a worm in the JavaScript ecosystem and says compromised dependencies can propagate attacks through connected projects.
Smyth says one Axios supply-chain incident was live for only a short period while the package received many downloads. His point is that the impact of a compromised package is amplified when other projects depend on it.
He argues that frontier agents accelerate both software production and attackers’ work. To explain changing trust, he invokes “eternal September”: a community can move from a high-trust environment to a more adversarial, lower-trust one as participation changes.
For Smyth, the fundamental supply-chain problem is a chain of responsibility. Users rely on an organization’s software, while that organization pulls components from upstream sources it must assess and maintain. A compromise upstream can therefore affect both the organization and its users.
Security practices and attack surfaces
Smyth recommends cooldown periods, remediation and signing, then distinguishes known vulnerabilities, malware, zero-days and soft targets.
His recommendations include package cooling periods, faster CVE remediation, signing artifacts and paying attention to operational security on developer laptops, including physical security keys. He says these practices address different parts of a more hostile environment.
Smyth also encourages teams to complete foundational work such as containerization, CI/CD and standardized images. Without those foundations, he says, other modernization and security efforts become harder; AI may help teams accelerate that work.
He introduces Chainguard as a company focused on the software supply chain and says its founders helped create projects including Kubernetes, Sigstore, SLSA and Google Distroless. He then separates several interacting risk surfaces.
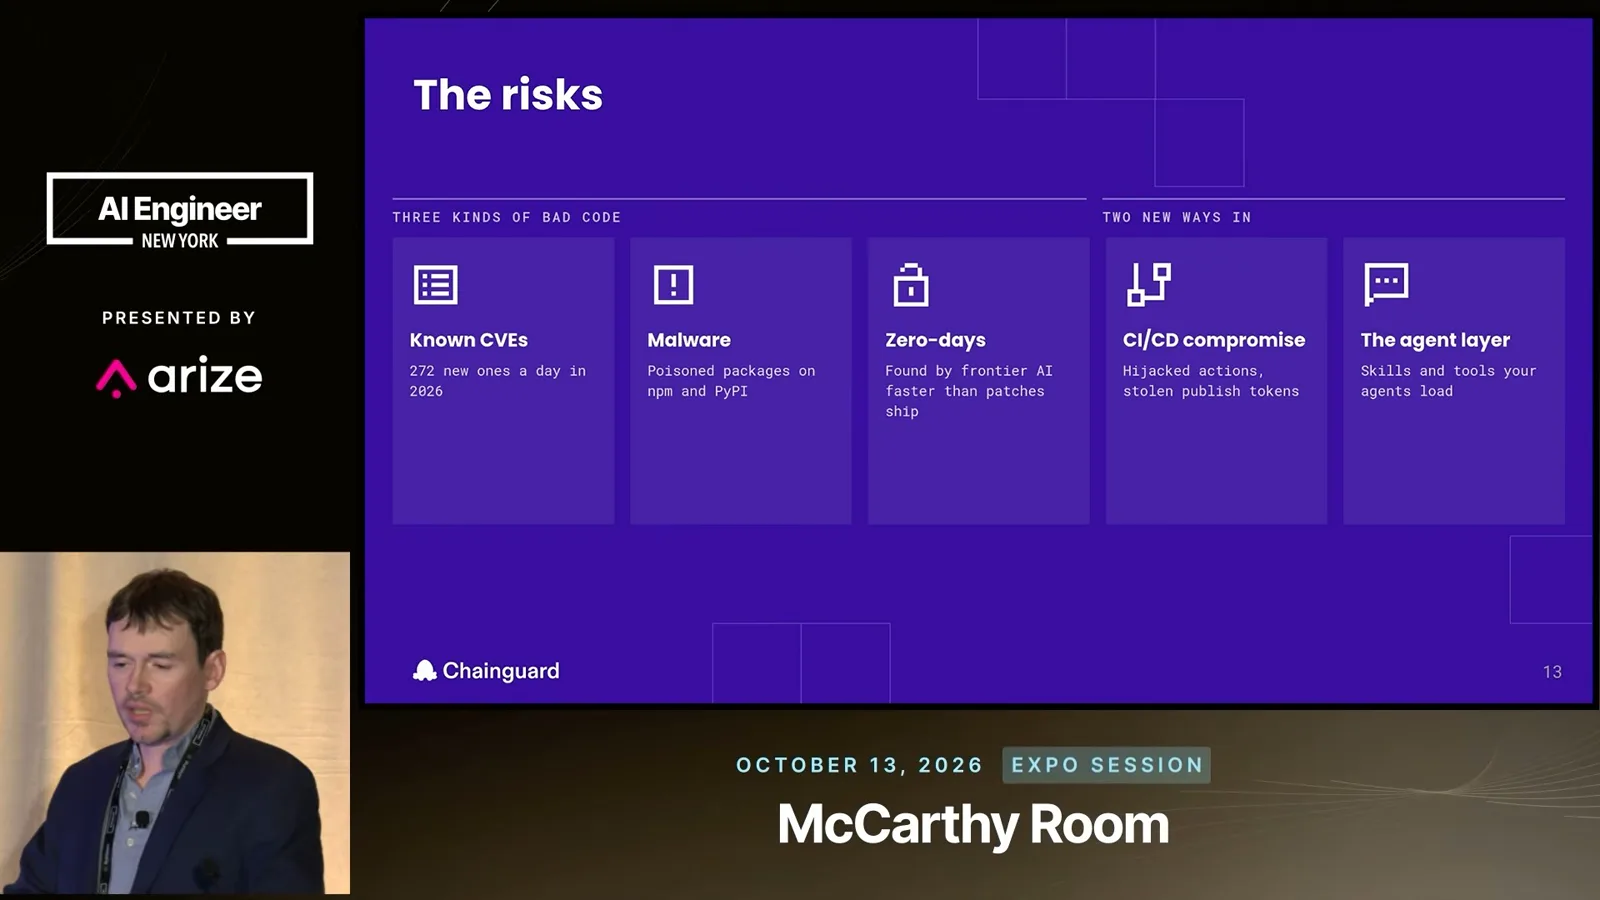
The first is malware in packages; a cooldown period can reduce exposure to some rapidly detected incidents. The second is known vulnerabilities: although many CVE reports create noise, Smyth says the important ones must be identified and fixed because attackers can compare deployed software with public vulnerability databases.
The third category is unknown vulnerabilities or zero-days. Smyth argues that frontier models increase the importance of this area because they can help chain smaller weaknesses together. He also warns about CI/CD pipelines, developer workstations and emerging agent tooling as alternative entry points.
Chainguard’s proposed responses
He describes containers, source-built libraries, the Athena consortium and hardened actions and skills.
Smyth describes Chainguard containers designed to have no known vulnerabilities at release, and libraries built from source as alternatives to consuming packages directly from public registries. These are company offerings he presents as ways to reduce specific supply-chain risks.
For zero-days, he describes Athena as a consortium and clearinghouse that shares information about discovered vulnerabilities with participating organizations. He also introduces hardened CI/CD actions and agent skills as responses to attacks on those layers.
Smyth illustrates the dependency problem with an explicitly made-up estimate that a small fraction of running code is an organization’s own application code. Much of the rest comes from operating systems, runtimes and other components outside the application team’s direct control.
He says Chainguard built Wolfi as a rolling Linux distribution, pulling upstream changes quickly and rebuilding images one to four times a day. He also emphasizes minimal images as a way to reduce exposed components, including potential zero-day attack surface.
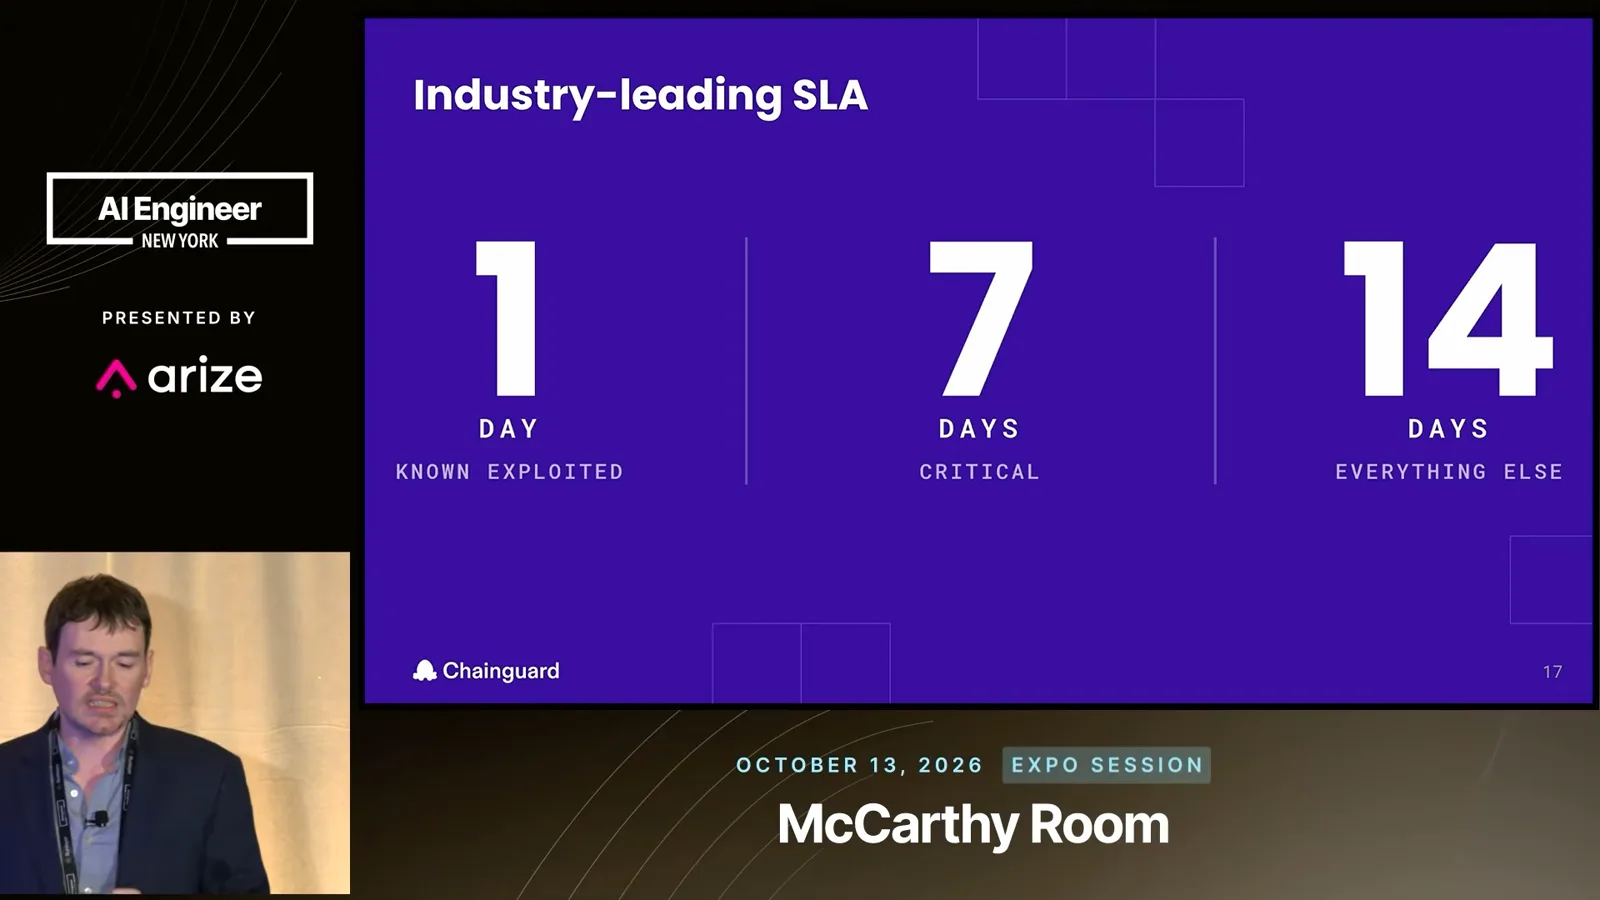
The service-level targets on his slide are one day for a known-exploited vulnerability, seven days for critical vulnerabilities and fourteen days for the remainder. He contrasts this with teams that may never triage lower-severity issues quickly.
Signing, provenance and hardened workflows
Smyth discusses SLSA and Sigstore, rebuilding packages from source, and protecting CI/CD and agent skills.
Smyth recommends signing artifacts when they are created and verifying signatures downstream. He describes Sigstore as useful for signing and SLSA as a way to attach and verify provenance through internal pipelines, where tags, dependencies or distribution steps can be attacked.
He explains Chainguard’s library approach as taking upstream source, building it in the company’s own pipeline and distributing the resulting artifacts, with scanning and remediation around that process. He presents this as a way to reduce exposure to attacks between source and package distribution.
Smyth says Chainguard Actions aim to harden CI/CD workflows, while its agent skills offering processes third-party skills through deterministic and agentic checks. He reports his own estimates of malicious or insecure skills in upstream repositories, framing them as findings from his analysis.
He closes by inviting discussion and pointing listeners to a finance-focused event and the company’s materials. The talk’s central message is that faster attacks require teams to secure dependencies, build pipelines and newer agent layers as well as application code.
同じチャンネルの記事
 21:32EN
 AI Engineer· 2026年10月29日Shy Ruparel on AI agent reliability and recovery after failuresShy Ruparel · TemporalTemporal’s survey finds a gap between frequent agent use and dependable deployment. Ruparel demonstrates a synthetic payout workflow that resumes after workers stop.
 14:50ENAI Engineer· 2026年10月29日Cole Gannaway on code review, cross-repository risk and AI software factoriesCole Gannaway · QodoA one-line rename can pass local checks while affecting distant clients. Qodo’s Cole Gannaway explains how review context, shared rules and independent agents can expose those risks.
 11:47ENAI Engineer· 2026年10月29日Revolut’s David Abitbol on self-hosting AI coding models at scaleDavid Abitbol · RevolutAbitbol shares engineering delivery trends, GPU-serving costs and latency tuning, then describes controls for operating the tools in a regulated bank.
 14:09ENAI Engineer· 2026年10月28日Taylor Luttrell-Williams on Finding Logic Vulnerabilities with SonarQube Hunter AgentTaylor Luttrell-Williams · SonarSonar’s Taylor Luttrell-Williams explains how a security agent maps a codebase, investigates logic flaws and presents validated findings alongside conventional scans.
 16:29ENAI Engineer· 2026年10月28日Chris Vela on Benchmarking vLLM Configurations with Runpod BenchPodChris Vela · RunpodRunpod’s Chris Vela demonstrates a dashboard for comparing LLM serving configurations and choosing performance settings with workload-specific data.
 18:52ENAI Engineer· 2026年10月28日Manish Kapur and Addy Osmani on Verifying AI Software FactoriesManish Kapur, Addy Osmani · SonarSonar’s Manish Kapur and Anthropic’s Addy Osmani discuss code review, evidence and layered checks as coding agents increase the pace of software changes.