30 秒でわかる
In this June 2026 breaking-news video, Theo discusses Anthropic’s statement that it would suspend Fable 5 and Mythos 5 access after a US export-control directive. He reviews the company’s explanation of a potential narrow jailbreak and its defense strategy, while the details and outcome remained uncertain at recording time.
- 1The directive as described by AnthropicThe company said foreign-national access was restricted and it would suspend access for all customers to comply.
- 2The disputed demonstrationAnthropic said the demonstrated findings were minor and comparable capabilities existed in other models.
- 3Defense in depthThe company described red-teaming, layered safeguards and monitoring, while acknowledging that no safeguards are perfect.
- 4A call for a transparent processAnthropic said it would comply but disputed the decision and called for a transparent, fair, technically grounded process.
- 5An unverified motiveTheo raises retaliation as a possibility without evidence; it remains speculation.
ポイント
- Anthropic said it would suspend the two models for all customers to comply with a directive concerning foreign-national access.
- The company said the government’s letter lacked specific details of the national-security concern.
- Anthropic characterized the described jailbreak as narrow and argued that similar capabilities existed in other models.
- The company said it would comply while calling for a transparent and technically grounded process.
- Theo’s suggestion of a retaliatory motive was speculation unsupported by evidence in the video.
チャプターごとに整えた全文を読む
The sudden suspension
Theo describes the impact and reads Anthropic’s account of the directive. He distinguishes the affected models from other Anthropic products.
Fable suddenly became unavailable after only a few days. I had been using it heavily and had paid for subscriptions for my team, so the disruption affects us directly. I am frustrated by how quickly this happened and concerned about the precedent.
Anthropic said the US government issued an export-control directive concerning access to Fable 5 and Mythos 5 by foreign nationals, whether inside or outside the United States, including Anthropic employees. The company said it would disable both models for all customers to comply and that its other models were unaffected.
The security explanation
Anthropic describes a narrow potential bypass and its safeguards. Theo weighs the company’s claims and the limits of the available information.
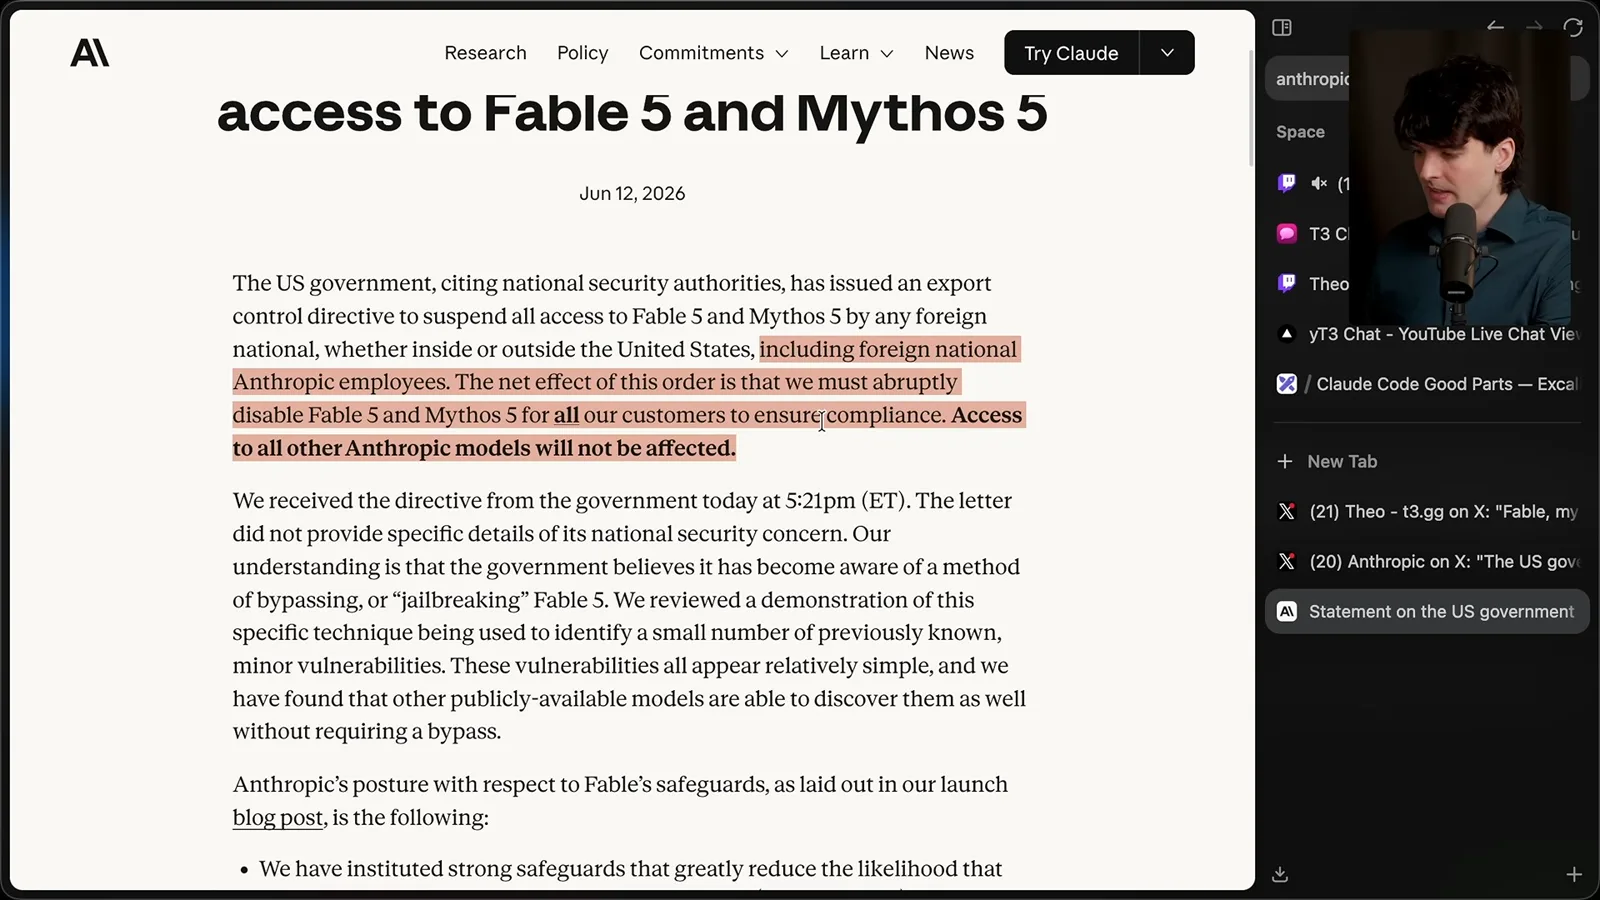
Anthropic said it received the directive at 5:21 p.m. Eastern time on June 12 and that the letter did not give specific details of the national-security concern. Its understanding was that the government had learned of a potential method of bypassing Fable’s safeguards.
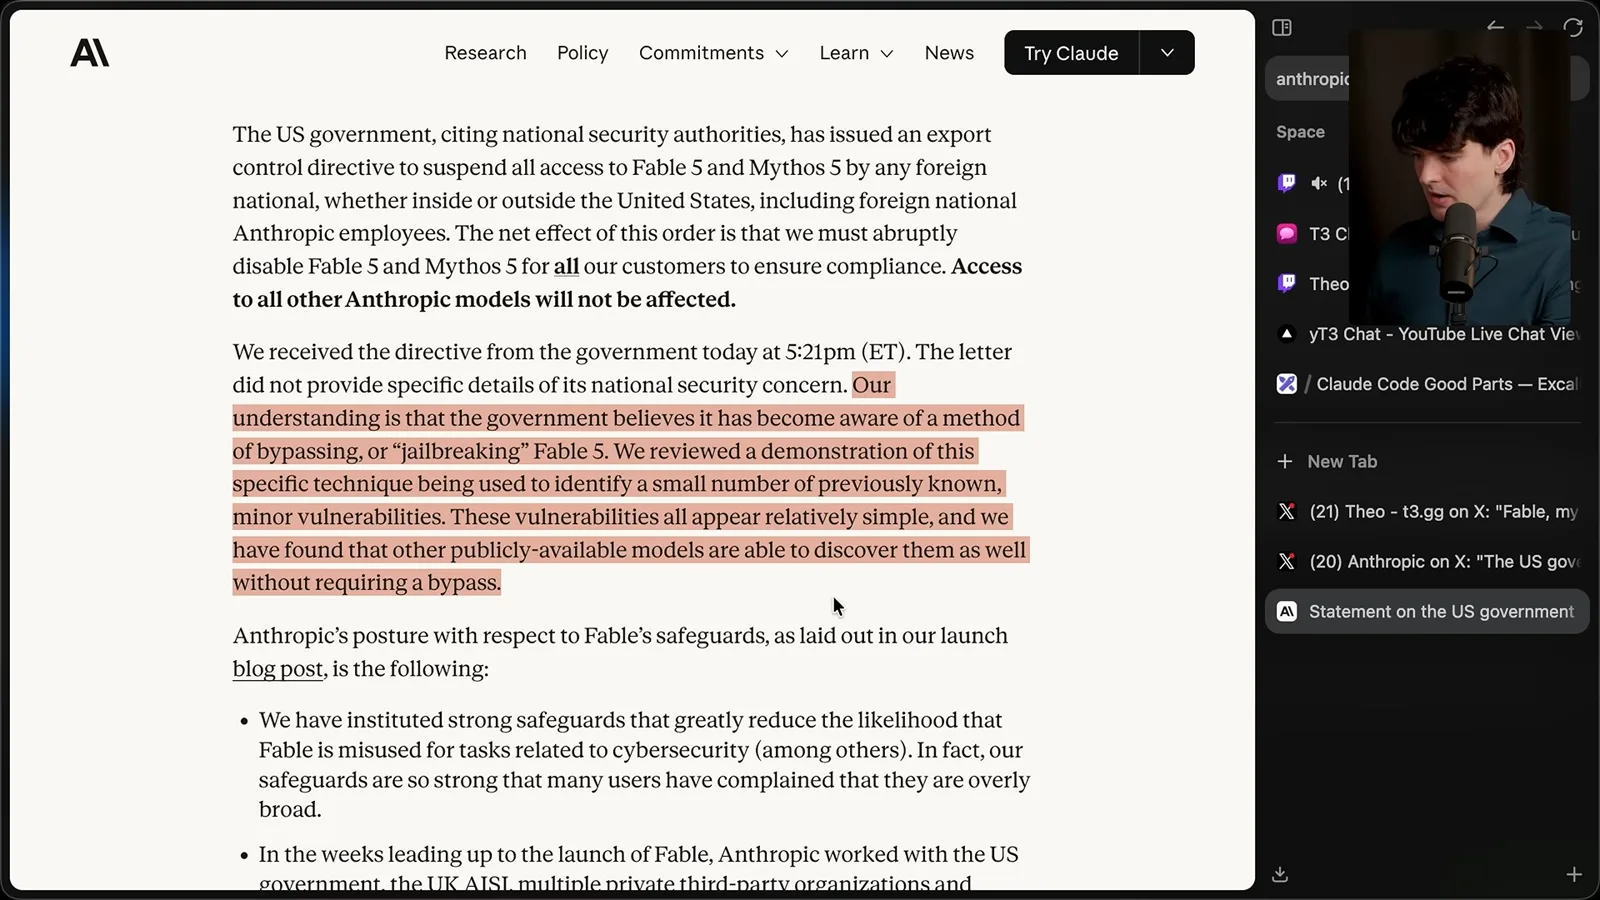
The company said it reviewed a demonstration involving a small number of previously known minor software vulnerabilities. It said the issues appeared relatively simple and that other publicly available models could find them without the same bypass. Those are Anthropic’s assessments of the demonstration, not an independent determination of the government’s full evidence.
Anthropic described extensive red-teaming before release with government, outside organizations and internal teams. It said testers had not found a universal jailbreak, while acknowledging that narrow bypasses remained possible and that perfect resistance was unlikely.
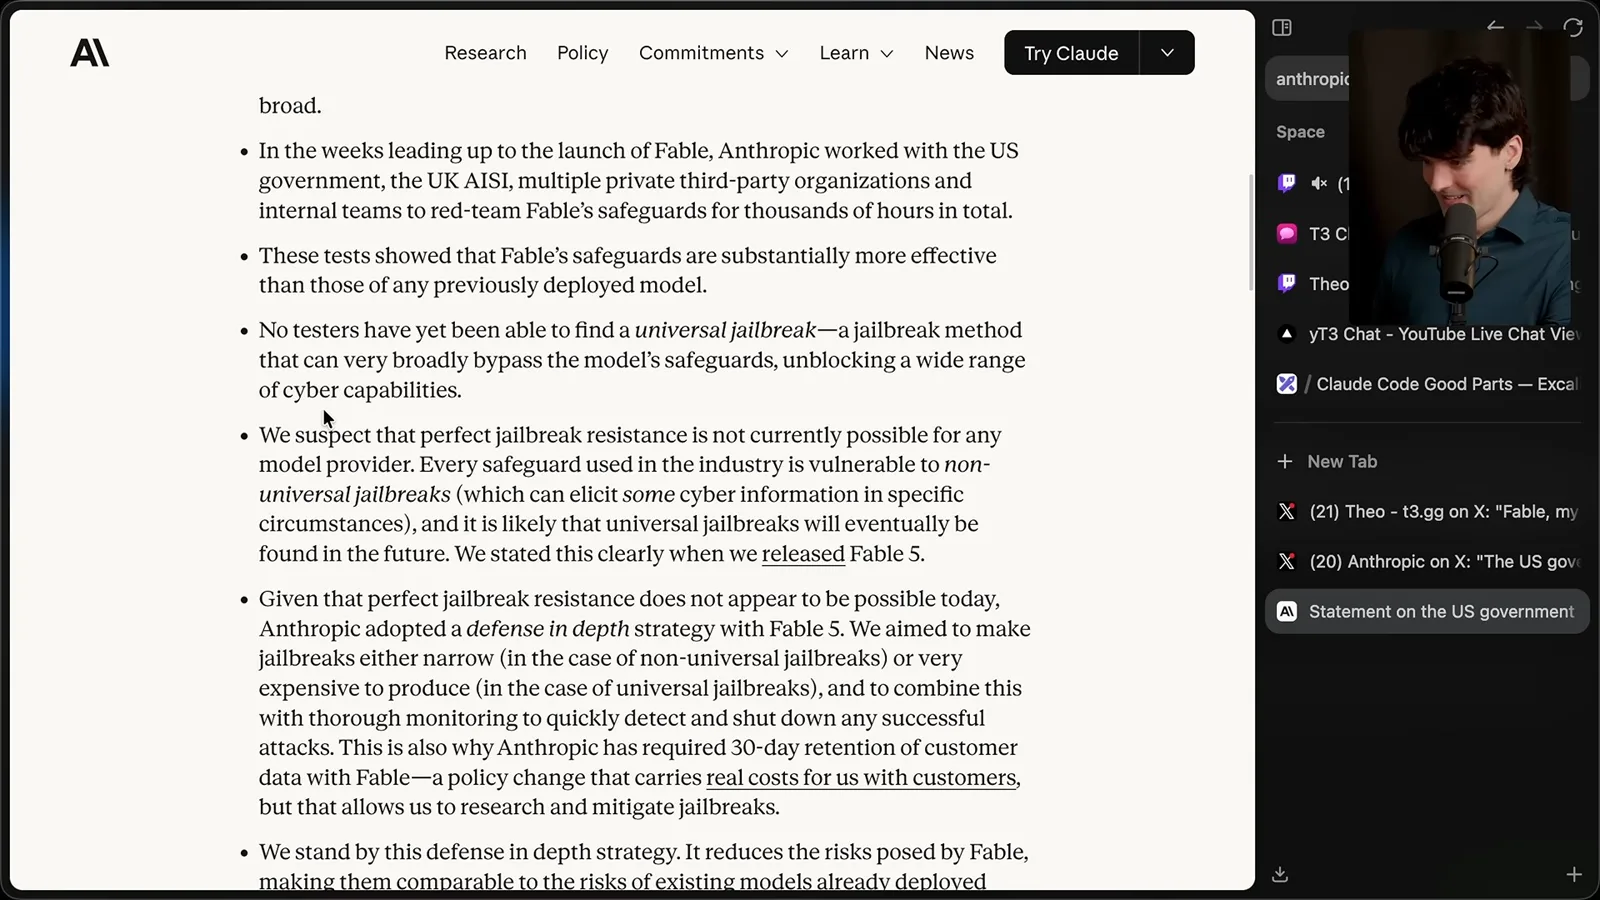
Its defense-in-depth approach combined safeguards with monitoring to detect and respond to potential bypasses. Anthropic also connected its 30-day customer-data retention requirement to investigating and mitigating jailbreaks, while acknowledging that this policy had costs for customers.
Anthropic argued that disclosed narrow findings did not demonstrate a harmful result unique to Mythos and that comparable capabilities existed in other models. I agree with the company’s concern about the response, though we only have its account of the evidence at this point in the story.
The company said the government had supplied verbal evidence of a potential narrow jailbreak involving reading a codebase and fixing flaws. It said similar capability was available elsewhere, including in GPT-5.5, and emphasized that defenders also use such tools to keep systems safe.
Policy and uncertainty
Anthropic calls for a transparent process; Theo considers Dario Amodei’s policy essay. He closes with a developing picture and an unverified speculation about motive.
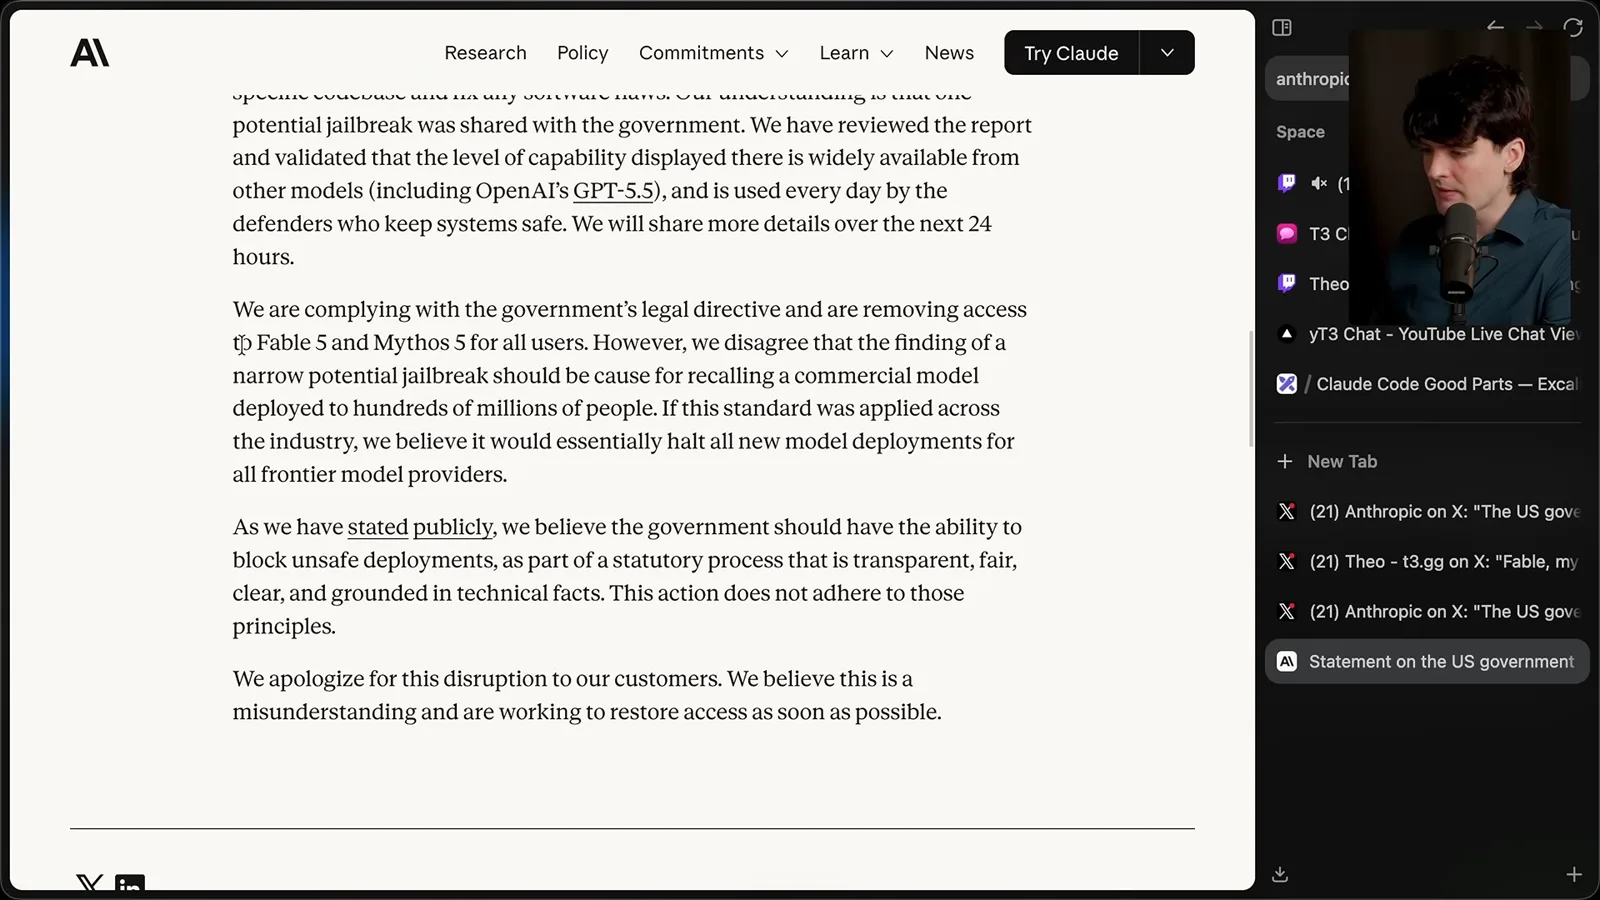
Anthropic said it was complying but disagreed that this potential narrow jailbreak justified removing access to commercial models. It argued that government intervention should follow a transparent, fair and technically grounded statutory process, and said it was working to restore access.
I turn to Dario Amodei’s essay on AI policy. He argues that legislation moves slowly while AI capabilities may develop quickly, making it difficult both to prepare for risks and to design rules before their effects are clear. He describes transparency measures, chip export controls and labor-impact data as partial steps.
Amodei also argues that advanced models can have strategic cybersecurity consequences and that biological or autonomy risks could follow. These are his risk assessments and projections. I find the essay relevant because it discusses the policy machinery now affecting the company’s own model.
As I record, access still appears to work in one interface, and people are building status pages to watch when the API stops responding. The situation is developing; an announcement, a user interface and actual availability may not change at exactly the same time.
I wonder aloud whether the action could be retaliation related to Anthropic’s position on AI laws. I have no evidence establishing that motive, so it is speculation rather than a finding. At this point I am working from the company’s official statement and expect more information later.
For now, I hope access can be restored and feel for people who depend on the model, including colleagues outside the United States. The story was still developing when I recorded this, and my reaction reflects the uncertainty of that moment.
同じチャンネルの記事
 38:47EN
 Theo - t3․gg· 2026年10月28日Theo’s Long-Running Agent Experiments: Verification, Compute and CostTheo Browne · Ping LabsA skateboard game and two compiler projects show how repeated checks and flexible compute can sustain agent work—and how expensive those loops can become.
 36:07ENTheo - t3․gg· 2026年10月27日Theo on Token Costs, Coding Agents, and the Price of AI CapabilityTheo Browne · Ping LabsA viral estimate of Lauren's AI spending prompts a closer look at cache pricing, benchmarks, and the changing work of coding agents.
 30:37ENTheo - t3․gg· 2026年10月26日Theo’s Three Skills for Reviewing and Shipping with Coding AgentsTheo Browne · Ping LabsHow sol-loop, full-send and full-stop encode review, verification and different levels of merge authority.
 0:43ENTheo - t3․gg· 2026年10月23日Theo Distinguishes Security Vulnerabilities from Active AttacksTheo Browne · Ping LabsA short explanation of why disclosed software flaws and reported attacks are different kinds of security news.
 29:22ENTheo - t3․gg· 2026年10月22日Theo on Security Vulnerabilities, Stolen API Keys and AITheo Browne · Ping LabsA look at the gap between vulnerability disclosure and patching, and a speculative account of why stolen inference keys may be valuable.
 31:13ENTheo - t3․gg· 2026年10月20日Theo on Why Smarter Models Help More Than DevelopersTheo Browne · Ping LabsFrom game modifications to compiler experiments, Theo revisits his assumptions about who benefits from more capable AI.