En 30 secondes
Evan Kormos describes introducing agents into policy-driven workflows by mapping outer dependencies and bounded inner loops. He argues that reliable checks, representative evaluations and execution traces are necessary to build confidence. He proposes starting with full supervision, moving to sampling when measured performance meets a policy threshold, and later concentrating human attention on exceptions. Consequential decisions and accountability can remain human-led.
- 1The outer workflowA DAG represents dependencies while allowing independent checks to run in parallel.
- 2The inner loopWork can be reviewed and revised within a bounded node.
- 3Quality of the checkMore iterations do not help if the acceptance check is unreliable.
- 4Evidence for confidenceRepresentative evaluations and traces complement traditional tests.
- 5Staged supervisionBegin with human verification, then consider sampling and exception handling.
À retenir
- Map dependencies and policy gates before assigning work to agents.
- A feedback loop is only as reliable as its acceptance check.
- Use representative evaluations and traces to build evidence.
- Faster steps can move bottlenecks elsewhere in the process.
- Reduce supervision in stages only when measured performance supports it.
Lire le texte remanié, chapitre par chapitre
Policy and the running system
Kormos distinguishes organizational rules from evolving operations.
I have spent twenty years delivering and building software, including fifteen in enterprise financial services. At Coinbase, I work on how to trust agents in workflows governed by policy.
A policy defines how an organization expects work to be done, including risk and compliance. I think of it as institutional intent: it uses words such as “must,” “may,” and “should” to set boundaries.
The written policy and the running system are distinct. Policy is revised at particular moments, while products and operations keep changing; the implementation must remain within the relevant rules.
Agents cross the familiar categories of people, process and technology: they collaborate with people, perform parts of a process and use technical tools. Today I focus on where they meet process.
Graphs, loops and exceptions
He maps dependencies, iterative steps and changing bottlenecks.
Map the workflow first. For example, an account may need verification before opening, or a change may require approval before release. Dependencies and gates should be explicit.
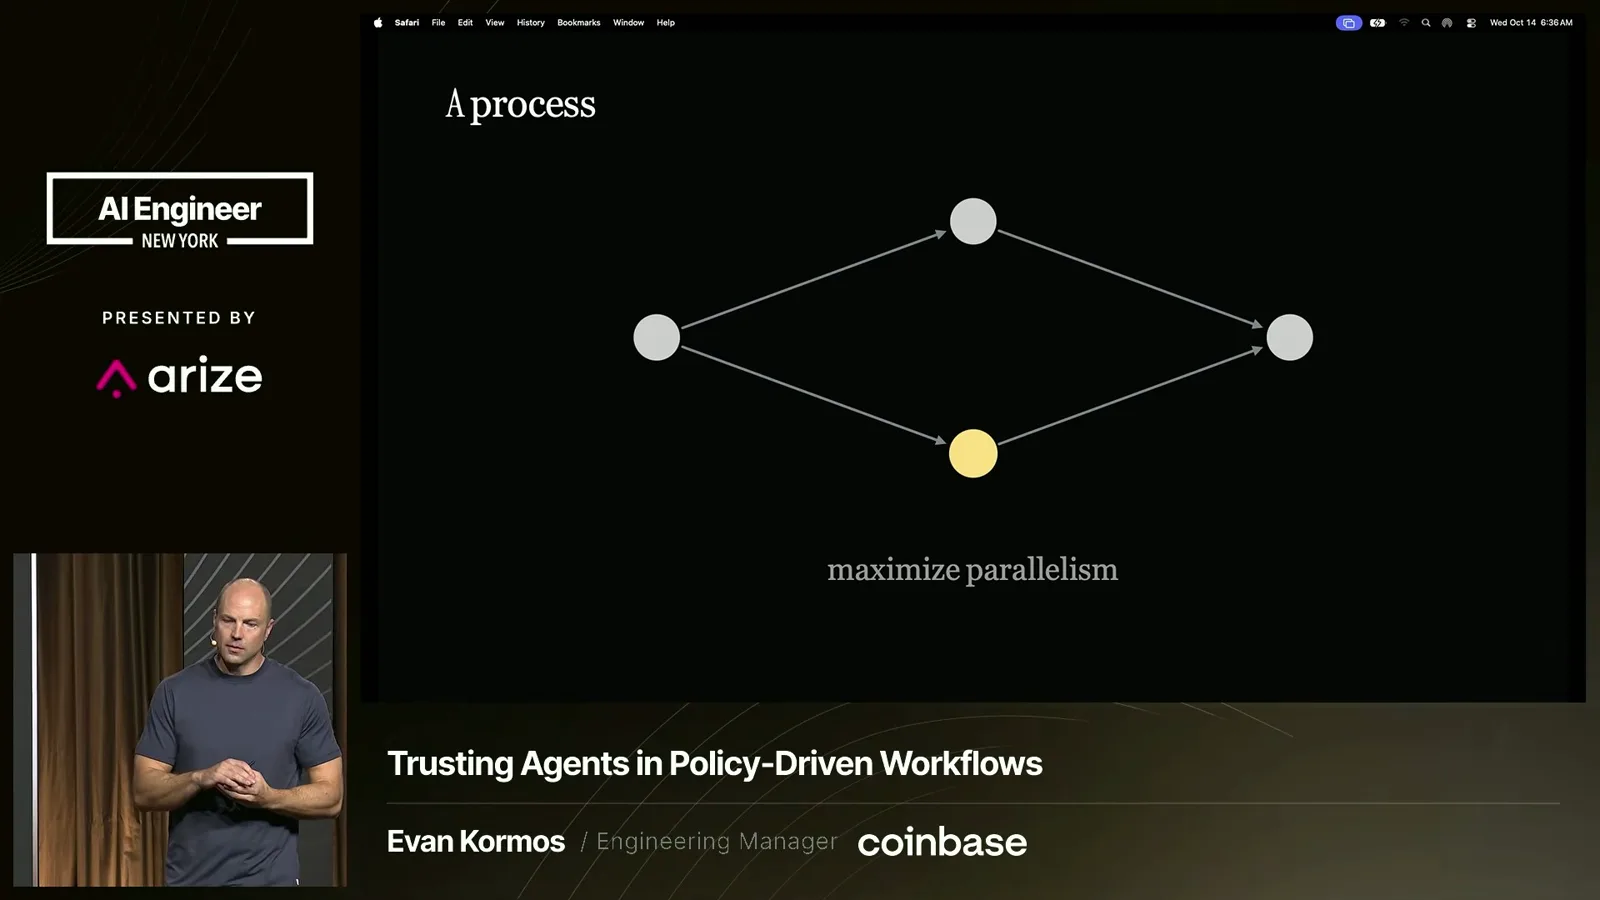
A directed acyclic graph, or DAG, represents steps and dependencies in a forward-moving process. Independent reviews can run in parallel, then converge without eliminating required checks.
Kormos points to Apache Airflow as one tool for defining such dependencies and gives lending, token-listing and software-delivery workflows as examples.
Inside a workflow node, the work can instead be iterative. In code review, a change is checked, feedback is applied, and the cycle repeats until it meets the acceptance criteria.
A cyclic graph can describe this inner loop; tools such as LangGraph can help manage its state. The overall example is simplified, and real workflows may be much more complex.
The outer process supplies a policy boundary, while people and agents may collaborate within individual steps. The two levels answer different questions: what may proceed, and how work is improved.
Design exception flows as well as the happy path. A canceled change or failed security check should be visible and routed appropriately rather than becoming silently stuck.
Speeding one step changes the load on others. Faster code review, for example, can move the bottleneck to design or security scanning, so teams need process-wide metrics.
Operational visibility becomes especially important as work is parallelized. Add capacity where needed without discarding the controls that the process requires.
Context and quality checks
He discusses inputs, output variability and reliable evaluation.
AI inputs and outputs vary. Kormos argues that better context can improve output quality and cost efficiency, though the actual benefit depends on the task and implementation.
One way to provide context is to tell an agent its position and state in the broader DAG. That lets it understand how its work relates to the surrounding process.
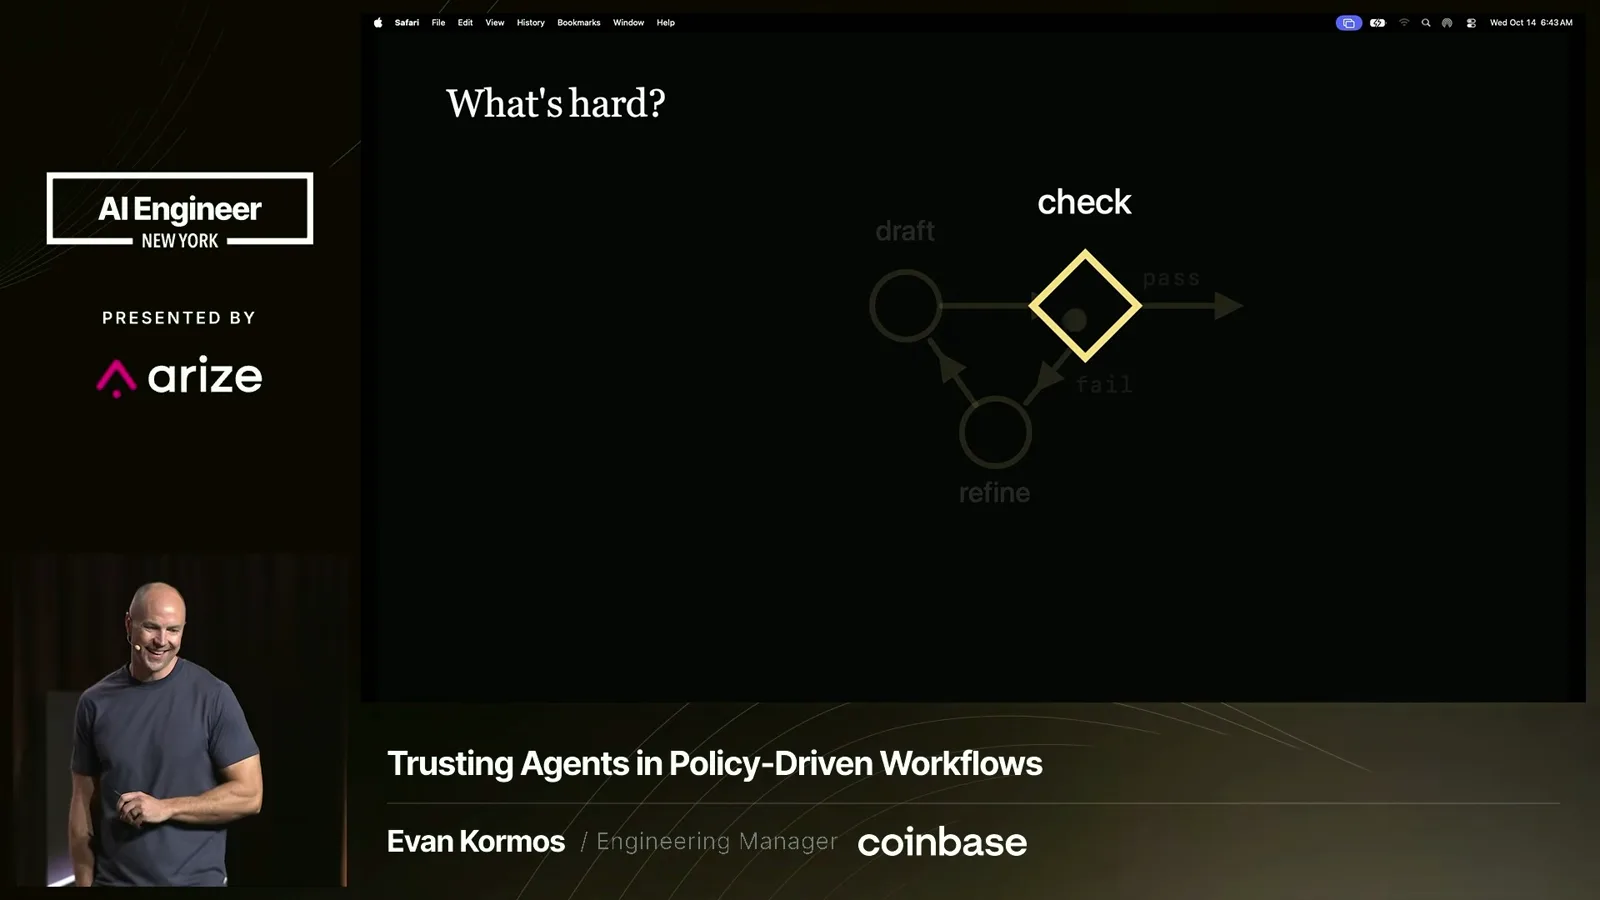
The check decides whether work is good enough to move forward. More iterations do not automatically improve the result: a loop is only as trustworthy as the check that evaluates it.
Traditional software uses tests as a confidence mechanism. Agent outputs are probabilistic, so the same request may have several acceptable answers rather than a single exact match.
Build representative evaluation datasets, define quality with domain experts, and run repeated evaluations across outputs. Examine results statistically instead of relying on an impression of one model response.
Traces show what happened during execution and complement evaluations. Together they provide evidence for whether an agent is behaving acceptably in its workflow.
Where agents belong
He proposes criteria for choosing nodes and keeping consequential decisions human-led.
For each node, ask whether the work can be checked against policy, bounded in a loop, traced and handed back to a person. A node satisfying these conditions may be a better automation candidate.
Not every decision must be delegated. Kormos suggests that a consequential decision against policy may remain human-led even when agents assist elsewhere in the workflow.
Reducing supervision in stages
He moves from verification to sampling and exception handling when evidence supports it.
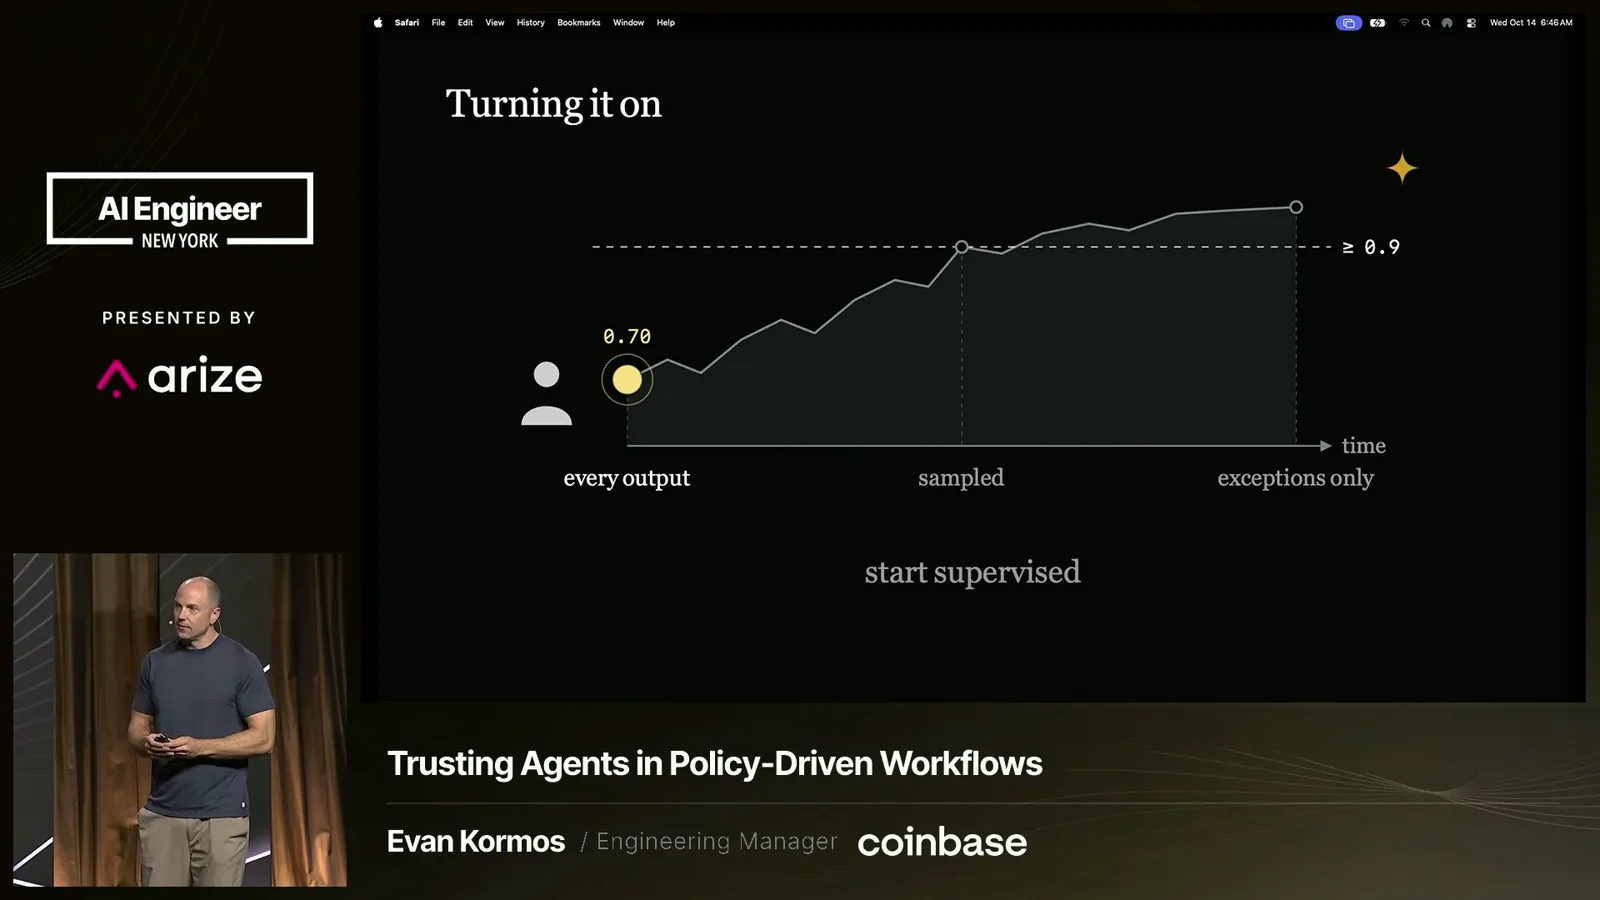
Start with supervision: people verify outputs, domain experts define what good looks like, and the team improves the evaluation dataset and checks.
If measured performance reaches an appropriate policy threshold, move to sampling. Humans examine a subset while systematic evaluations and traces monitor the outputs they do not inspect.
Only after further evidence supports it should people focus mainly on exceptions. They still help update datasets, checks and quality standards; reduced review is not the same as eliminating accountability.
The design principle is to keep the outer process controlled and predictable while allowing bounded adaptation inside a step. Evaluations provide evidence, not an unconditional guarantee.
Quality is a team effort: engineers, domain specialists and process owners must carry product signals into the evaluation and delivery pipeline as agents change how work moves.
Sur la même chaîne
 21:32EN
 AI Engineer· 29 oct. 2026Shy Ruparel on AI agent reliability and recovery after failuresShy Ruparel · TemporalTemporal’s survey finds a gap between frequent agent use and dependable deployment. Ruparel demonstrates a synthetic payout workflow that resumes after workers stop.
 14:50ENAI Engineer· 29 oct. 2026Cole Gannaway on code review, cross-repository risk and AI software factoriesCole Gannaway · QodoA one-line rename can pass local checks while affecting distant clients. Qodo’s Cole Gannaway explains how review context, shared rules and independent agents can expose those risks.
 11:47ENAI Engineer· 29 oct. 2026Revolut’s David Abitbol on self-hosting AI coding models at scaleDavid Abitbol · RevolutAbitbol shares engineering delivery trends, GPU-serving costs and latency tuning, then describes controls for operating the tools in a regulated bank.
 21:47ENAI Engineer· 28 oct. 2026Patrick Smyth on Open-Source Supply Chain Security in the AI EraPatrick Smyth · ChainguardChainguard’s Patrick Smyth discusses faster exploitation, malware in dependencies, zero-days and the expanding attack surface around developer workflows.
 14:09ENAI Engineer· 28 oct. 2026Taylor Luttrell-Williams on Finding Logic Vulnerabilities with SonarQube Hunter AgentTaylor Luttrell-Williams · SonarSonar’s Taylor Luttrell-Williams explains how a security agent maps a codebase, investigates logic flaws and presents validated findings alongside conventional scans.
 16:29ENAI Engineer· 28 oct. 2026Chris Vela on Benchmarking vLLM Configurations with Runpod BenchPodChris Vela · RunpodRunpod’s Chris Vela demonstrates a dashboard for comparing LLM serving configurations and choosing performance settings with workload-specific data.