En 30 segundos
GitHub engineer Don Syme describes continuous AI and GitHub Agentic Workflows, using repository maintenance and verification experiments to explore how people and agents can collaborate. He emphasizes bounded permissions, review, quality gates and end-to-end flow.
- 1Individual speed is not team flowMany fast prototypes still require coordination and agreed boundaries.
- 2Continuous AIEvent-driven agent work can complement deterministic CI/CD.
- 3Bound permissions and outputsThe described workflow limits secrets, networking and actions.
- 4Review before a pull requestA report followed by human selection can separate research from changes.
- 5Guardrails enable unattended workSafety controls need ongoing testing and maintenance.
- 6Design the whole systemQuality gates, human override, authorization, costs and audit trails shape reliable automation.
Conclusiones
- AI-assisted individual productivity does not automatically improve team-wide flow.
- Continuous AI applies agents to recurring repository work while retaining deterministic quality gates.
- The described workflows restrict secrets, networking and outputs and preserve human review before merging.
- Audit trails, cost limits, authorization and human override are central design questions.
Lee el texto editado por capítulos
From individual productivity to collaboration
Syme discusses the changing role of agents in shared repositories.
I came into computer science through formal verification, later working on programming languages and developer tools. At GitHub Next, I have been exploring how AI changes software development and collaboration. My examples are experiments and proposals, not guarantees about what every agent can do.
The pace of change is unsettling: tasks that once took large teams can now produce prototypes quickly with agents, although a prototype is not the same as a mature, reliable system. I also underestimated how useful chat would become as a way for people and AI to explore a problem together.
GitHub was built around human collaboration but now hosts increasing AI participation. This raises questions about teamwork, quality, review, deployment and whether existing structures such as merge queues and CI/CD will change.
I use a metaphor: everyone in a meeting is now a wizard who can quickly produce a prototype. Six people might produce six prototypes, but individual power does not automatically create coordination. An agent acting in a shared project can also cross agreed boundaries.
Most AI tools emphasize individual productivity. I am interested in autonomous collaborators that can work within familiar repository processes: answer questions, analyze issues, suggest improvements or help with releases while a maintainer is away, with appropriate limits.
Continuous AI
Recurring agent work complements existing integration and deployment processes.
We began calling this continuous AI in 2025: automated activity responds to changes or events, much as continuous integration and deployment do. The additional category covers tasks that require judgment, while retaining deterministic CI/CD as an important trust boundary.
For example, a large enterprise may need to roll out vulnerability fixes or dependency upgrades across thousands of repositories. Those changes require judgment and coordination. A general automation system could support many such activities rather than requiring a separate tool for every task.
GitHub Actions is interesting because repository permissions can grant bounded access to compute, networking and storage. Adding AI to that environment can combine automation with an existing record of runs, though permission boundaries and costs still require careful design.
Continuous fault analysis is one possible application: collect service failures and telemetry, investigate a cluster of problems and prepare a proposed fix before an on-call engineer reaches the computer. This is a workflow vision; a proposed fix still needs validation.
For maintainers, the goal is to wake up to useful work aligned with the direction they set: perhaps a performance suggestion, an analysis of a feature request or a maintenance improvement. The maintainer should define the automation, decide what is valuable and control its cost.
Because the workflows repeat and leave records, their definitions can be reviewed and improved. I describe examining past runs for failures and converting reliable portions of reasoning into scripts. I also suggest comparing models on identical tasks, while noting that the proposed exam-style testing was not yet implemented.
A shared ledger matters. In my examples, GitHub issues and pull requests provide a familiar place where humans and agents can see and discuss work. Collaboration through that ledger has limitations, but it builds on processes many teams already use.
Agentic workflows and safety
A Markdown-driven implementation uses triggers, restricted outputs and guardrails.
GitHub Agentic Workflows is one implementation. A maintainer checks in a Markdown workflow and runs a compilation and checking step that creates an Actions workflow. The Markdown describes triggers, permissions, allowed outputs and the task for the agent.
Issue triage is an example: when an issue is opened or reopened, the workflow can gather context, assess completeness and propose or apply configured actions. The maintainer chooses what the workflow is supposed to do.
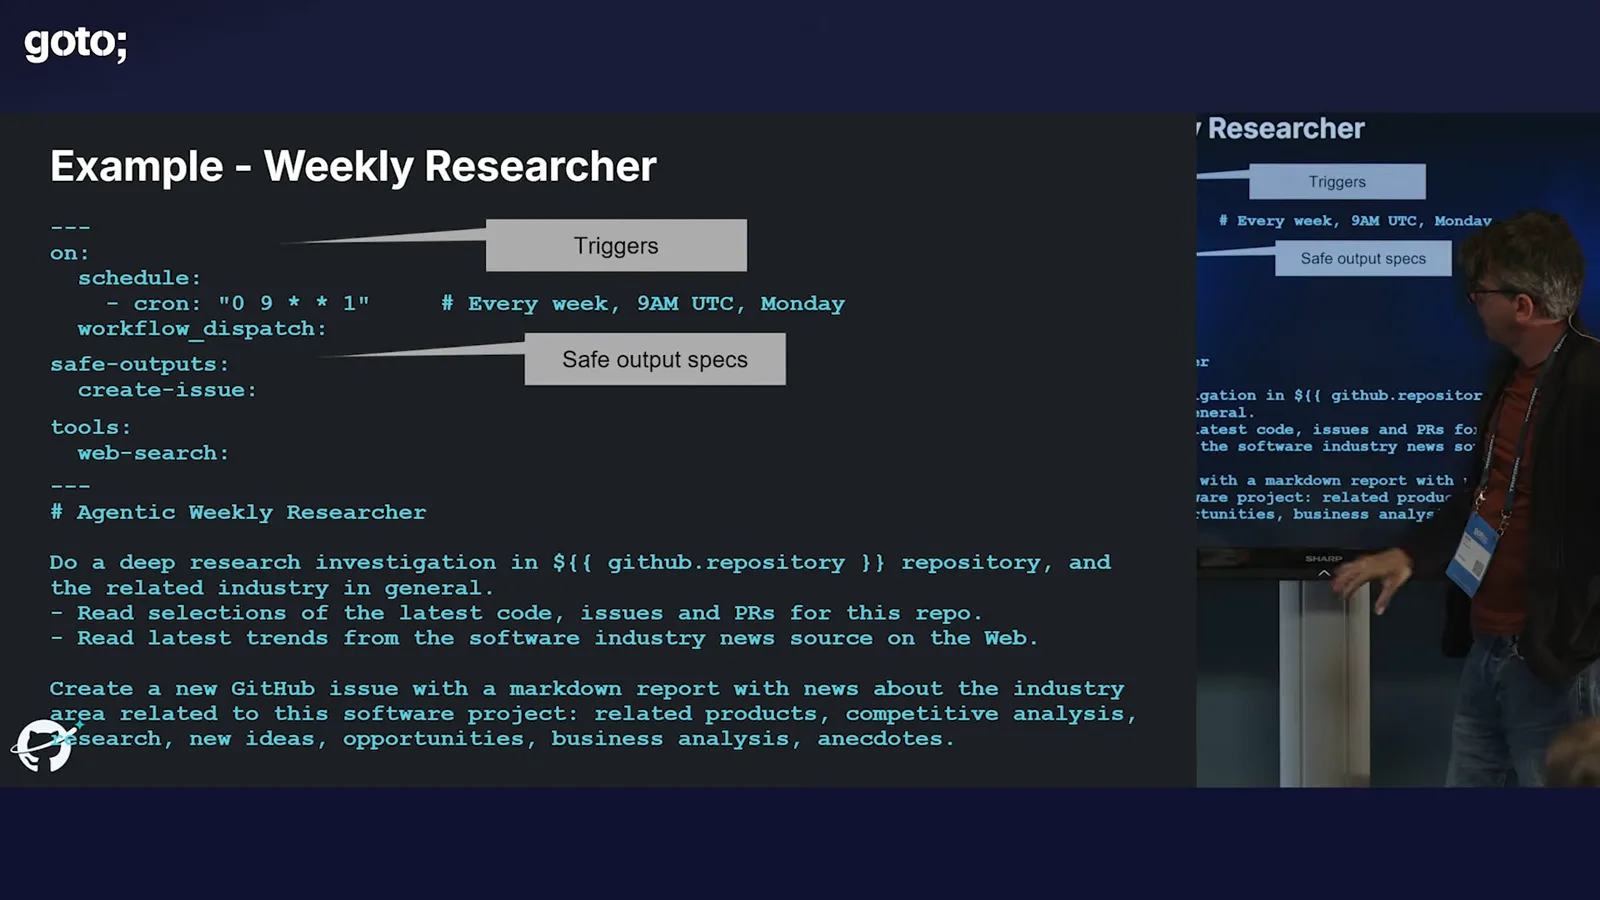
In the architecture I describe, the agentic step has no direct secret access, network access is controlled, and outputs are limited to declared channels. A weekly researcher might be allowed to create one issue rather than freely editing the repository. These are design controls, not proof that all risks disappear.
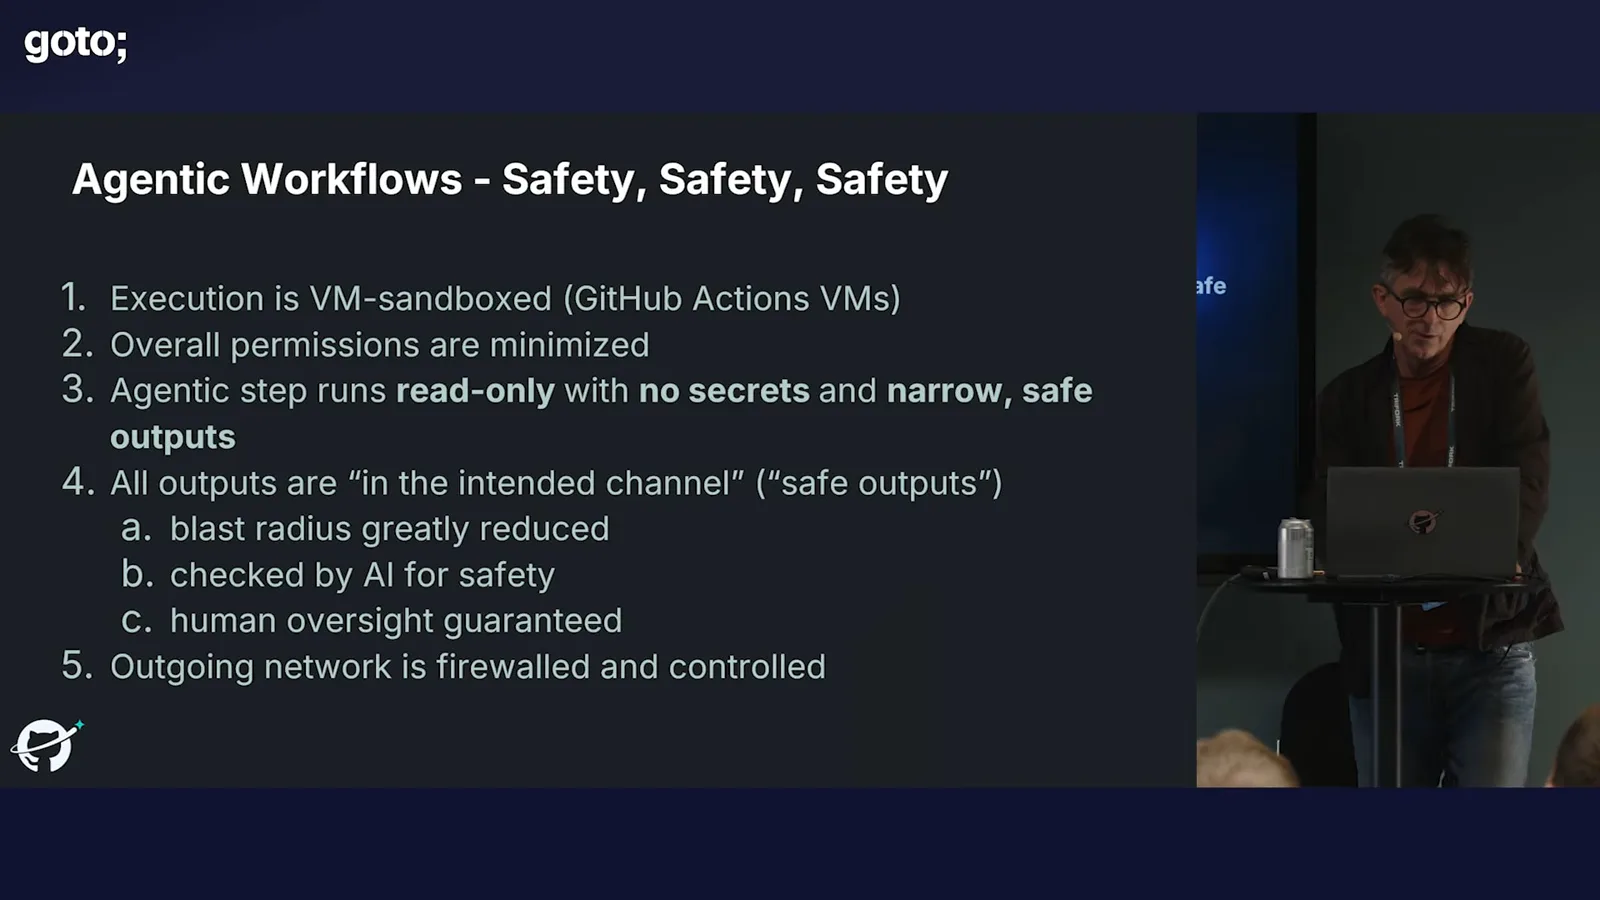
Prompt injection and data leakage are two major concerns. The workflow restricts which outside issues it sees, and public-repository automation should not be given private data or tokens it could expose in logs. The described setup uses sandboxing, minimized permissions, restricted outputs and human review before merging pull requests.
Examples and maintenance
Specialized agents propose code, tests, performance work and repository upkeep.
My colleague Peli de Halleux maintains a collection of specialized workflows, an “agent zoo.” One example examines existing Go dependencies for better ways to use them and remove redundant code. He reported 58 merged pull requests from 74 proposals for that workflow; that is a specific case, not a general success rate.
A useful pattern separates research from changes: an agent writes a report, a human reviews it, and a later step turns a selected idea into a pull request. The issue and pull-request history provides an audit trail for following the chain.
Other possible workflows include improving test coverage and maintaining performance benchmarks. My hope is to make recurring performance work sustainable instead of relying on occasional heroic efforts. More tests or benchmark activity alone do not guarantee better quality.
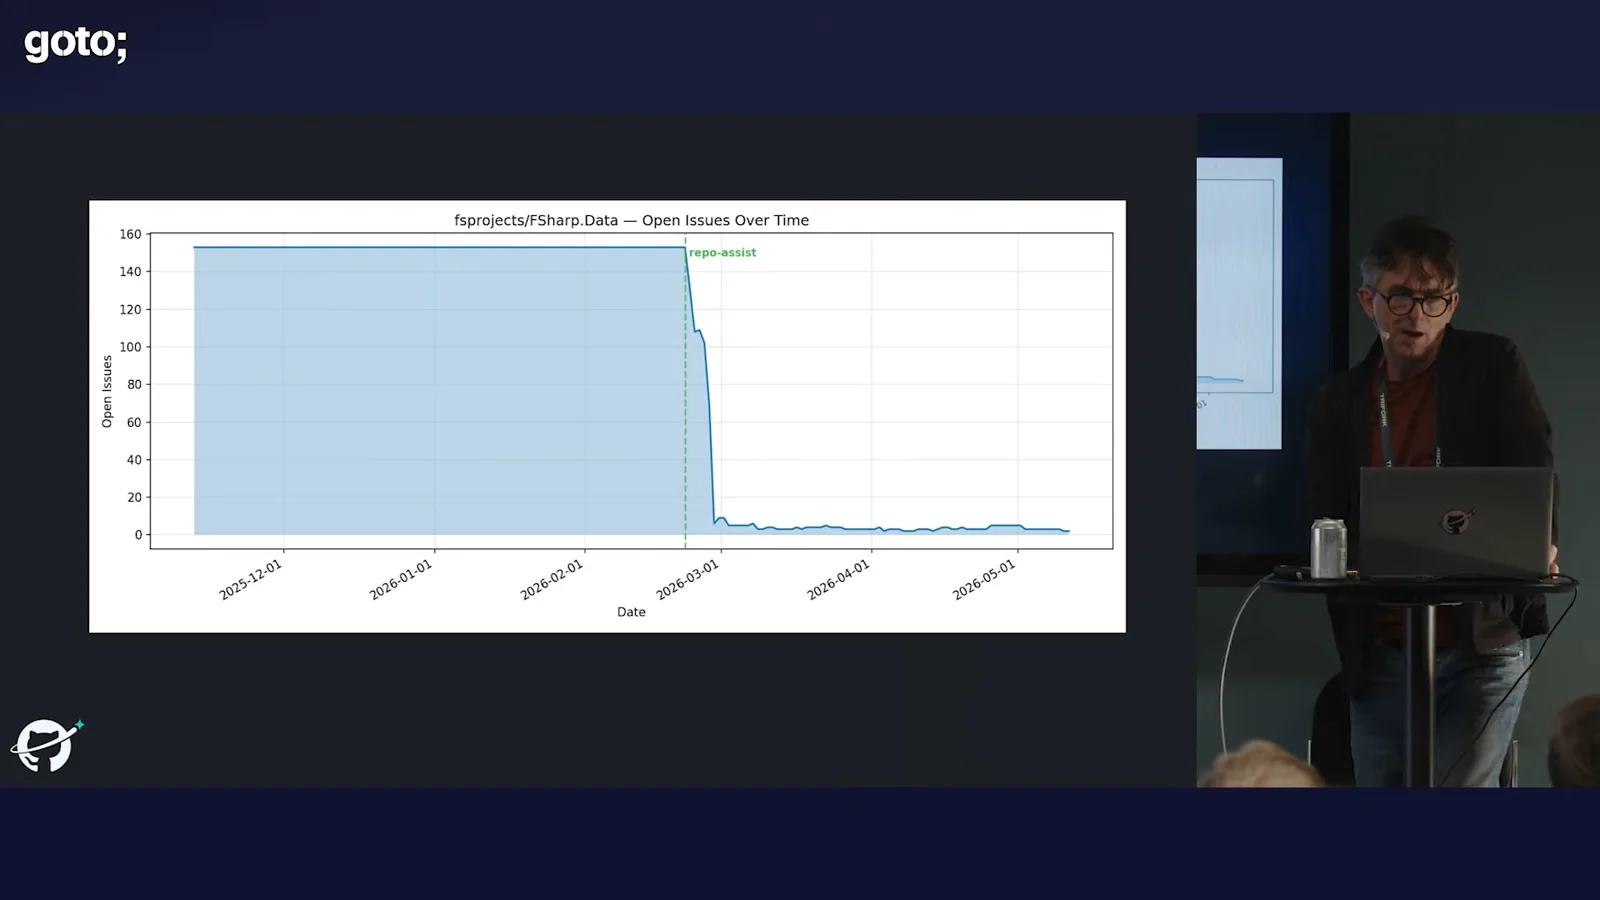
I used Repo Assist on relatively dormant F# repositories. In one example it analyzed old issues, suggested closures or fixes and helped lead to new releases; I reviewed the suggestions. Results vary with backlog size and maintainer engagement, so the example is not a controlled study.
Guardrails can make unattended automation more useful: if the system remains within well-designed boundaries, a maintainer can let it run with less concern. Those boundaries need to be tested and maintained, not merely assumed.
Verification and end-to-end flow
Experiments and design questions focus on quality, control and system throughput.
I also experimented with Lean Squad, a recurring workflow that identifies targets, extracts informal specifications, writes formal specifications, compares models with code and critiques its work. The experiment asks whether this form of automation can produce useful verification work; its value depends on the setting and independent review.
I describe repositories as human–agent knowledge factories, then offer a softer metaphor: software farms. The important question is end-to-end flow. Making each individual produce more can worsen a bottleneck if the rest of the system cannot absorb the output.
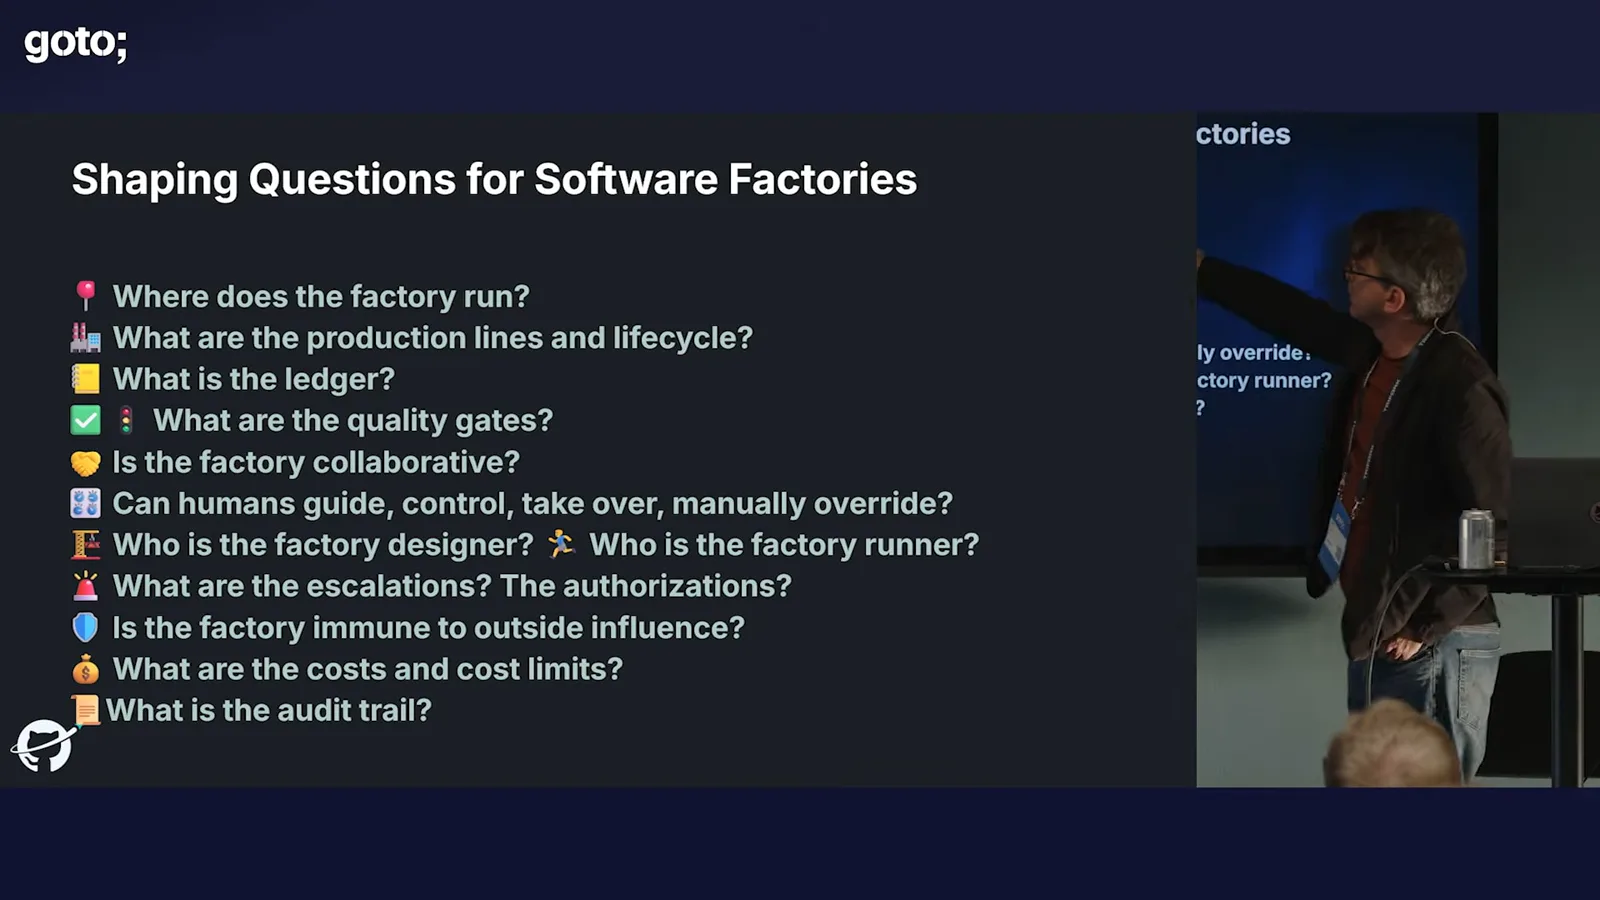
Design questions include where the automation runs, its ledger and quality gates, whether humans can intervene, who authorizes actions, resistance to outside instructions, cost limits and audit history. I describe centrally controlled automation repositories with bounded access to other repositories as one possible pattern.
Más de este canal
 39:12EN
 GOTO Conferences· 28 oct 2026Cate Huston: How Rigour Supports AI-Assisted Development VelocityCate Huston · TwillA two-person team’s experience with release gates, automated checks, prioritization and the cost of shipping faster.
 22:33ENGOTO Conferences· 26 oct 2026William Schor: From Unit Tests to Synthetic Canaries at NetflixWilliam Schor · NetflixHow generated workloads and production-like infrastructure help test a distributed key-value service.
 34:11ENGOTO Conferences· 23 oct 2026Anatoliy Bilenko and Alberto Carretero: Making Database Protocols Reliable with Formal Methods and AIAnatoliy Bilenko, Alberto Carretero · CanonicalCanonical’s database engineers connect executable specifications, model-based tests, failure exploration, and reconstructed execution histories—and explain why none of these techniques proves a real system correct on its own.
 28:15ENGOTO Conferences· 22 oct 2026Steve Poole on Open-Source Security and AI’s Maintenance ChallengeOlimpiu Pop, Steve PooleWhy faster vulnerability discovery increases pressure on maintainers, dependency users and upgrade processes.
 28:23ENGOTO Conferences· 19 oct 2026Learning Ash: Declarative Elixir Apps, Testing and ExtensibilityChristian Alexander, Rebecca Le, Zach DanielRebecca Le and Zach Daniel explain how their book and the framework evolved together.
 38:07ENGOTO Conferences· 9 oct 2026Garrison Hinson-Hasty on Systems Programming with ZigTrevor Berrange Sanchez, Garrison Hinson-HastyA conversation about simplicity, memory, strings, graphics APIs and working with C.