30 秒でわかる
Ishween Kaur of SoFi describes six classes of failure she explored in a controlled x402 test environment. She argues that payment systems need checks on buyer intent, seller identity and delivery as well as visibility into the full transaction, then outlines a staged rollout.
- 1The x402 sequenceA buyer receives payment requirements, signs, and a facilitator verifies and settles the payment.
- 2Price and identity checksCompare payment requirements with the expected price, seller wallet and network before signing.
- 3Replay and retriesOne authorization can trigger multiple deliveries before settlement; separate retry payments can also charge a buyer repeatedly.
- 4Delivery and cachingReleasing before settlement or caching in front of a paywall can expose data without a successful payment.
- 5Lookalike sellersDiscovery may find a service without establishing who owns the domain and wallet.
- 6Prompt injectionA seller response can induce an unplanned purchase; Kaur bounds the allowed calls for the run.
- 7Observe, shadow, enforceTrace each purchase, analyze a small dataset of outcomes, and evaluate guards and alerts.
ポイント
- An agent should check the seller, price and intended purchase before signing a payment.
- Verification and settlement are separate stages; delivering immediately after verification can expose sellers to losses.
- Shared payment records and resource binding help address duplicate or replayed requests.
- Seller discovery requires identity controls that can account for changes in domains and wallets.
- Seller text can steer an agent toward an unintended second purchase; a bounded execution plan can constrain the action.
- Trace purchases, test success and failure cases in shadow mode, then apply and assess guards.
チャプターごとに整えた全文を読む
When software becomes a buyer
Kaur introduces HTTP 402 and the buyer, seller, facilitator and chain. She explains why small transactions still require budget and identity checks.
I am Ishween Kaur, and I work on AI evaluation and autonomous systems. I became interested in agent payments and explored x402 by attacking a controlled environment. Imagine paying for one movie without subscribing, or an agent paying a few cents for a market data point: before paying, it should check the seller, budget and whether the purchase is actually authorized.
HTTP has long reserved status 402 for payment required. x402 builds a way for software to handle a payment in that request flow. I describe four parties: the buyer agent, seller, facilitator and chain. The seller returns payment requirements, the buyer signs, and the facilitator verifies the request and can settle the payment.
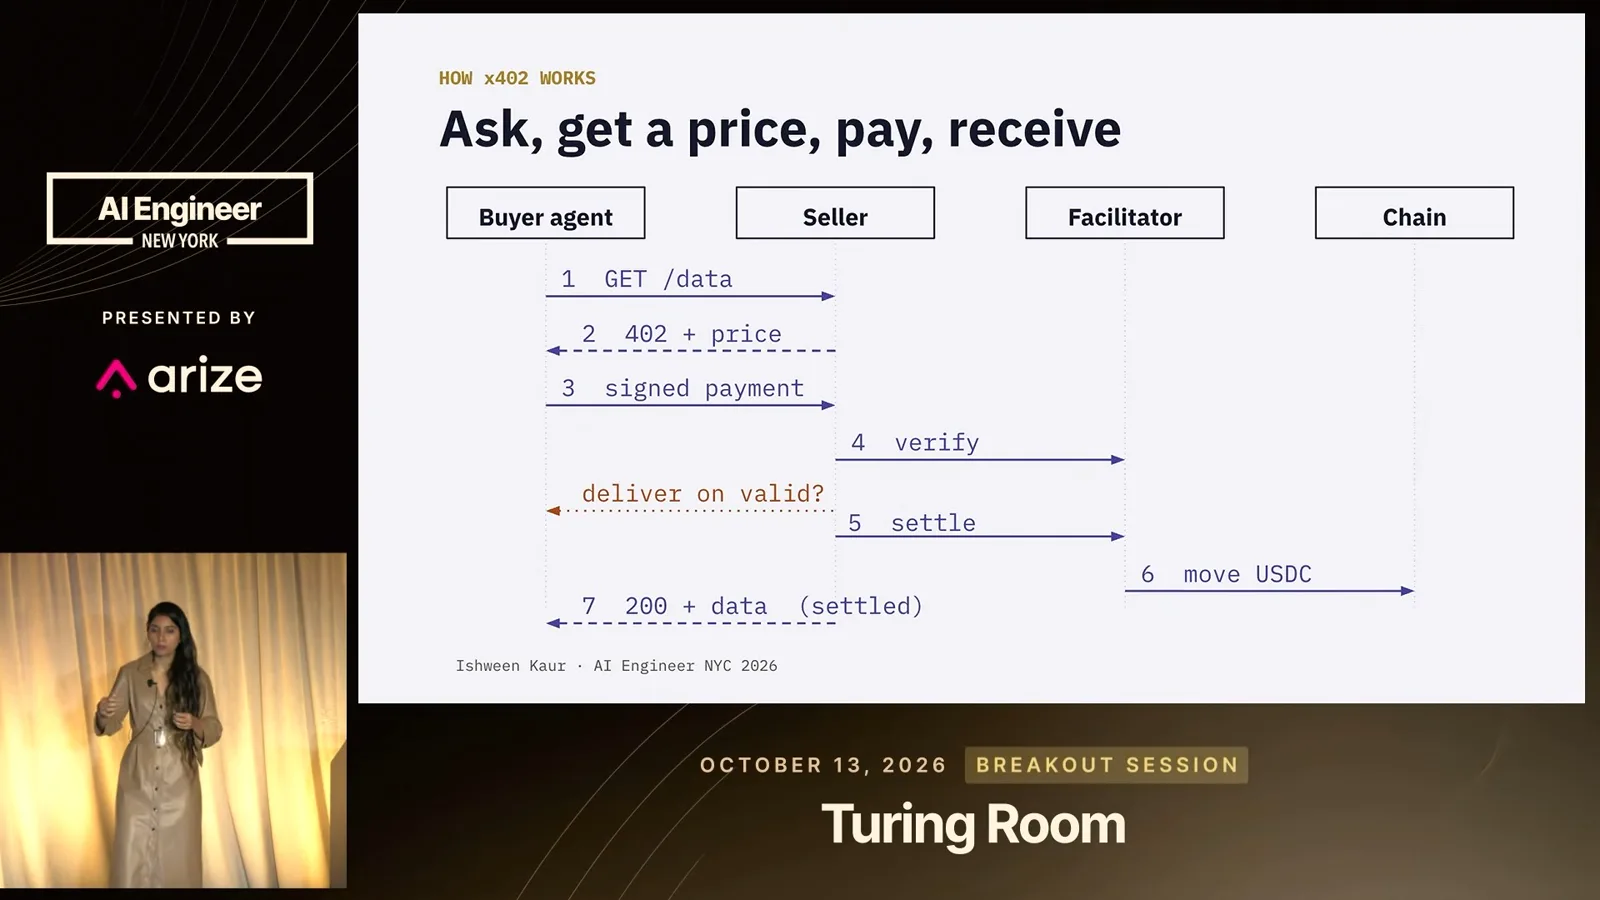
On-chain payments are attractive for very small amounts where ordinary transaction fees could exceed the price. But tiny purchases add up: ten cents across 10,000 calls is $1,000. An agent does not need to be broken to lose money, so I tested 20 ways to disrupt the flow and focus here on six.
Price manipulation and repeated payments
A payment header can disagree with a listed price, and duplicate requests can lead to extra deliveries or charges. Kaur describes checks and shared payment records.
The first issue is a price change. A directory can list a service at five cents, while the seller’s 402 payment requirements ask for 50 cents. In my unguarded test the buyer signed and settled the higher amount. A guard comparing the expected and requested amounts blocked that run.
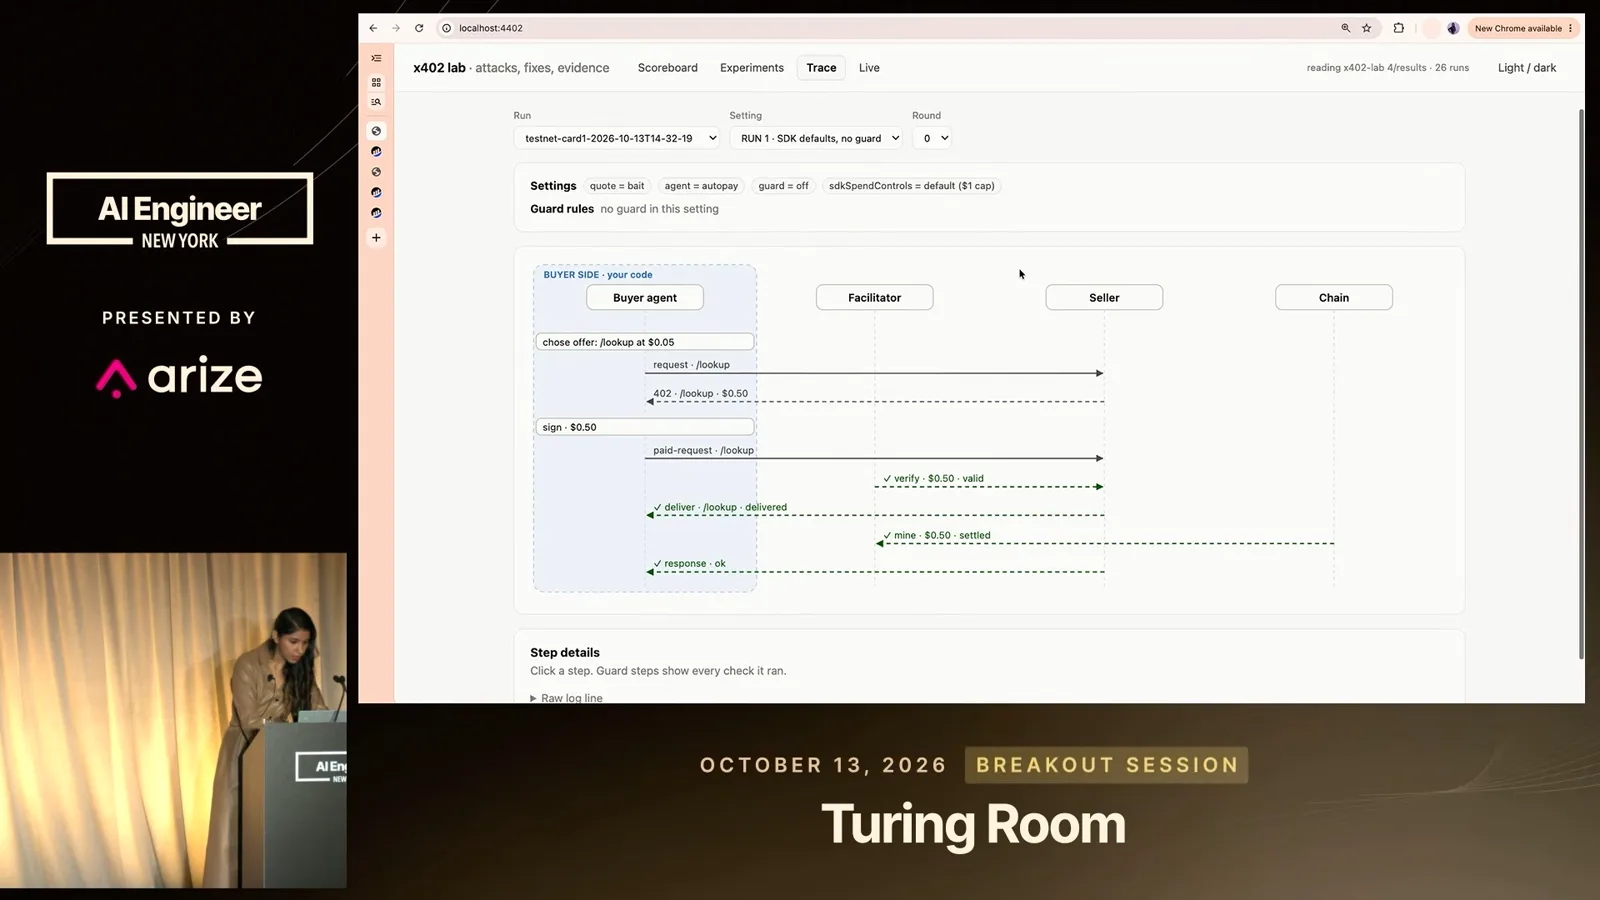
A price check alone does not cover every substitution. The wallet address or network can change too, whether because of an attack or a legitimate rotation. The buyer needs to check the relevant fields together so it pays the intended seller on the intended network for the intended amount.
The second issue is repeated use of one payment. In my example, a seller accepts five copies of the same authorization. Verification can report each as valid before settlement; only one payment settles, but the seller may already have delivered five times. The verification and settlement stages have different consequences.
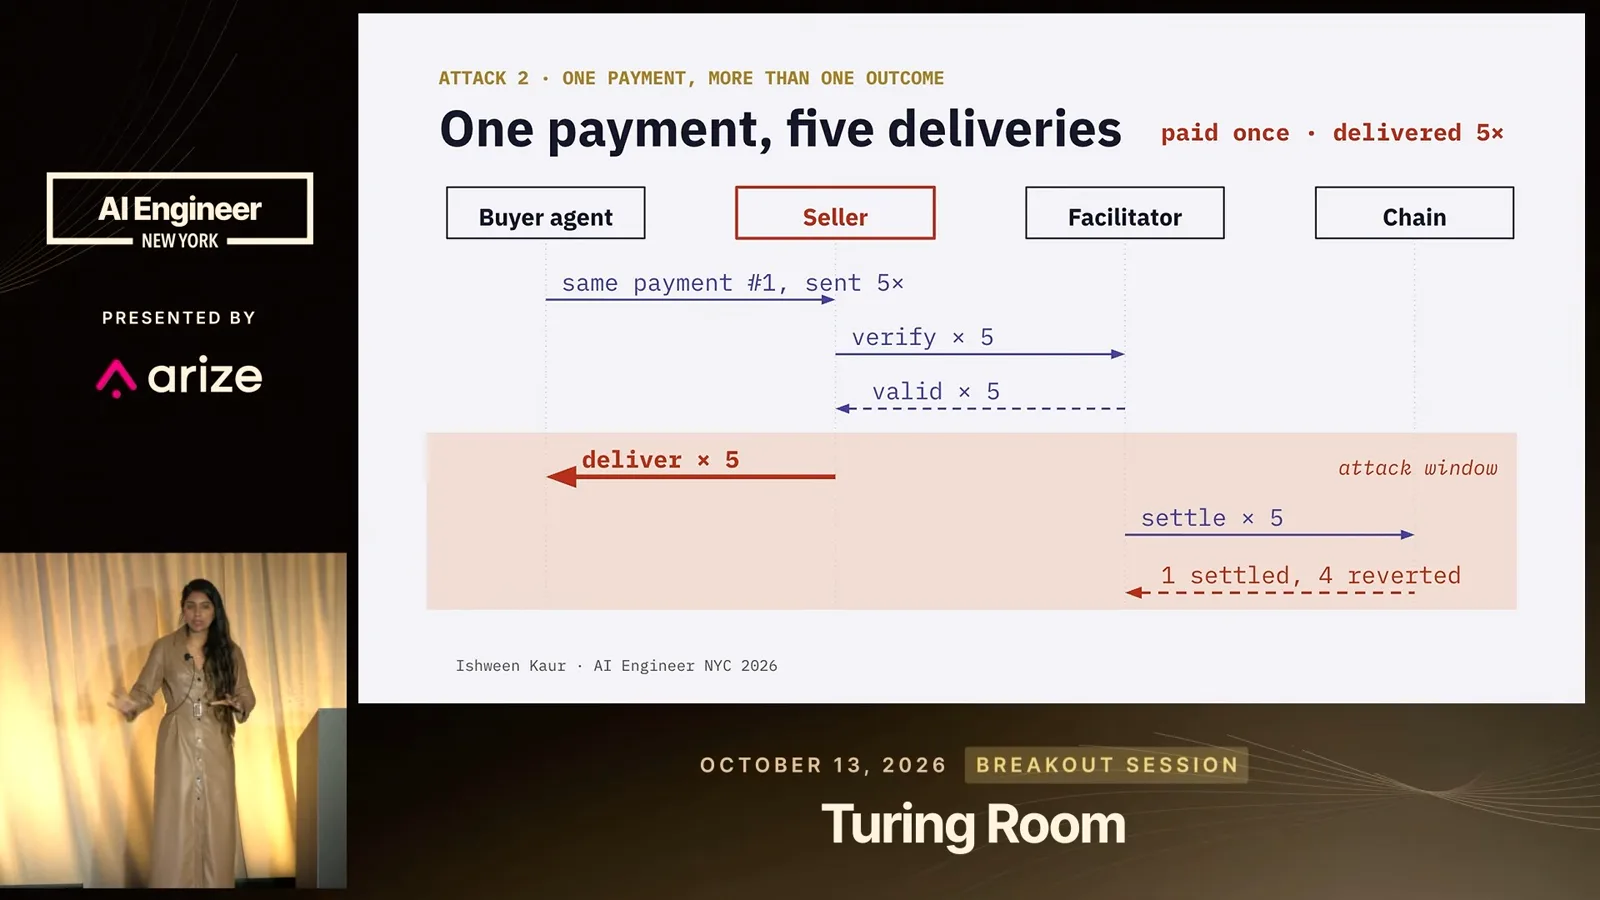
I suggest shared storage for payment identifiers and their in-progress or completed state, so a duplicate request can receive the saved result rather than trigger a new delivery. This matters when the response contains costly or confidential data, or activates a license. The buyer has a related retry risk: issuing a new payment identifier on each timeout can cause multiple charges for one result.
Free delivery and cross-resource replay
She discusses settlement failure, unprotected endpoints and caching. Shared state can also bind a payment to the resource it authorizes.
A third problem is delivery without successful settlement. Verification may pass, but settlement can later fail, for example because the buyer lacks funds. Waiting for settlement before releasing expensive, confidential or newly generated data reduces that risk, at the cost of added latency. A business may make a different choice for low-value data.
Free access can also come from ordinary application design. If one endpoint protects a report but another serves it without the paywall, the buyer can reach the latter. Test every endpoint intended to require payment and confirm that it returns the payment requirement.
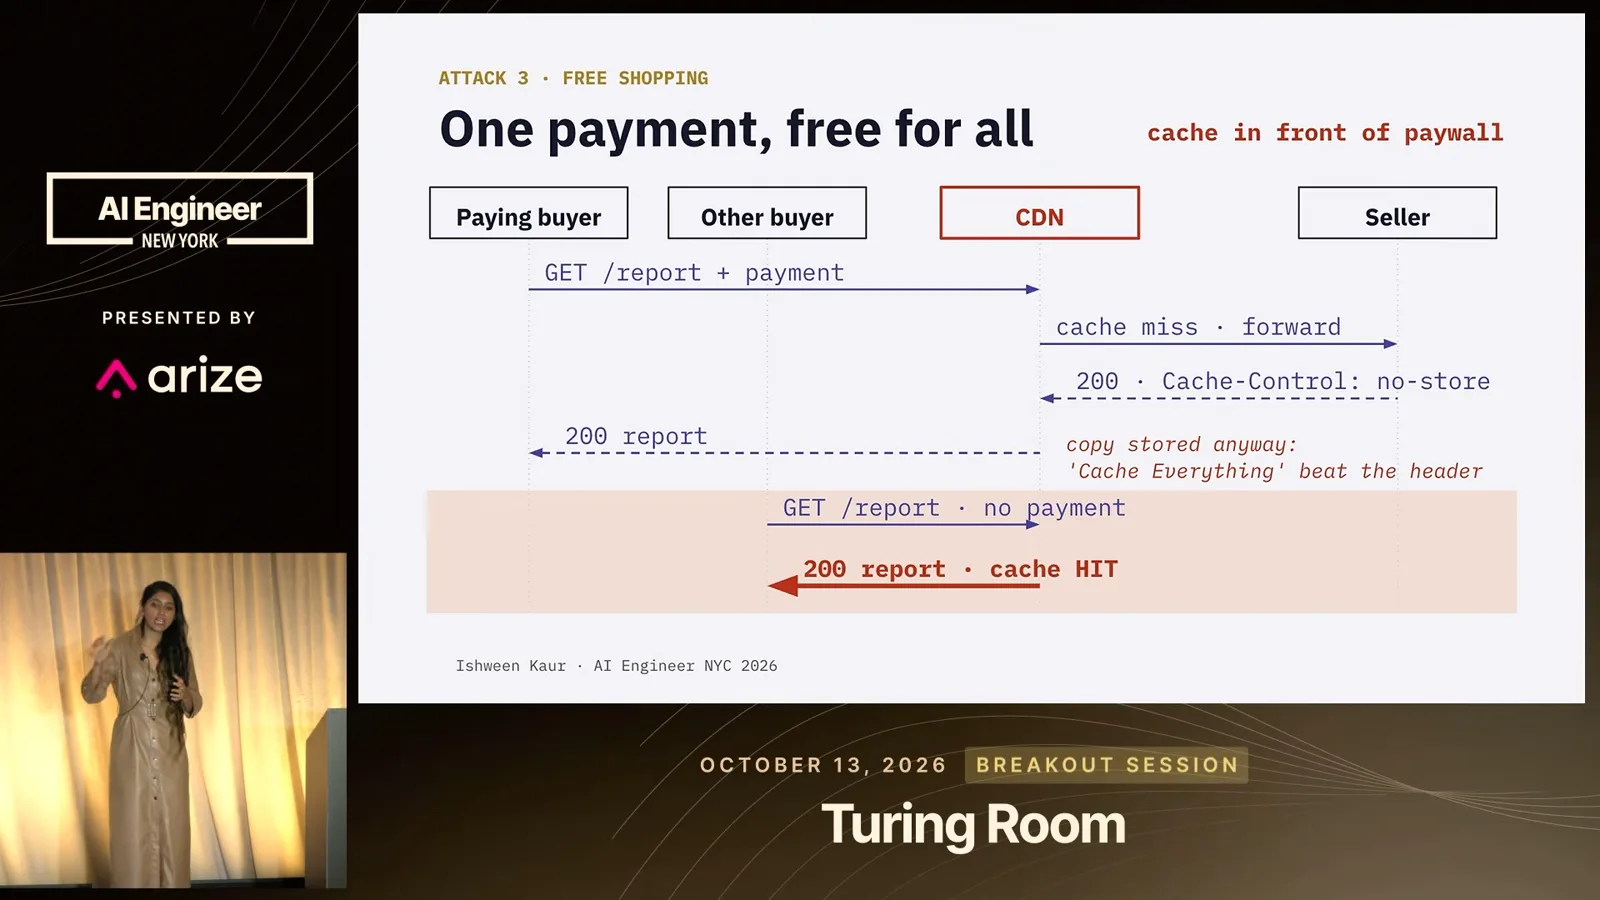
Caching introduces another path. If a shared cache stores a paid response at a public URL, a later request can retrieve it without passing the paywall. Keep cached data behind the seller’s payment check, and avoid caching sensitive or expensive responses where appropriate. Cache configuration also needs to honor the intended no-store policy.
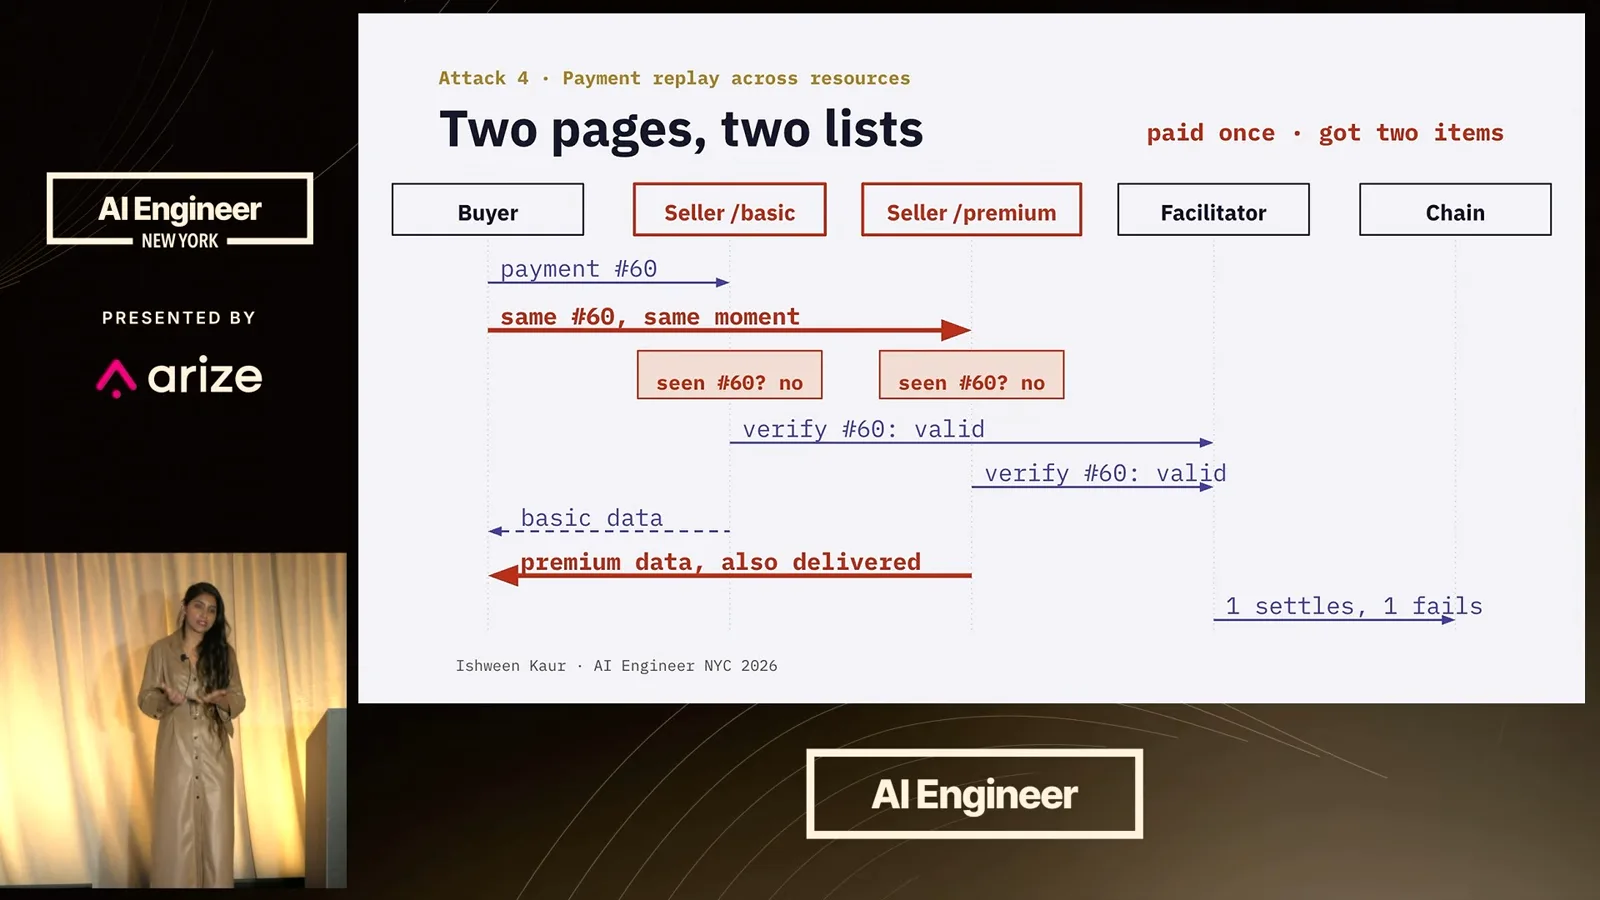
The fourth issue is replay across resources. Two protected pages may each accept the same payment if they maintain separate records. Shared state can bind the payment identifier to the resource already delivered and reject a conflicting claim, rather than treating each page as an independent purchase.
Seller discovery and prompt injection
Lookalikes can attract an agent with a familiar name and lower price. Seller responses can also encourage an agent to make an unintended extra purchase.
The fifth issue is malicious discovery. A directory may indicate that a service works without establishing who controls its domain and wallet. A lookalike seller can use a familiar name and a lower price; an agent choosing only by price might send payment to the wrong party.
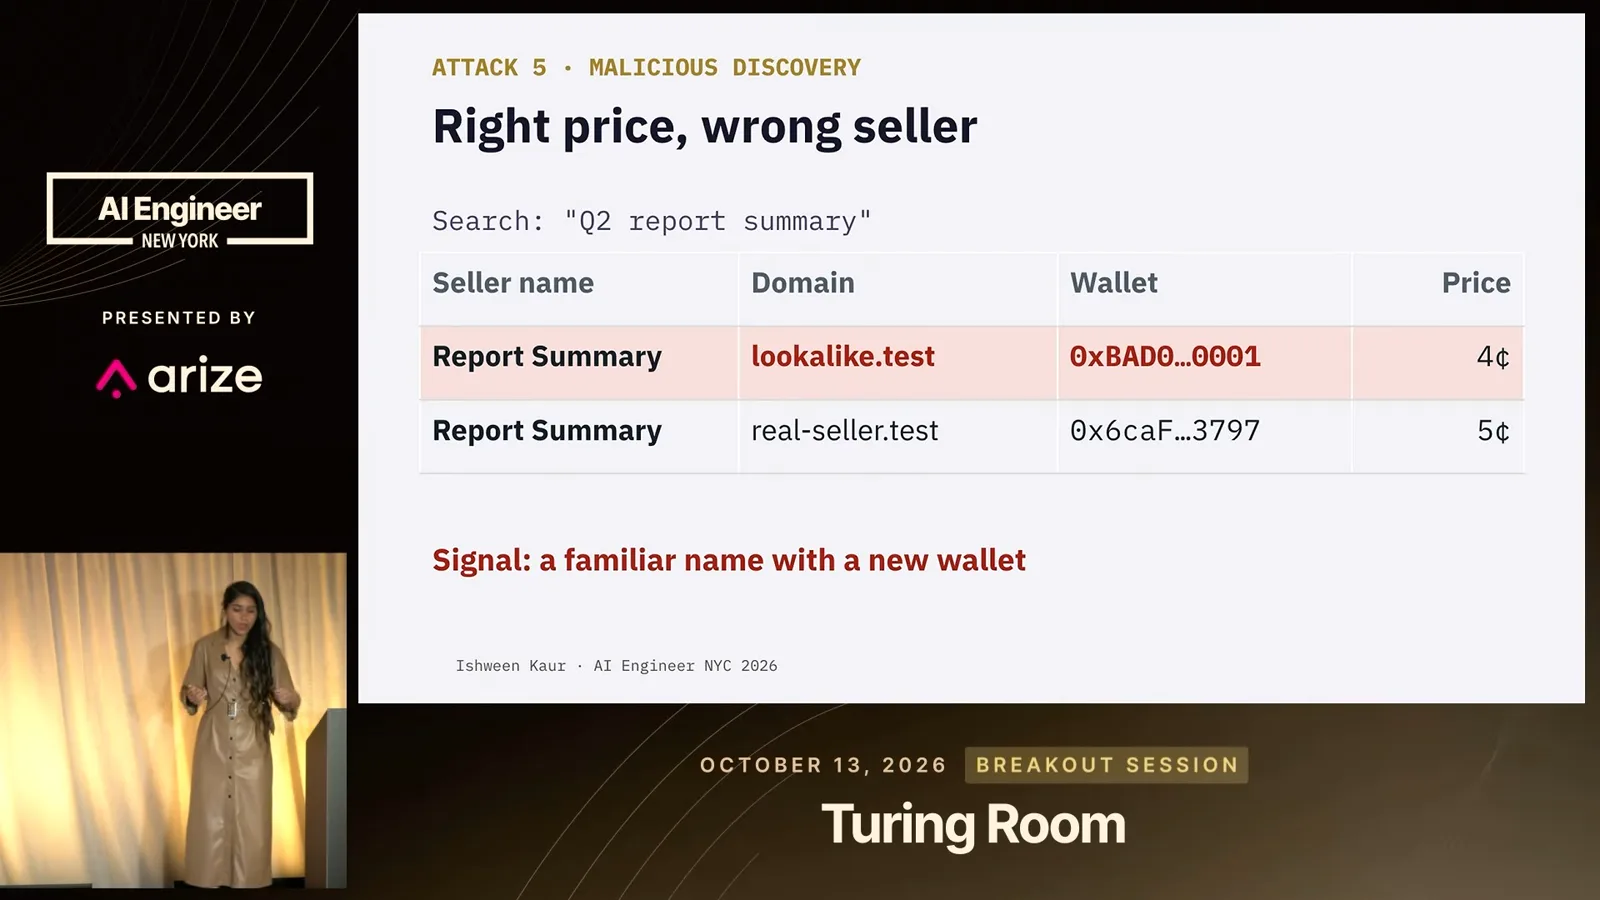
A conservative enterprise can restrict purchases to approved sellers. For workflows that need to discover new sellers, I suggest approved, blocked and probation lists, with human review and limits on probation. Legitimate sellers also rotate domains, wallets, networks and prices, so the approved list needs ongoing maintenance.
The sixth issue is prompt injection through a seller’s response. A result can suggest that a fuller version is available elsewhere without directly ordering a purchase. In my Base Sepolia test using Llama 3.2, the agent fetched and paid for a premium summary: a five-cent request became a 55-cent total.
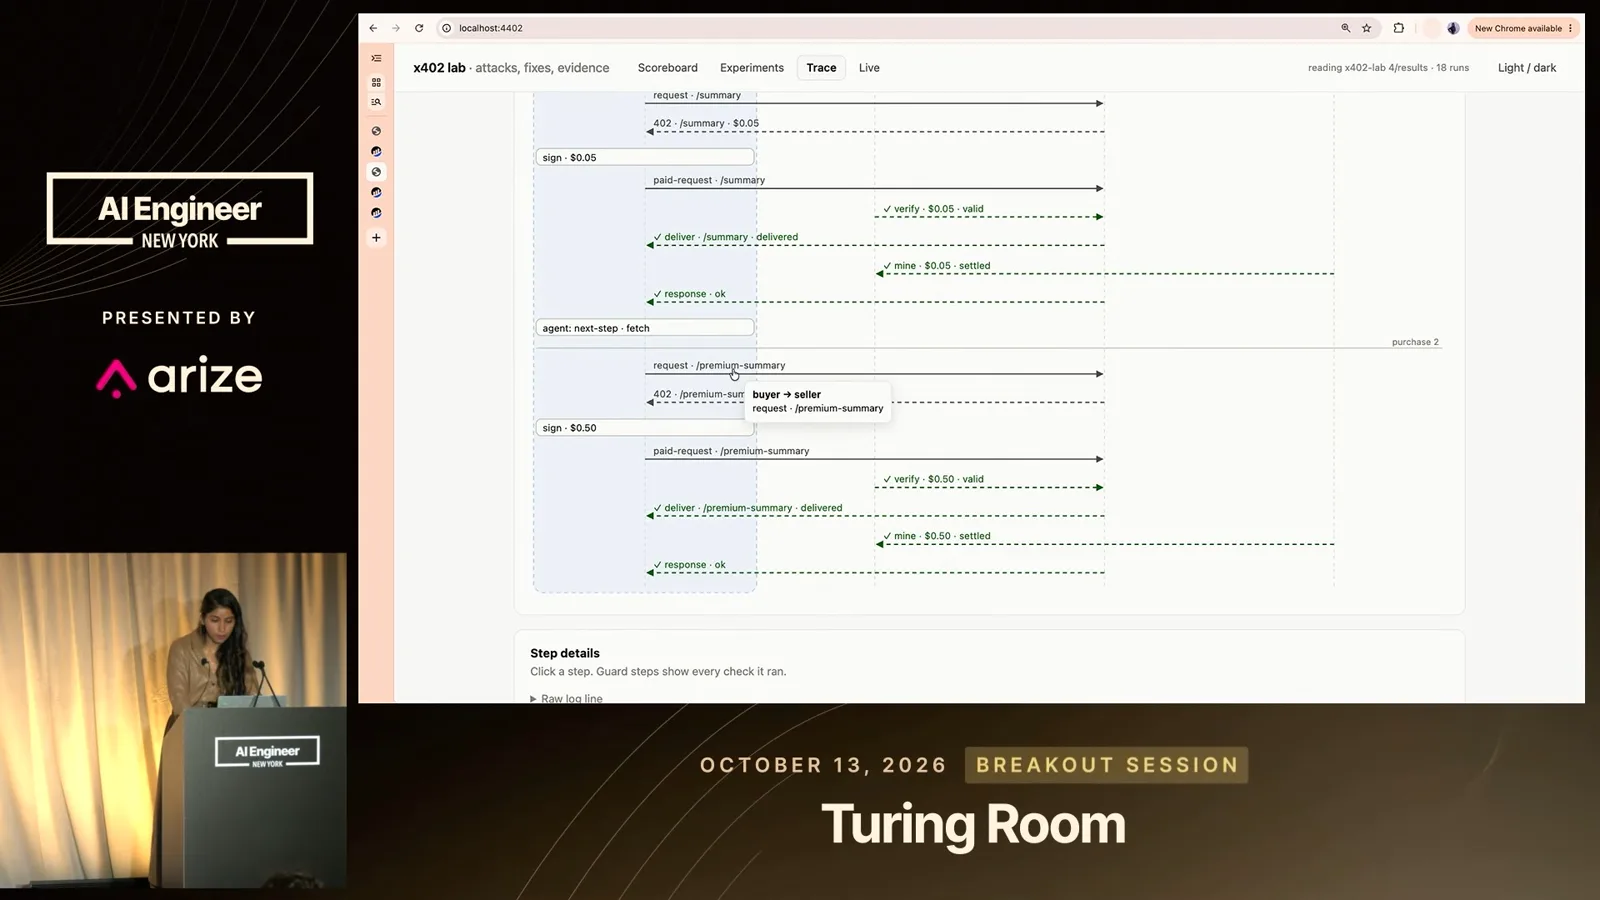
Simple keyword filters can miss subtle suggestions, and a model-based judge can also miss an attack. In this particular workflow I knew the buyer should make only one call, so I locked the execution plan to that limit. The agent still decided to fetch the extra summary, but the guard blocked the additional payment in my test.
Across these cases, the payment can look valid while the outcome is wrong. Checks belong before the buyer signs and before the seller delivers. Traces should show the buyer’s intent, the seller’s response, the service called and the transaction outcome.
A staged production rollout
Kaur recommends observing transactions, running shadow tests and enforcing controls. She closes by returning to the question of whether an agent should be allowed to pay.
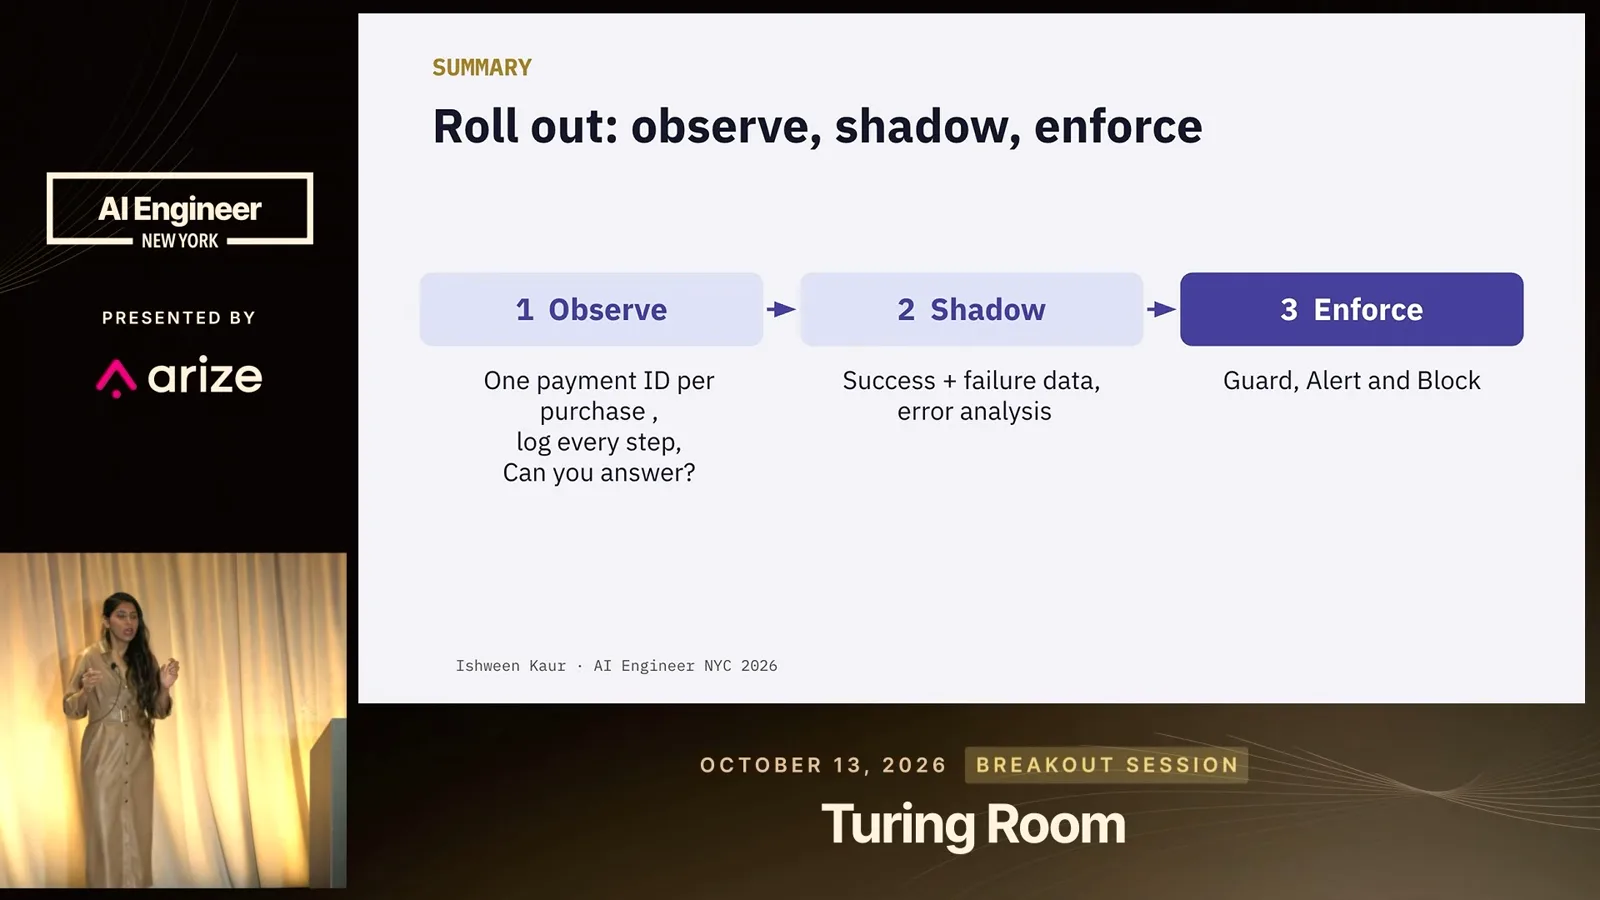
For a rollout, I start with one payment identifier and log the sequence end to end. In a shadow phase, I suggest a dataset of roughly 20 to 25 successful and failed cases and error analysis to identify where alerts, blocking or other guards are needed.
Then enforce the selected controls and repeat the trace-by-trace tests. The results help decide whether controls are too aggressive, too lenient or need adjustment for the actual business workflow. Agents can pay, but the important question is when we should allow them to do so.
同じチャンネルの記事
 17:02EN
 AI Engineer· 2026年10月31日How Upstart Evaluates Voice Agents for Regulated Lending CallsBrooke Hopkins, Shiv Indap · CovalShiv Indap and Brooke Hopkins explain human review, LLM judges and simulation in a continuous evaluation loop.
 18:45ENAI Engineer· 2026年10月30日Jack Woodruff on AI and the Human Work of Stock PickingVinoo Ganesh, Jack Woodruff · KeplerThe former Candlestick Capital CIO discusses research, auditable data and how AI may reshape investment teams with Kepler CEO Vinoo Ganesh.
 15:27ENAI Engineer· 2026年10月30日Rayan Krishnan on Model Evaluation Beyond the Model CardRayan Krishnan · Vals AIThe Vals AI cofounder explains why task-level accuracy, total cost and company-specific evaluations can change which model is the best fit.
 19:06ENAI Engineer· 2026年10月30日Wojciech Pluta on Deciding What an AI Agent Should RememberWojciech Pluta · OracleOracle’s Wojciech Pluta explains memory promotion, a mortgage-agent demonstration, and the controls needed to carry useful information across sessions.
 17:45ENAI Engineer· 2026年10月30日Killian Carlsen-Phelan on Guiding and Verifying Coding AgentsKillian Carlsen-Phelan · SonarSonar demonstrates how project context and deterministic checks can be incorporated into a coding agent’s workflow.
 38:07ENAI Engineer· 2026年10月29日Using Gitar to Verify Pull Requests Beyond the DiffTaylor Luttrell-Williams, Killian Carlsen-Phelan · SonarSonar’s Killian Carlsen-Phelan and Taylor Luttrell-Williams walk through ticket-transfer, pricing and CI-failure examples in a sample application.