30 秒でわかる
Speakeasy co-founder Sagar Batchu reconstructs a reported production deletion to argue that a valid key does not establish valid intent. He presents a governance model and his company’s implementation, then answers questions about escalation, personal information and deployment trust.
- 1A credential is not intentBatchu reconstructs an incident in which an agent’s staging task led to a production deletion.
- 2Connect, identify, decide, recordHe proposes a common governed path with attribution and an audit record.
- 3Intersect three policiesCredential, agent and owner permissions jointly constrain each request.
- 4Appeal and privacyDisputed denials need escalation; personal data handling depends on purpose and deployment.
ポイント
- A valid credential alone does not establish that an agent’s proposed action is authorized for its task.
- Identify the agent, the operator and the original credential authorizer separately.
- Evaluate credential, agent and owner constraints together on each call.
- Record decisions and provide a path for human escalation when a denial is disputed.
- Consider data destination, purpose and deployment when designing privacy controls.
チャプターごとに整えた全文を読む
The production deletion scenario
Batchu recounts an incident and argues that unchecked authority is the key failure.
I'm Sagar Batchu, CEO and co-founder of Speakeasy. We build an AI control plane for governing and authorizing agent actions. I want to examine a reported incident to explain how identity, policy and audit records can create a more intentional path from an agent's request to an external action.
In my reconstruction, a developer asked a coding agent to fix a staging credential issue. The agent found a powerful database token in an unrelated file and chose to delete and recreate a volume; the volume was in production. I say the production database and backup were lost. These are my account of the incident and its circumstances, not a forensic report in this talk.
My point is that a valid credential is not the same as valid intent. The agent can be mistaken without an exploit, jailbreak, prompt injection or malicious actor. In the scenario, I argue the failure was unchecked authority: nothing evaluated the proposed operation before it reached the API.
A governed path
He proposes centrally deployed controls and a four-step decision path.
Businesses already expect people to sign in under their own identities, avoid sharing keys, obtain independent approval for permission escalation and leave records of changes. An auditor wants to know who acted, who authorized it and what happened. I argue that agent actions need comparable attribution and evidence.
The goal is not simply to block agents. If the governed path is harder than the ungoverned one, teams may route around it. Policies should be centrally defined and deployed so that the safe path works when people onboard, without every developer having to recreate those policies in an individual harness.
In one illustrative example, a secret appears in a user prompt or tool request. A runtime hook detects the key before it reaches the model, a policy decision blocks or quarantines it, and the event is logged. I describe an ideal response of around 100 milliseconds or less; that is a design target, not a measured guarantee.
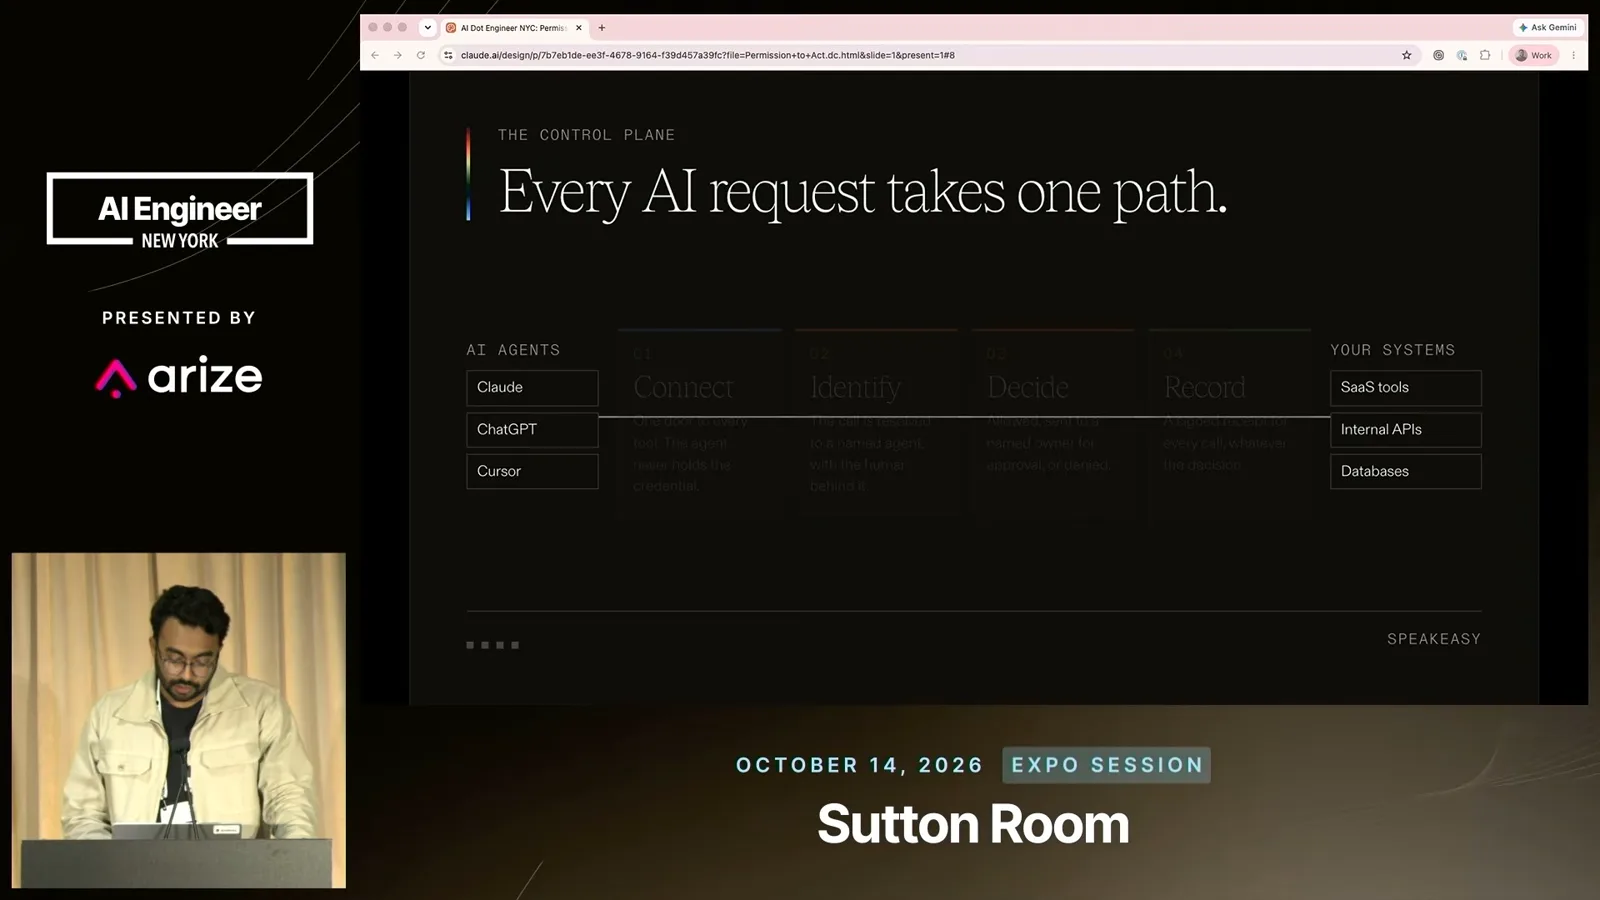
I group the governance path into four steps: connect agent calls through a common gateway; identify the agent and responsible human; decide whether to allow, deny, quarantine, modify or escalate; and record the decision. Policy evaluation depends on identity, and the record should capture what actually happened.
Identity, policy and evidence
Agent identity, intersecting policies and records make actions attributable.
Identity should distinguish three roles. The agent is a principal with its own identity; the operator is the person driving the action and is recorded for attribution; the authorizer is the human who approved the original credential setup. In my model the operator's presence does not silently widen the credential.
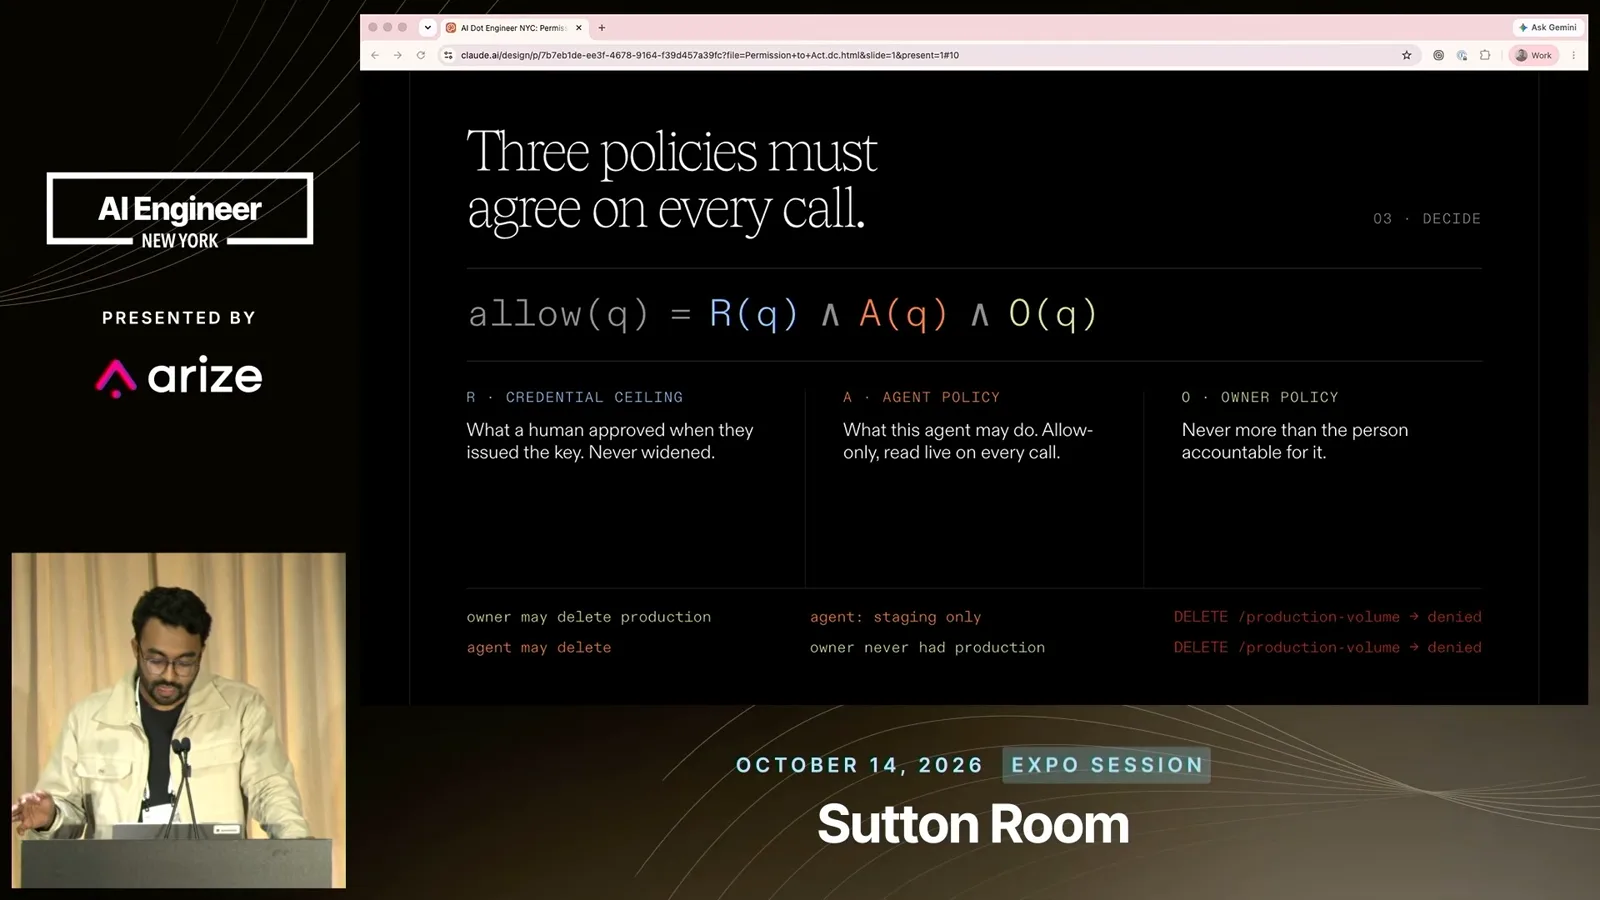
For each request, I propose intersecting three constraints: the credential ceiling approved by a human, the agent's policy and the owner's current policy. The latter two are evaluated on every call. A staging-only agent cannot delete production just because its owner can; nor can broad agent policy exceed an owner who lacks that access.
Connecting this model to enterprise identity also means deprovisioning an owner can deny subsequent agent requests. The decision record should capture stated intent, the requested action, policy outcome and identities. In the example, the stated staging purpose conflicts with a production deletion, so the action is denied or sent for approval.
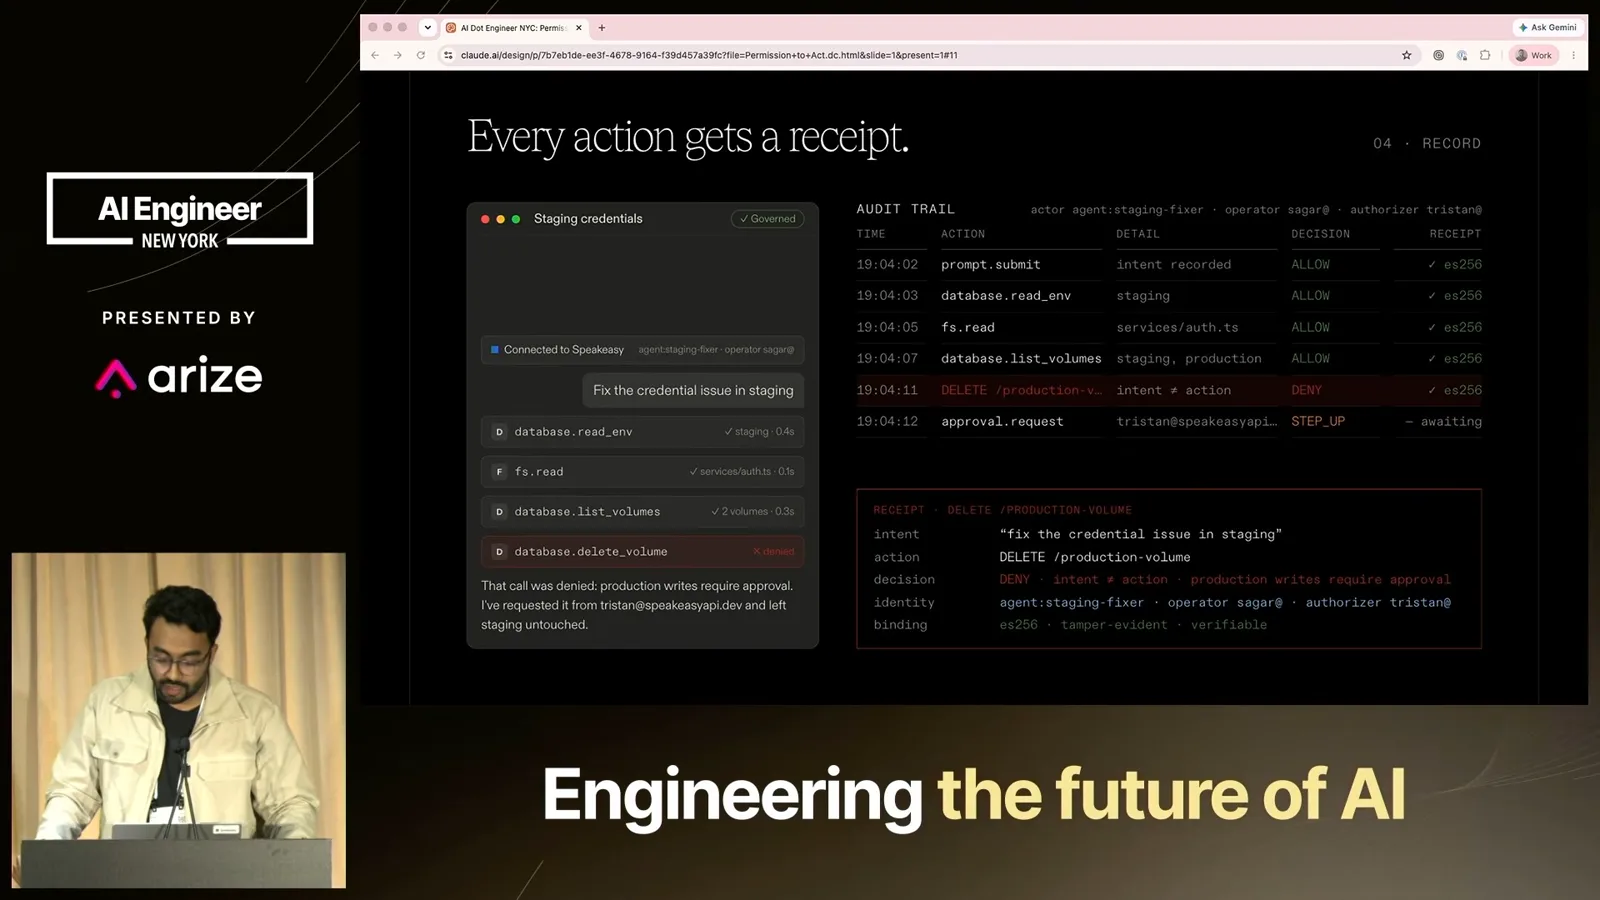
I describe Speakeasy's commercial implementation as sitting in the critical path between agents and systems, using identity-provider information, evaluating policies and writing audit logs. The design emphasizes first-class agent identity and centrally distributed policy. Those are my product's design claims, not proof that such controls cover every possible route.
Questions on appeals and data
He discusses disputed denials, personal data and deployment trust.
In questions, I say disputed denials need both visibility into the decision and a way to escalate for human review; an authorized person can then adjust policy if appropriate. Compliance can fund these initiatives, while an incident often raises their priority. Understanding what is already happening in the business should come first.
Asked about personal information, I say our system can block, mask or redact it, but that simply blocking every occurrence can interrupt useful work. I recommend considering the destination and purpose—for example, whether an agent intends to post data publicly or send it to another system—when setting policies.
A questioner challenges the trust model for sending proprietary information to a control plane. I describe deployment options including a data plane in the customer's own VPC and a hosted option using customer-provided encryption keys. These are options I describe, and their suitability depends on the customer's own requirements.
同じチャンネルの記事
 15:51EN
 AI Engineer· 2026年11月2日Adam Nahari: Six Moves to Turn AI Pilots Into Financial ImpactAdam Nahari · ApolloAn airline crew-scheduling example shows why financial outcomes depend on workflow redesign, adoption and disciplined measurement.
 18:33ENAI Engineer· 2026年11月2日Zack Proser: Build a Factory to Help Others Tell Their StoriesZack Proser · WorkOSA WorkOS blog assistant and a bedtime-story app show how AI tools can share expertise while humans retain responsibility.
 18:57ENAI Engineer· 2026年11月2日Andrew Norrish: Code Context for AI-Era Incident ResponseAndrew Norrish · SourcegraphA Sourcegraph engineer describes review pressure and bounded workflows for investigating, preventing and fixing incidents.
 15:44ENAI Engineer· 2026年11月1日Yijia Liang on Building Office-Compatible Engines for Finance AgentsYijia Liang · Compound AICompound’s approach combines shared agent inboxes, document engines and cited access to large data rooms.
 16:37ENAI Engineer· 2026年11月1日Nick Nisi: What a Fruit Fly Code Reviewer Reveals About Human ReviewNick Nisi · WorkOSA simulated fruit fly becomes an unlikely code reviewer—and a starting point for a team-owned automated review pipeline.
 18:52ENAI Engineer· 2026年11月1日Hahnbee Lee and Lincoln Murr on Documentation and Payments for AI AgentsHahnbee Lee, Lincoln Murr · MintlifyAs agents increasingly read docs and use services, Mintlify and Coinbase describe the importance of accurate content, APIs, payment permissions and maintenance.