En 30 segundos
Theo reviews Anthropic’s explanation of the June 2026 restrictions, reporting on government involvement, a lawsuit, and a bipartisan congressional inquiry. He questions whether restricting access to proprietary models addresses security risks when comparable open-weight models remain available. His predictions and judgments reflect what was known when the video was recorded.
- 1A launch followed by restrictionsFable 5 and Mythos 5 launched on June 9; Anthropic restricted access on June 12. Theo reviews reporting on the government’s involvement.
- 2The stated security concernAnthropic said the government provided oral evidence about a narrow potential jailbreak related to finding and fixing vulnerabilities in code.
- 3A legal and congressional responseLegion disputed the government’s authority in a lawsuit, while members of Congress requested an explanation of the legal and technical basis.
- 4The open-weight questionTheo points to a benchmark comparison and asks what limiting proprietary models achieves when other capable models remain available.
Conclusiones
- Anthropic said it suspended access to both models after a US government request related to cybersecurity concerns.
- Anthropic described a narrow potential jailbreak involving code analysis and vulnerability repair, while saying other models had similar capabilities.
- A lawsuit and a bipartisan congressional letter challenged or sought clarification about the government’s action; neither established a legal conclusion.
- Theo argues that restrictions on proprietary models must be evaluated alongside the availability of capable open-weight alternatives.
- At the time of recording, the timing and conditions of any restoration remained unclear.
Lee el texto editado por capítulos
A favorite model disappears
Theo describes losing access to Fable and the uncertainty around its return. He revisits the events following the two models’ release.
I miss Fable. At the time of this recording, it has been unavailable for 11 days, and despite promises of more information, we still do not have a clear explanation of when it might return. The uncertainty matters to people who had built it into their work.
Fable 5 and Mythos 5 were released on June 9, and access was restricted on June 12. Reports have filled in some pieces of the story, but a lot is still unclear. WIRED reported that the White House had asked Anthropic to revoke SK Telecom’s access to Mythos.
The reporting also discusses allegations about resale to China. Those allegations are not established facts. I can speculate about why the government was concerned, but speculation should not be confused with an explanation of the actual evidence or the legal basis for the action.
The cybersecurity explanation
Anthropic describes the government’s stated concern and its own decision to suspend access. Theo questions how the restriction addresses the underlying risks.
Anthropic says the government gave it oral evidence of a narrow potential jailbreak involving the models’ ability to read code and patch vulnerabilities. The company says other models have similar capabilities. That distinction matters: a claim about a particular risk is different from proof that these two models uniquely create it.
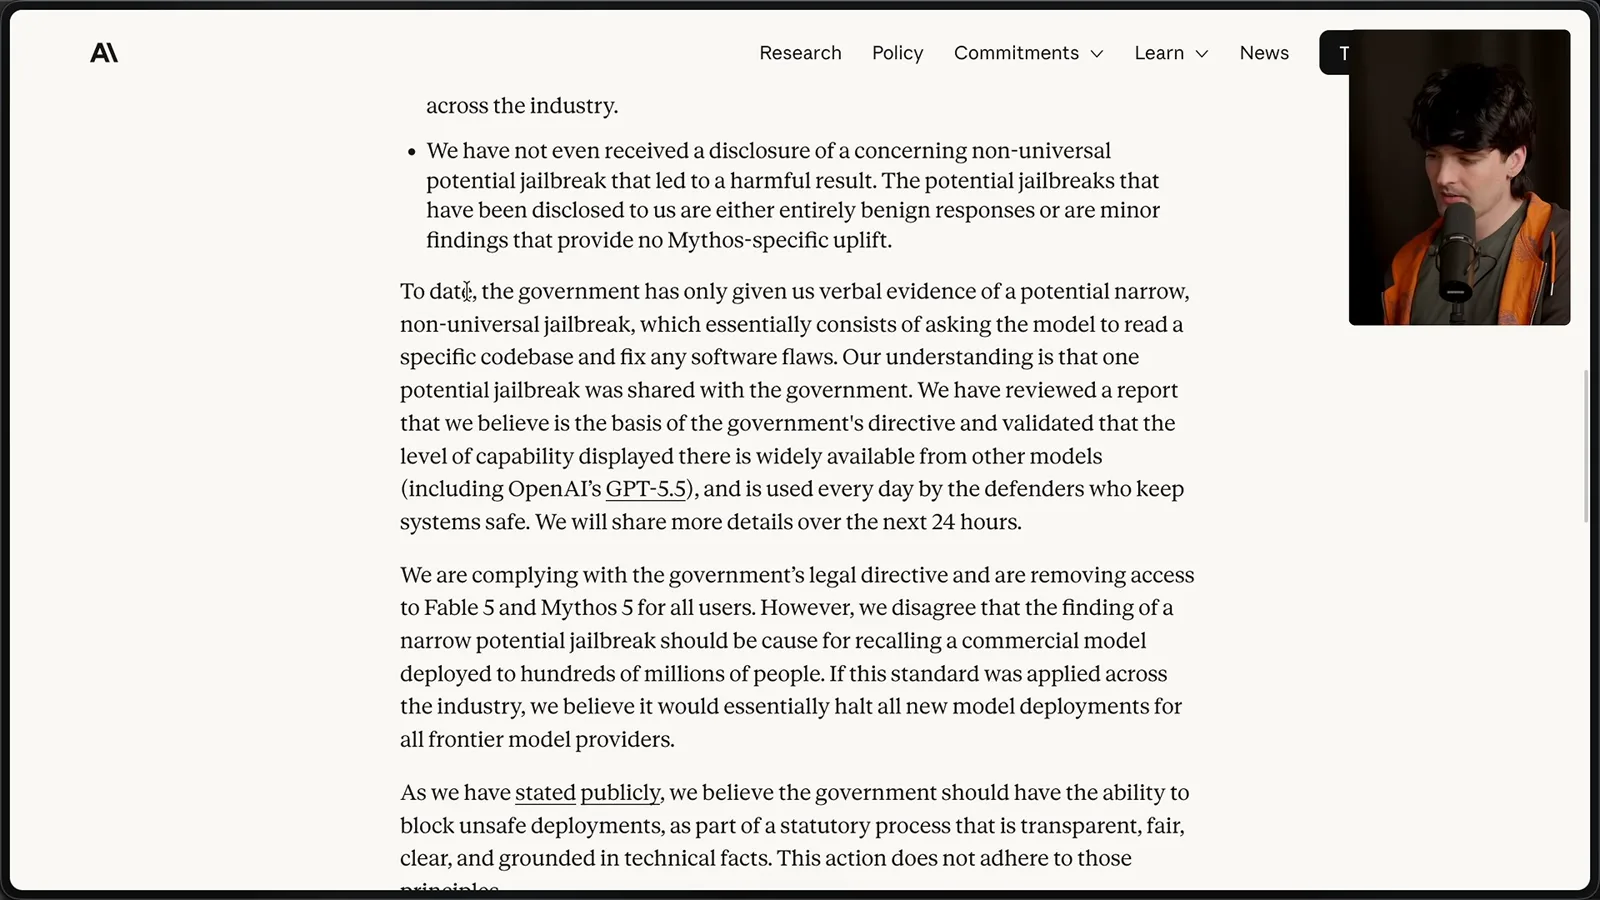
Finding and fixing vulnerabilities can help defenders, even though the same knowledge can have other uses. My instinct is that we should make systems more secure as quickly as we can. Simply taking a useful tool away does not make the underlying vulnerabilities disappear.
The public explanation leaves me wanting much more detail. If there is a specific risk, it would help to understand what makes it different from what other models can do and how the restriction is expected to reduce it. Without that context, developers have little way to assess the decision.
Anthropic says the government requested that it suspend access for foreign nationals, and that it chose to suspend access for everyone in order to comply. That is the company’s account of its decision, not an independent legal ruling on who was covered.
I can see how difficult it would be to verify every API user’s status and prevent access through intermediaries. A developer product can serve many users indirectly. That is my interpretation of the implementation problem, however, not a stated legal requirement from the government.
There has also been discussion of negotiations between Anthropic and the White House and rumors about what might happen next. I would be cautious about treating those rumors as confirmed. The situation remained unsettled when I recorded this video.
A lawsuit and congressional questions
A customer challenges the action in court, and a bipartisan group of representatives asks for details. Theo separates the claims and requests from established outcomes.
Legion filed a 43-page lawsuit challenging the action. The complaint argues that the Bureau of Industry and Security exceeded its authority and describes a 90-minute deadline. These are the plaintiff’s allegations; a complaint does not itself establish that the government acted unlawfully.
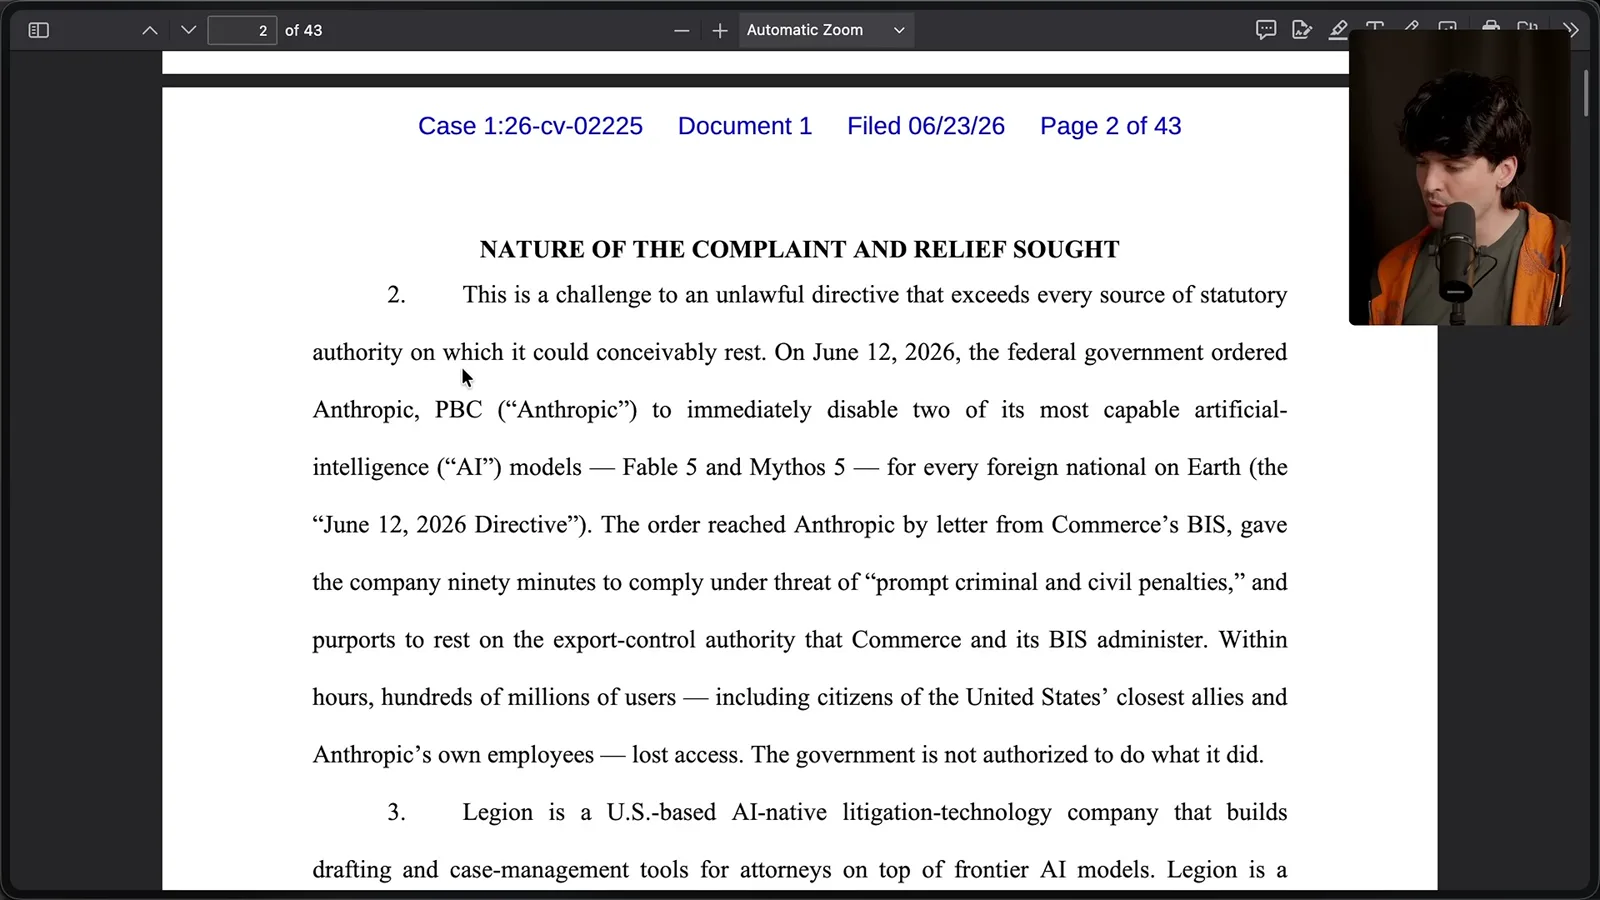
The company says the restriction harms its developers, including a developer in Canada. Its legal argument also invokes an exception for informational materials. Whatever one thinks of that argument, it is a claim for the court to consider, not a conclusion we can draw from the filing alone.
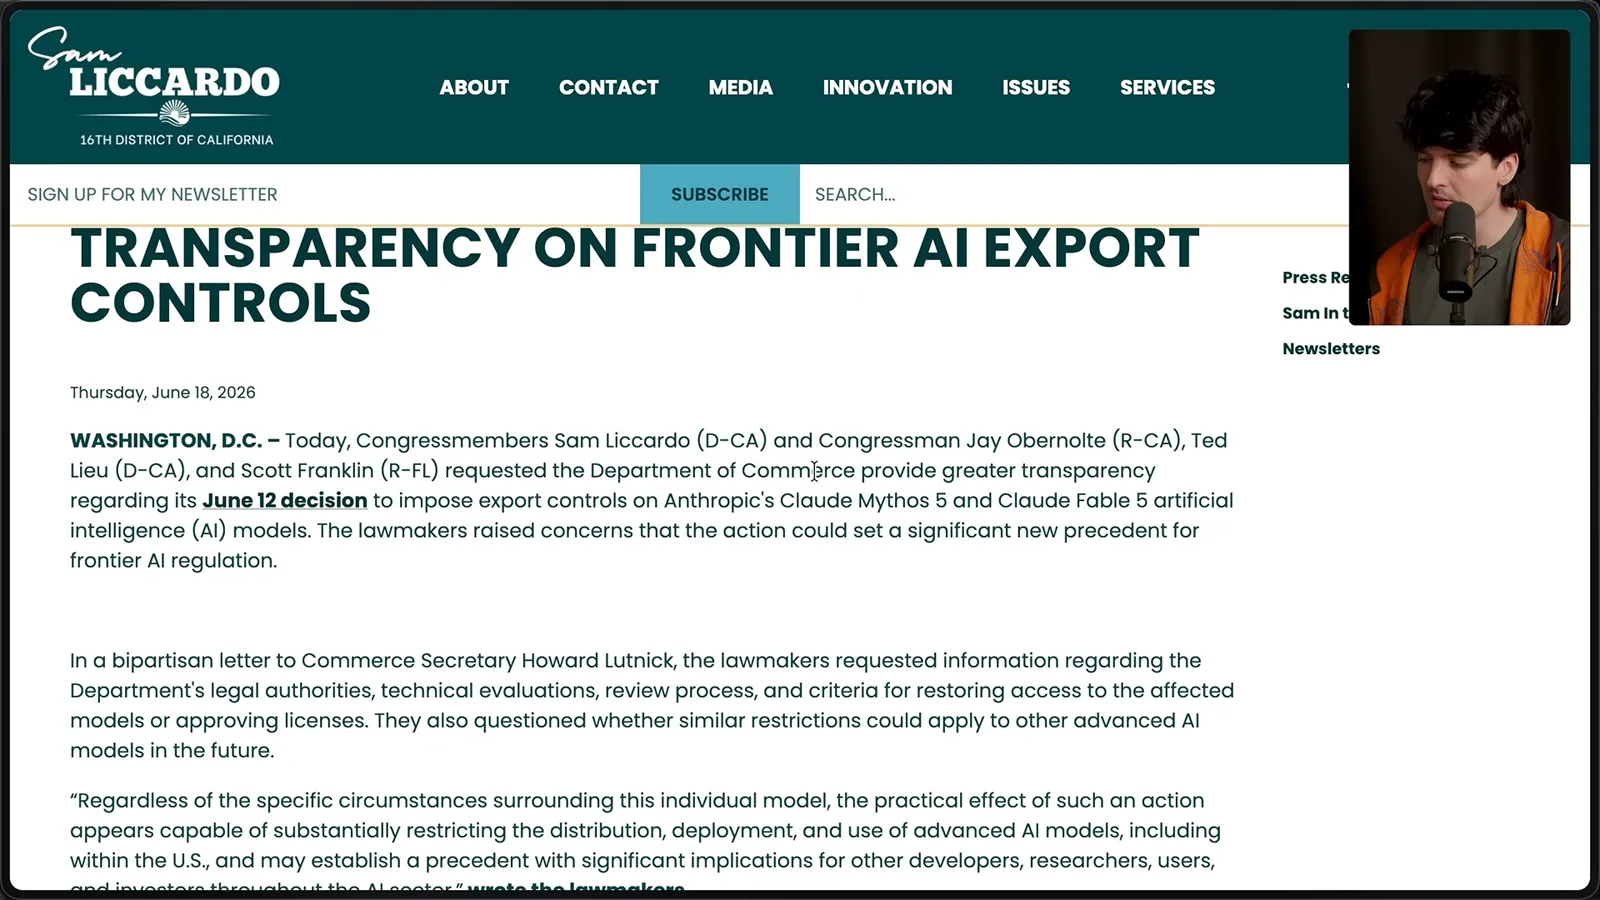
A bipartisan group of representatives—Sam Liccardo, Jay Obernolte, Ted Lieu, and Scott Franklin—also asked for answers. Their letter sought the legal basis and technical criteria behind the restrictions and requested a response by June 26. That kind of oversight is important when an action affects people’s access to widely used tools.
Open weights and the cost of restrictions
Theo compares benchmark results and argues that open-weight models complicate the policy. He closes with his concerns about transparency and future access.
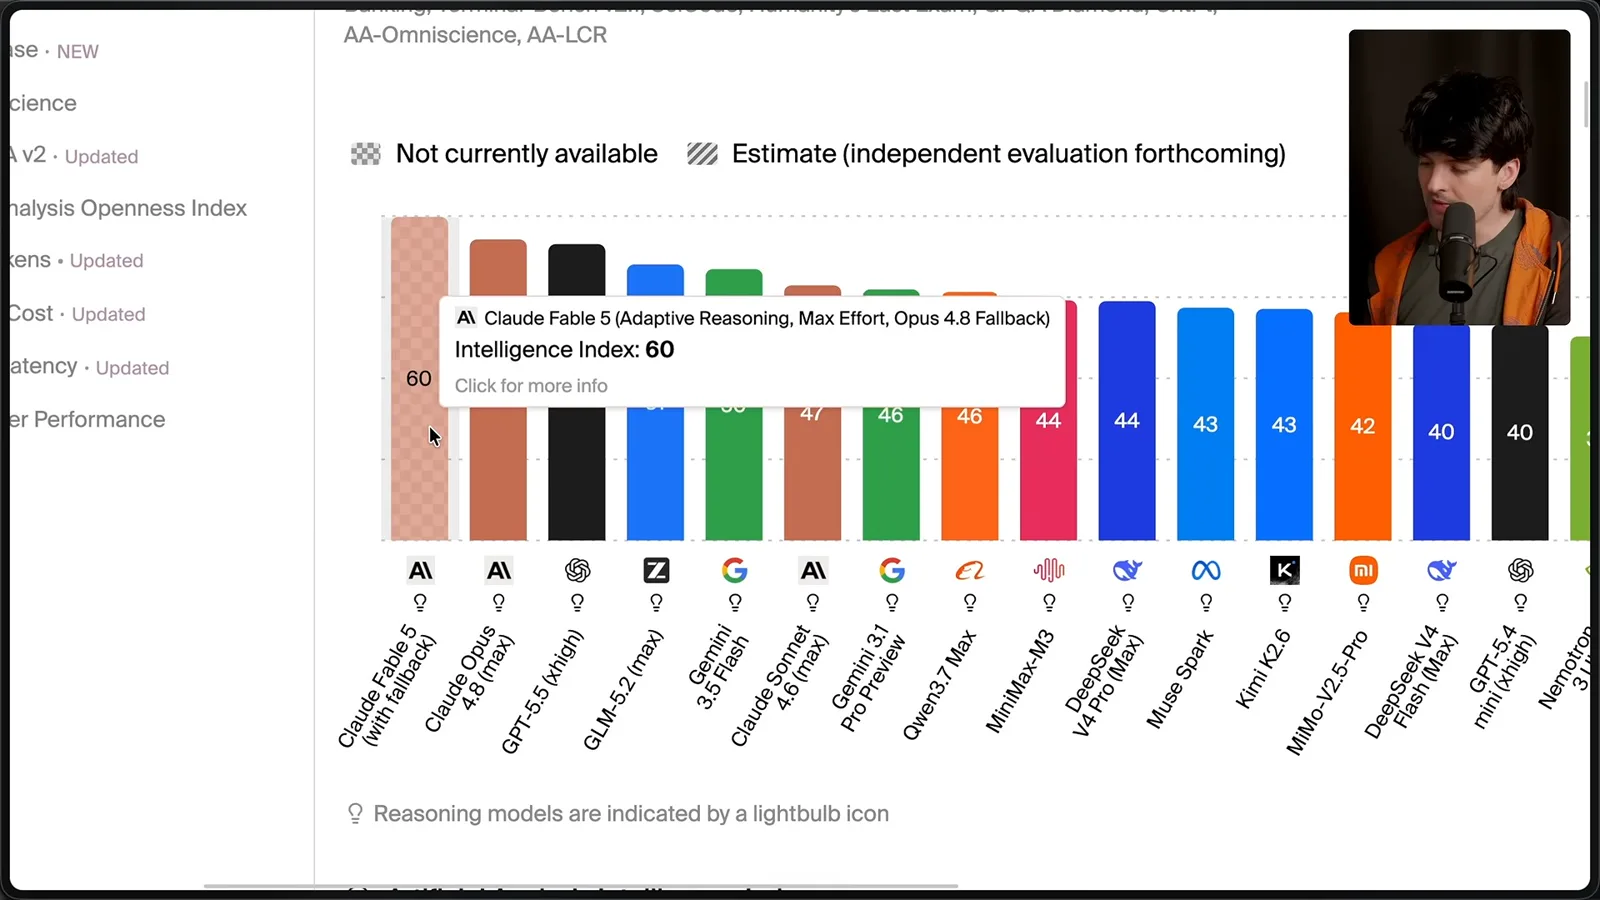
Consider the Artificial Analysis results I have on screen: Fable with an Opus fallback scores 60, Opus scores 56, and GLM 5.2 scores 51 on the displayed benchmark. This is one measurement, not a comprehensive ranking of every model or task, and the Fable result includes a fallback.
My concern is that capable open-weight models remain available while a proprietary model is restricted. If the stated objective is security, the policy needs to account for that reality. Otherwise the restriction can affect developers and the company providing the service without resolving the broader availability of comparable capabilities.
I also worry about the competitive effect. The landscape includes models developed and distributed in different countries, and access restrictions may change which tools developers choose. My view about the strategic consequences is a prediction, not evidence that a particular country or company caused this decision.
A government can have legitimate security concerns, but the public still needs an intelligible account of the action. What evidence supported it? What standard was applied? What would have to change for access to be restored? Those questions matter to customers making plans as well as to policymakers.
The congressional letter is a useful step because it asks for the reasoning rather than simply accepting the lack of detail. I hope the response makes the technical and legal basis clearer. For now, the available public information does not tell us when Fable will return.
I want a policy that takes security seriously while recognizing how these models are actually distributed and used. Until we get more information, my frustration is with both the loss of a tool I valued and the uncertainty around the decision.
Más de este canal
 38:47EN
 Theo - t3․gg· 28 oct 2026Theo’s Long-Running Agent Experiments: Verification, Compute and CostTheo Browne · Ping LabsA skateboard game and two compiler projects show how repeated checks and flexible compute can sustain agent work—and how expensive those loops can become.
 36:07ENTheo - t3․gg· 27 oct 2026Theo on Token Costs, Coding Agents, and the Price of AI CapabilityTheo Browne · Ping LabsA viral estimate of Lauren's AI spending prompts a closer look at cache pricing, benchmarks, and the changing work of coding agents.
 30:37ENTheo - t3․gg· 26 oct 2026Theo’s Three Skills for Reviewing and Shipping with Coding AgentsTheo Browne · Ping LabsHow sol-loop, full-send and full-stop encode review, verification and different levels of merge authority.
 0:43ENTheo - t3․gg· 23 oct 2026Theo Distinguishes Security Vulnerabilities from Active AttacksTheo Browne · Ping LabsA short explanation of why disclosed software flaws and reported attacks are different kinds of security news.
 29:22ENTheo - t3․gg· 22 oct 2026Theo on Security Vulnerabilities, Stolen API Keys and AITheo Browne · Ping LabsA look at the gap between vulnerability disclosure and patching, and a speculative account of why stolen inference keys may be valuable.
 31:13ENTheo - t3․gg· 20 oct 2026Theo on Why Smarter Models Help More Than DevelopersTheo Browne · Ping LabsFrom game modifications to compiler experiments, Theo revisits his assumptions about who benefits from more capable AI.