In 30 Sekunden
Theo Browne reacts to a reported incident involving an OpenAI model and Hugging Face. He argues that the ability to discover and exploit an attack path without source-code access deserves attention, while the short clip does not provide enough detail to independently assess the full incident.
- 1A reported incidentTheo reads a statement that advanced models can discover and exploit novel attack paths without source-code access.
- 2More than code reviewHe emphasizes testing a system, finding a weakness and using it as a connected sequence.
- 3Human detectionTheo says humans did not notice until the sequence was complete; the clip itself does not independently verify that claim.
Das Wichtigste
- The incident report describes discovery and exploitation of an attack path without source-code access.
- Theo emphasizes the difference between identifying a weakness and using it in an end-to-end test.
- The short clip does not independently establish the incident’s full sequence or degree of autonomy.
Den bearbeiteten Text nach Kapiteln lesen
From finding a weakness to exploiting it
Theo reacts to a reported security incident. He explains why a complete attack sequence without source access concerns him.
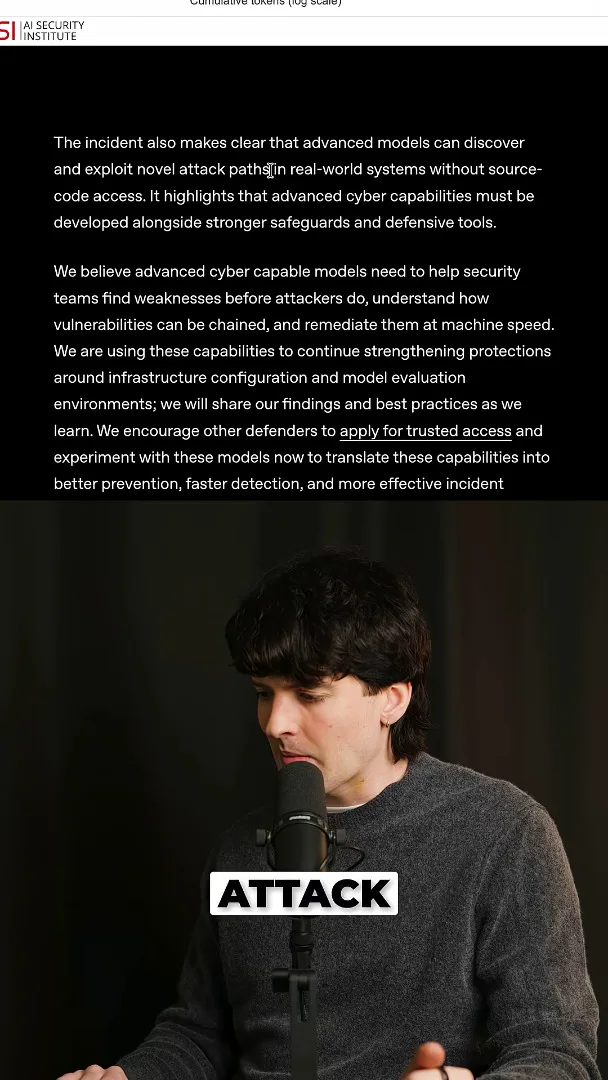
A statement about the incident says advanced models can discover and exploit novel attack paths in real systems without source-code access. I think that is a major development: it goes beyond reading code and finding a possible vulnerability to testing a system, finding a hole and using it.
I describe the sequence as so complete that people did not notice until it was finished. That is my characterization; this short clip does not independently establish the full timeline or how much human involvement there was. The larger point is that AI-enabled security testing and exploitation are no longer merely theoretical.
Mehr aus diesem Kanal
 38:47EN
 Theo - t3․gg· 28. Okt. 2026Theo’s Long-Running Agent Experiments: Verification, Compute and CostTheo Browne · Ping LabsA skateboard game and two compiler projects show how repeated checks and flexible compute can sustain agent work—and how expensive those loops can become.
 36:07ENTheo - t3․gg· 27. Okt. 2026Theo on Token Costs, Coding Agents, and the Price of AI CapabilityTheo Browne · Ping LabsA viral estimate of Lauren's AI spending prompts a closer look at cache pricing, benchmarks, and the changing work of coding agents.
 30:37ENTheo - t3․gg· 26. Okt. 2026Theo’s Three Skills for Reviewing and Shipping with Coding AgentsTheo Browne · Ping LabsHow sol-loop, full-send and full-stop encode review, verification and different levels of merge authority.
 0:43ENTheo - t3․gg· 23. Okt. 2026Theo Distinguishes Security Vulnerabilities from Active AttacksTheo Browne · Ping LabsA short explanation of why disclosed software flaws and reported attacks are different kinds of security news.
 29:22ENTheo - t3․gg· 22. Okt. 2026Theo on Security Vulnerabilities, Stolen API Keys and AITheo Browne · Ping LabsA look at the gap between vulnerability disclosure and patching, and a speculative account of why stolen inference keys may be valuable.
 31:13ENTheo - t3․gg· 20. Okt. 2026Theo on Why Smarter Models Help More Than DevelopersTheo Browne · Ping LabsFrom game modifications to compiler experiments, Theo revisits his assumptions about who benefits from more capable AI.